Security and Correctness in Wasmtime
Explore security measures in Wasmtime WebAssembly runtime, focusing on sandboxing, isolation, and implementation correctness to ensure safe execution of untrusted programs.
Sandboxing Your Sandbox: Leveraging Hypervisors for WebAssembly Security
Explore advanced techniques for securing Wasm applications using hypervisor-based sandboxing. Learn to address security challenges in multi-tenant environments and leverage hardware virtualization for robust application isolation.
Using WebAssembly to Run, Extend, and Secure Applications
Explore WebAssembly's evolution, security features, and applications beyond browsers. Learn to run, extend, and secure apps using WASM, WASI, and Trusted Execution Environments.
Application Security Testing Career Guide for 2024
Comprehensive guide to starting an Application Security career, covering fundamentals, programming, security concepts, tools, and certifications. Practical advice for building skills and avoiding information overload.
Cloud Native Apps with Server-Side WebAssembly
Explore server-side WebAssembly's potential to enhance security, portability, and simplicity in cloud-native apps. Live demo showcases deployment models and reference applications using wasmCloud, Krustlet, and Envoy.
Cloud Native Application Security with Open Source
Explore cloud native app security risks, identification methods, and open-source tools for risk mitigation in developer-friendly environments. Learn to integrate security into workflows.
Strategies for Secure Development with GraphQL
Explore strategies for building secure GraphQL APIs, including security as a core feature, developer tools for secure applications, and effective request logging techniques.
Protect Secret Keys in Jamstack Apps - Learn With Jason
Learn to secure API keys in Jamstack apps using Postman for rapid prototyping and development. Explore techniques for protecting sensitive data while building secure and efficient web applications.
Rapid Assessment of Service and Application Security - Application Design and Architecture
Learn a rapid methodology to assess application security, identify vulnerabilities, and improve overall security posture. Gain practical skills to evaluate design and architecture, even with limited resources.
Android Security Enhancements in Versions M and N
Explore Android M and N's enhanced security features, including boot process verification, runtime hardening, and data protection. Learn to implement new security APIs and best practices for app development.
The Anatomy of Java Vulnerabilities
Explore Java vulnerabilities, their management, and defense strategies. Learn about attack vectors, reporting processes, and effective methods to enhance code security against cyber threats.

MVC 1.0 - Building Secure and Flexible Web Applications
Explore MVC 1.0 fundamentals, core concepts, and practical implementation for building secure, flexible web applications. Includes code samples and tooling support demonstration.

Java First, Java Always - The Future of Java Development
Explore Java's enduring impact on modern app development, Oracle's stewardship, and the importance of clean code for secure applications in this JavaOne keynote.
Modern Application Development with Java and GraalVM Enterprise
Explore GraalVM and Java SE Subscription's potential to drive innovation while maintaining efficiency in critical applications, balancing business continuity with growth opportunities.
Secure Coding Guidelines for Java SE - Overview and Best Practices
Learn essential Java secure coding practices to prevent vulnerabilities. Covers guidelines, real-world examples like Log4Shell, and practical tips for implementing security throughout the development process.
Pipeline Pandemonium - Hijacking Cloud Security Through CI/CD Vulnerabilities
Explore CI/CD pipeline vulnerabilities in cloud environments, examining real-world examples of security risks and exploitation techniques in GitHub, CircleCI, and Jenkins.
Root Canal Static Analysis Audit of Zephyr
Comprehensive static analysis audit of Zephyr's code quality, revealing deeper security vulnerabilities beyond standard linters. Insights on advanced bug detection and fixing processes for critical open-source projects.
Don't Get Burned! Secure Coding Essentials to Protect Your Application
Explore common security pitfalls in coding and learn practical tips to write secure, bulletproof applications. Covers input validation, injection, file overwrites, and arbitrary code execution with real-world examples.
Using WebAssembly to Run, Extend, and Secure Your .NET Application - Niels Tanis - NDC Porto 2023
Explore WebAssembly's evolution, security features, and integration with .NET. Learn to run and extend applications, leverage sandboxing, and enhance security using Trusted Execution Environments.
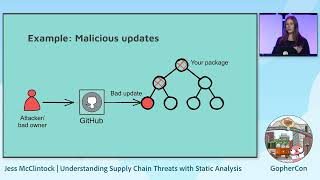
Understanding Supply Chain Threats with Static Analysis - GopherCon 2023
Explore a CLI tool for Go that detects privileged permissions in package dependencies, enhancing security and preventing supply chain attacks.
Maximizing Security with JDK - Understanding Built-in Capabilities
Explore JDK's native security features, including cryptography and post-quantum enhancements, to simplify development and strengthen application security through live coding demonstrations.