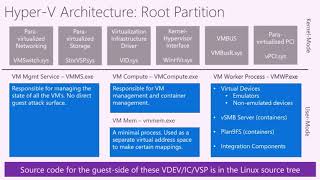
A Dive into Hyper-V Architecture and Vulnerabilities
Explore Hyper-V architecture, vulnerabilities, and security implications in virtualization technology. Gain insights into guest-to-host exploits and platform security challenges.
Breaking the Attack Graph - How to Leverage Graphs to Strengthen Security in a Domain Environment
Explore how defenders can leverage graph-based thinking to strengthen security in domain environments, adapting to sophisticated attackers and enhancing prevention, detection, and investigation strategies.
Exploiting the Hyper-V IDE Emulator to Escape the Virtual Machine
Explore a critical Hyper-V vulnerability, its exploitation on Windows Server 2012R2, and learn about virtualization security, memory manipulation, and payload strategies in this technical deep dive.
The Active Directory Botnet
Explore how botnets and C&C servers can infiltrate organizations, bypass network controls, and render security measures ineffective, with a focus on Active Directory vulnerabilities.
Top Active Directory Attacks - Understand, then Prevent and Detect
Explore common Active Directory attacks, prevention strategies, and detection methods. Learn to secure enterprise networks against prevalent hacking techniques and enhance cybersecurity practices.
The Great Sandbox Escape
Explore novel ransomware techniques, including virtual machine deployment for attacks. Learn about attacker strategies, detection methods, and cybersecurity insights from a malware specialist.
PowerShell Exploitation - PowerSploit - Bloodhound - PowerShellMafia - Obfuscation
Explore PowerShell exploitation techniques, including obfuscation and malware tactics. Learn to analyze logs, detect suspicious activities, and implement effective security measures.
Kerberoasting Revisited
Explore advanced Kerberoasting techniques, encryption types, and defenses. Learn about the "tgtdeleg" trick and Rubeus for improved Kerberoasting in this cybersecurity deep dive.
Attacking Azure Environments with PowerShell
Learn to exploit Azure environments using PowerShell, covering data dumping, modules, and various services. Gain insights into escalation techniques and practical demonstrations.
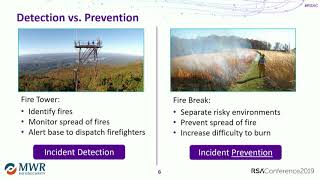
Future Forests - Realistic Strategies for AD Security & Red Forest Architecture
Strategies for implementing Microsoft's Red Forest architecture to mitigate Active Directory attacks, covering benefits, challenges, and practical steps for enhanced security in enterprise domains.
CrackMapExec Owning Active Directory by Using Active Directory
Explore Active Directory exploitation using CrackMapExec. Learn libraries, authentication, payload modules, and execution techniques for effective penetration testing and security assessment.
Active Directory Real Defense for Domain Admins
Learn practical strategies to secure Active Directory, including limiting Domain Admin accounts, setting logon restrictions, and implementing best practices for enhanced network protection.
Active Directory - Real Defense for Domain Admins
Practical strategies for securing Domain Admins and Domain Controllers in Active Directory environments, including account management, password policies, and logon restrictions.
Windows Event Logs - Zero to Hero
Comprehensive guide to Windows Event Logs, covering forwarding, analysis, and practical applications in cybersecurity, with real-world examples and best practices.
Deploying PAWs as Part of a Strategy to Limit Credential Theft and Lateral Movement
Explore strategies to limit credential theft and lateral movement using Privileged Access Workstations (PAWs), including deployment models, Active Directory setup, and network segmentation.
The Devopsification of Windows Server 2016
Explore Windows Server 2016's DevOps-centric features, including NanoServer, DSC, OneGet, and containers. Learn how these innovations enable cloud-paced workflows and enhance security, deployment, and management.
Lessons Learned from a Ransomware Attack
Comprehensive analysis of a real-world ransomware attack on a school district, covering timeline, damage, recovery, and preventive measures for future cybersecurity preparedness.
Recertifying Active Directory Certificate Services
Explore AD CS vulnerabilities, attack vectors, and defense strategies for securing Microsoft's PKI implementation. Learn escalation scenarios, auditing techniques, and incident response.
Certified Pre-Owned - Abusing Active Directory Certificate Services
Explore AD CS vulnerabilities for credential theft, persistence, and domain escalation. Learn offensive and defensive techniques to secure Active Directory PKI implementations.
Threat Hunting in Active Directory Environment
Explore advanced threat hunting techniques in Active Directory, focusing on attacker persistence methods, privilege escalation, and covert system control. Learn to detect and mitigate sophisticated APT threats.
Is This My Domain Controller? A New Class of Active Directory Protocol Injection Attacks
Explore new Active Directory protocol injection attacks, focusing on NTLM and Kerberos vulnerabilities. Learn about attack scenarios, mitigation strategies, and essential tips for defenders.