From Strong to Stronger: Phishing Resistant Authentication Methods - BRK244
Explore phishing-resistant authentication methods like FIDO2 and Windows Hello, their inner workings, deployment strategies, and benefits over traditional MFA for enhanced security and user protection.
Digital Perspectives - A Holistic Approach in Bringing Accessibility by Angela Suriyakumaran
Explore holistic approaches to enhance digital accessibility in biosciences education, promoting inclusivity and diversity in learning environments.
Start with the BPT Then Worry About the APT - Lecture 1
Explore essential cybersecurity strategies, from basic protection techniques to advanced memory analysis, covering various systems and devices for comprehensive digital defense.

Attacking Drupal - Security Vulnerabilities and Exploitation Techniques
Explore techniques for exploiting vulnerabilities in Drupal websites, focusing on common attack vectors and security weaknesses in this popular CMS platform.
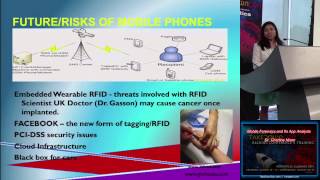
Mobile Forensics and App Analysis - Lecture 9
Explore mobile forensics and app analysis techniques, focusing on Android, Facebook, NFC, and privacy concerns. Learn about emerging mobile technologies and their security implications.

How to Securely Store Passwords in Databases
Learn to securely hash and store passwords in databases using a free template app. Gain practical skills in implementing robust password security measures for your web applications.
How to Bypass Sophisticated Anti-Bot Systems
Learn techniques to bypass advanced anti-bot systems, enhancing your understanding of web security and automation challenges in modern web development.
Abstracting TEE Silicon Implementations with Shims
Explore TEE silicon abstraction using shims, covering Anarchs, WebAssembly, runtime portability, and trusted computing. Learn deployment strategies and how to contribute to this innovative technology.
Application Penetration Testing
Learn application penetration testing techniques and methodologies to identify vulnerabilities and secure web applications effectively.
Webshells - History, Techniques, and Obfuscation
Explore webshell history, techniques, and obfuscation methods in this comprehensive talk by Adrian Crenshaw, covering essential cybersecurity concepts for IT professionals and security enthusiasts.
Web Penetration Testing Workshop: Uploading a Web Shell via SQL Injection - Part 3
Explore SQL injection techniques to upload web shells, enhancing your penetration testing skills in this hands-on workshop segment led by security expert Jeremy Druin.

Fun with WebSockets Using Socket Puppet
Explore WebSocket technology and its security implications using Socket Puppet. Learn practical techniques for testing and exploiting WebSocket vulnerabilities in web applications.

Crunching the Top 10,000 Websites' Password Policies and Controls
Analysis of password policies across top 10,000 websites, revealing trends and best practices in online security. Insights for improving authentication systems and user protection.
Mirror Mirror - Reflected PDF Attacks Using SQL Injection
Explore innovative techniques for exploiting SQL injection vulnerabilities to launch reflected PDF attacks, enhancing your understanding of web application security.
Burp Suite: Informing the 99% of What the 1%ers Know - Lecture 1.2.4
Explore advanced techniques and insights for using Burp Suite, a popular web application security testing tool, to enhance your penetration testing and vulnerability assessment skills.
HTML5 Security Vulnerabilities and Attacks - Taking a Byte Out of HTML5
Explore HTML5 security vulnerabilities and attacks, including client-side threats, browser support issues, and defensive strategies using the SHARK repository and testing environment.
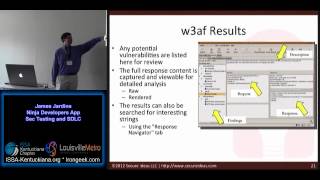
Application Security Testing and SDLC for Developers
Learn app security testing techniques and tools for the software development lifecycle, including reconnaissance, mapping, vulnerability assessment, and exploitation.
Embedded Malicious JavaScript - Outerz0ne 2009
Explore techniques for embedding malicious JavaScript in web applications, understanding potential vulnerabilities and security risks in modern web development.
OSInt, Cyberstalking, Footprinting and Recon: Getting to Know You - Part 3 Metadata and Miscellaneous Topics
Explore metadata, file formats, and EXIF information for effective digital footprinting and reconnaissance. Learn practical tools and techniques for gathering valuable intelligence.
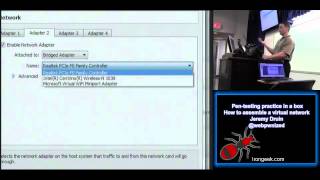
Pen-Testing Practice in a Box: Assembling a Virtual Network
Learn to set up a virtual network for penetration testing practice, covering VirtualBox installation, VM configuration, networking options, and installing essential tools and environments.
Build a Micro HTTP Server for Embedded Systems
Implement a lightweight HTTP server for embedded systems, covering design principles, Python prototyping, C implementation, and integration with RTOS on an STM32F4-Discovery board.