Tangled Web: Defense in Deception - 2017
Explore defensive deception strategies for web applications, including tools and techniques to detect, confuse, and corral attackers. Learn to plan, execute, and monitor effective deception in cybersecurity.
Take Control of and Secure Your Passwords Using Vaultwarden on Portainer
Learn to set up and secure a self-hosted password manager using Vaultwarden on Portainer, covering installation, configuration, and integration with browsers for enhanced password security.
Broken CAPTCHAs and Fractured Equity - Privacy and Security in hCaptcha's Accessibility Workflow
Exploring hCaptcha's accessibility workflow, its privacy implications, and security vulnerabilities. Discusses the future of CAPTCHAs and the challenge of balancing inclusivity with security in online verification systems.
2019 OWASP Top 10 - Part 1
Comprehensive exploration of the first half of OWASP Top 10, covering critical web application security risks and effective mitigation strategies for developers and security professionals.
Brains Can Be Hacked - Why Should You Care and How to Prevent It
Explore potential security risks of brain-computer interfaces and surgical robots, and learn mitigation strategies based on unique user interactions with these systems.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
OWASP Top 10 Training - Part 1
Comprehensive overview of OWASP Top 10 security vulnerabilities, focusing on identification, prevention, and mitigation strategies for web application developers and security professionals.
OWASP Top 10 Security Risks - Part 5
Explore the latest OWASP Top 10 security vulnerabilities, their impact, and effective mitigation strategies to enhance web application security and protect against common threats.
HoneyPy and HoneyDB: Leveraging Honeypots for Network Security - 2016
Explore honeypots, HoneyPy, and HoneyDB for network security. Learn about low-interaction honeypots, threat detection, and leveraging honeypot data to enhance organizational cybersecurity defenses.
API Security Best Practices and Guidelines - 2016
Explore industry-leading best practices for designing secure APIs, navigating standards, and protecting both public and private APIs to maximize benefits while keeping threats at bay.
Heike Winschiers Theophilus - Bridging Worlds: Indigenous Knowledge in the Digital World - Talk
Explore the integration of Indigenous knowledge in digital spaces, addressing challenges and proposing innovative solutions for inclusive representation and preservation.
Laravel API Crash Course With Sanctum - How to Build Laravel API
Comprehensive tutorial on building secure APIs with Laravel Sanctum, covering setup, authentication, route protection, and CRUD operations for a task management system.

How to Use Broadcasting in Laravel - What Is Broadcasting in Laravel
Learn to implement real-time event sharing between server-side Laravel and client-side JavaScript using broadcasting, with step-by-step guidance on setup, configuration, and practical implementation.
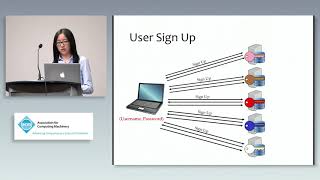
PASTA - Password-Based Threshold Authentication
Explore password-based threshold authentication with PASTA, a novel framework distributing identity verification among servers for enhanced security against token forgery and offline attacks.
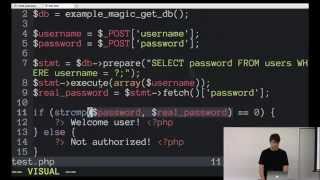
Input Sanitization - Peter Faiman
Learn essential techniques for validating user input, protecting against common vulnerabilities, and developing a security-focused mindset to safeguard your applications from malicious or unintended user actions.
Web Attacks
Explore common web vulnerabilities and attack methods, including discovery techniques, backdoors, weak passwords, and injection attacks, to enhance your cybersecurity knowledge.
Cross Origin Resource Sharing - Explained by Example
Explains CORS errors and solutions through practical examples, covering common issues like missing headers, preflight requests, and content-type restrictions.
Introduction to Web Infrastructures - Security and Network Forensics Lecture 11
Explore web infrastructure security: identity management, authentication methods, access control, and federated systems. Gain insights into SOAP, LDAP, Radius, Kerberos, and more.
sa.FIRE Cloud4Health Studio Demonstration
Explore sa.FIRE Studio's interface, ontology, policy creation, retrieval, and revocation in this Cloud4Health demonstration by Dr Lu Fan.
Security Scan with Nessus - Comprehensive Guide
Learn to perform security scans using Nessus, covering policy creation, scanning techniques, and interpreting results for various systems including web servers and Windows.
The Beauty of the Internet Protocol
Explore the elegance of the Internet Protocol, its role in routing, addressing, and enabling VPNs. Learn about IP addresses, network routing, and the protocol's impact on modern communication.