Creating Accessible Security Testing with ZAP - AppSecCali 2019 Lightning Talk
Introducing OWASP ZAP's Heads Up Display: A new UI that makes security testing more intuitive for developers and professionals, enabling efficient use of the attack proxy tool.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface, and learn to integrate security testing into CI/CD pipelines for effective DevOps practices.
HTTPS Security Headers: HSTS, TLS, HPKP, and CSP Implementation - APPSEC CA 2017
Comprehensive guide to implementing HTTPS using HSTS, TLS, HPKP, and CSP. Learn best practices for secure web communication from Salesforce security experts.
DASTProxy: Automated Security Testing Focused on Business Context
Explore DASTProxy: a tool for automated security testing that focuses on business context rather than crawling, enhancing efficiency and effectiveness in application security assessments.
Monitoring Application Attack Surface to Integrate Security into DevOps Pipelines
Explore integrating security into DevOps pipelines through application attack surface monitoring. Learn strategies from a recognized expert to enhance your organization's software security practices.
Application Security California 2017 - Keynote Address
Explore cutting-edge application security insights and strategies with industry expert Chenxi Wang in this OWASP Foundation presentation from AppSec California 2017.
Rhyming with Hacks - The Ballad of Supply Chain Attacks
Explore supply chain attacks, their anatomy, and prevention strategies. Learn about real-life examples, existing solutions, and a new DOM monitoring approach with live demonstration.
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
Stop the Looters: Method to Detect Digital Skimming Attacks
Discover a method to detect and prevent digital skimming attacks on websites, protecting sensitive customer data from theft by malicious actors like Magecart.
OWASP Top 10 Privacy Risks 2021 - Understanding and Mitigating Web Application Privacy Threats
Explore OWASP's updated Top 10 Privacy Risks for web applications, covering vulnerabilities, consent issues, and data quality. Learn countermeasures to build a more private digital future.
Good Bot, Bad Bot: Characterizing Automated Browsing Activity
Explore Aristeus, a system for deploying honeysites to study malicious bot behavior. Learn about bot traffic patterns, attack strategies, and the importance of understanding automated browsing activity for web security.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
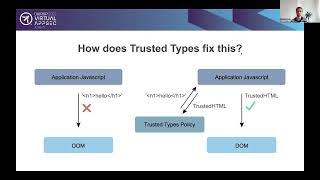
Trusted Types: A World Without XSS
Explore cutting-edge web security with Trusted Types, a powerful defense against XSS attacks. Learn implementation strategies and best practices from industry experts.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
OWASP Web Honeypot Project
Explore web application security through honeypot technology. Learn deployment strategies, data analysis, and threat intelligence gathering to enhance your cybersecurity defenses.
Common Application Security Mistakes Enabling Automated Attacks
Explore common security flaws enabling automated attacks on applications, including retail fraud and account takeovers. Learn from real-world examples and discover effective prevention strategies.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
2013 AppSec Guide and CISO Survey - Making OWASP Visible to CISOs
Insights from OWASP's 2013 AppSec Guide and CISO Survey, focusing on application security governance, risk management, and investment strategies for Chief Information Security Officers.