2019 OWASP Top 10 - Part 1
Comprehensive exploration of the first half of OWASP Top 10, covering critical web application security risks and effective mitigation strategies for developers and security professionals.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
OWASP Top 10 Training - Part 1
Comprehensive overview of OWASP Top 10 security vulnerabilities, focusing on identification, prevention, and mitigation strategies for web application developers and security professionals.
OWASP Top 10 Security Risks - Part 5
Explore the latest OWASP Top 10 security vulnerabilities, their impact, and effective mitigation strategies to enhance web application security and protect against common threats.
Start with the BPT Then Worry About the APT - Lecture 1
Explore essential cybersecurity strategies, from basic protection techniques to advanced memory analysis, covering various systems and devices for comprehensive digital defense.
Application Penetration Testing
Learn application penetration testing techniques and methodologies to identify vulnerabilities and secure web applications effectively.
Webshells - History, Techniques, and Obfuscation
Explore webshell history, techniques, and obfuscation methods in this comprehensive talk by Adrian Crenshaw, covering essential cybersecurity concepts for IT professionals and security enthusiasts.
Web Penetration Testing Workshop: Uploading a Web Shell via SQL Injection - Part 3
Explore SQL injection techniques to upload web shells, enhancing your penetration testing skills in this hands-on workshop segment led by security expert Jeremy Druin.
Mirror Mirror - Reflected PDF Attacks Using SQL Injection
Explore innovative techniques for exploiting SQL injection vulnerabilities to launch reflected PDF attacks, enhancing your understanding of web application security.
Burp Suite: Informing the 99% of What the 1%ers Know - Lecture 1.2.4
Explore advanced techniques and insights for using Burp Suite, a popular web application security testing tool, to enhance your penetration testing and vulnerability assessment skills.
HTML5 Security Vulnerabilities and Attacks - Taking a Byte Out of HTML5
Explore HTML5 security vulnerabilities and attacks, including client-side threats, browser support issues, and defensive strategies using the SHARK repository and testing environment.
MarkDoom: How I Hacked Every Major IDE in 2 Weeks
Explore how major IDEs were hacked through embedded browsers, revealing critical security vulnerabilities in desktop applications built with web technologies. Learn about the risks and safeguards in the "Desktop Web" era.
OWASP Top 10 - Application Security Risks
Explore the latest OWASP Top 10 web application security risks with expert Andrew van der Stock. Learn about critical vulnerabilities and effective mitigation strategies for safer software development.
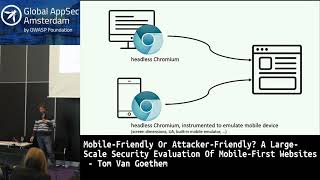
Mobile-First Websites Security Evaluation - Attacker-Friendly or User-Friendly?
Evaluate security vulnerabilities in mobile-first websites, exploring potential risks and attacker-friendly features. Learn to identify and mitigate threats in mobile web development.
AppSec Challenges - Overcoming Framework Limitations and Building Robust Security
Exploring challenges in application security, analyzing framework limitations, and discussing robust approaches to improve security at scale while making it more manageable.
DNS Hijacking Using Cloud Providers: No Verification Needed - AppSec EU 2017
Explore advanced domain hijacking techniques, including undisclosed methods, to understand vulnerabilities in DNS providers and cloud services. Learn to identify and mitigate risks beyond common subdomain takeover scenarios.
OWASP Zap - Introduction and Usage Guide
Explore OWASP Zap's capabilities for web application security testing with David Scrobonia's comprehensive overview, highlighting key features and best practices for effective vulnerability detection.
Monitoring Application Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface evolution, and learn to integrate security testing into CI/CD pipelines using metrics-based policies.
Popular Approaches to Preventing Code Injection Attacks are Dangerously Wrong
Explores limitations of current code injection prevention methods and introduces Name Space Layout Randomization (NSLR) as a novel approach to secure Java applications against known and zero-day vulnerabilities.
Detecting CSRF Vulnerability Reliably - Programmatic Approach
Explore a programmatic approach to reliably detect CSRF vulnerabilities in web applications, overcoming common shortcomings of existing tools and improving automated security testing.
Remediating XSS in GitHub Open Source Projects - Lessons Learned
Insights on scaling XSS remediation across GitHub open source projects, focusing on risk reduction, adding security controls, and automating code modification for diverse applications.