Windows 2003 - Web Application Security
Explore web application security vulnerabilities and defense strategies for Windows 2003 servers, focusing on practical techniques and real-world scenarios.
Web Application Security and Release of "WhiteHat Arsenal"
Explore web application security and the "WhiteHat Arsenal" tool, focusing on vulnerabilities, attack methods, and defensive strategies for Windows systems.
Live Hacking - Breaking into Your Web App
Live hacking session demonstrating vulnerabilities in open source dependencies. Explores real-world exploits, their impacts, and solutions to enhance application security through DevSecOps practices.
The Hidden XSS - Attacking the Desktop
Explore hidden XSS vulnerabilities in desktop applications, focusing on Skype, WebOS, and Android. Learn attack techniques and implications for security.
OWASP Top 10 of 2013 - It's Still a Thing and We're Still Not Getting It
Explore OWASP Top 10 vulnerabilities from 2013, their ongoing relevance, and why organizations struggle to address them effectively in web application security.
Burp for All Languages
Learn to leverage Burp Suite for web application security testing across various programming languages with expert insights and practical techniques.
Exploiting Browsers Like A Boss
Learn advanced browser exploitation techniques and strategies for identifying vulnerabilities in web applications from cybersecurity expert Bryce Kunz.
NoSQL Injections - Moving Beyond or 11
Explore advanced NoSQL injection techniques and defense strategies with expert Matt Bromiley, moving beyond basic vulnerabilities to enhance database security.
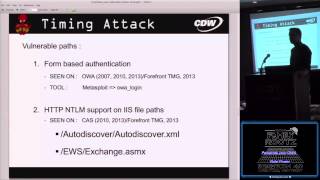
Penetrate Your OWA
Explore techniques for penetrating Outlook Web Access (OWA) and enhancing your security testing capabilities in this informative DerbyCon 4 presentation.

CMS Hacking Tricks
Explore advanced techniques for exploiting content management systems, uncovering vulnerabilities, and enhancing web application security.
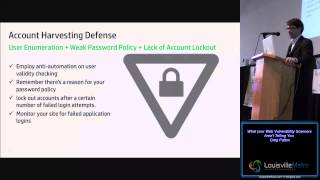
What Your Web Vulnerability Scanners Aren't Telling You
Explore common web vulnerabilities often missed by automated scanners, including logic flaws, authentication issues, and access control problems. Learn defensive strategies for better web security.
OWASP 2014 Top 10 Proactive Web Application Controls
Explore proactive web application security controls, focusing on preventing SQL injection, XSS attacks, and implementing robust access controls and password policies.
Mutillidae Jeremy Druin Part 2
Learn to install and configure Mutillidae, explore security levels, and understand OWASP Top 10 vulnerabilities with expert guidance from Jeremy Druin.
Running Away from Security - Web App Vulnerabilities and OSINT Collide
Explore the intersection of web app vulnerabilities and OSINT techniques, uncovering potential security risks and learning effective mitigation strategies.
Wielding BurpSuite - Quick Start Your Extensions and Automation Rules
Learn to create BurpSuite extensions and automation rules. Explore API usage, custom tabs, serializers, and macros. Gain practical skills for enhancing web application security testing capabilities.
Stable12 Hacking Web Apps
Learn web application hacking techniques and strategies from expert Brent White in this informative conference talk from Derbycon 2015.
The 3 Way09 Going AUTH the Rails on a Crazy Train
Explore authentication vulnerabilities in Ruby on Rails applications, focusing on common pitfalls and effective security measures for web developers.
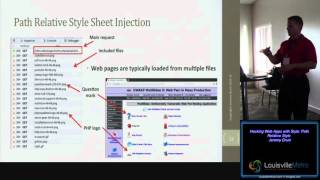
Hacking Web Apps with Style Path Relative Style
Explore web application vulnerabilities and attack techniques using style path relative methods, enhancing your understanding of web security and ethical hacking practices.
Bumper Massage - Punch and Counter Punch Part Deux - Web Applications
A short, under 1-hour program featuring videos from GrrCON 2015, focusing on web applications.
Hacking Web Apps
Learn essential techniques for identifying and exploiting common web application vulnerabilities, enhancing your cybersecurity skills and understanding of web security.
Hacking Web Apps
Learn techniques for identifying and exploiting web application vulnerabilities, focusing on practical methods to enhance security testing skills.