Portable Data exFiltration - XSS for PDFs
Explore PDF vulnerabilities and learn how a single HTTP link can compromise PDF contents, exposing security risks in widely-used document formats and generators.
Stupid Webappsec Tricks
Discover simple yet effective techniques for detecting vulnerabilities and making malicious activity economically infeasible in web application security.
What Do You Mean My Security Tools Don't Work on APIs?
Explores techniques for securing APIs and modern service-based web applications, discussing challenges and innovative approaches like security instrumentation for vulnerability identification and protection.
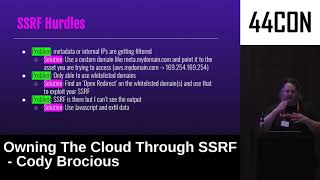
Owning the Cloud Through SSRF
Explore cloud security vulnerabilities through SSRF attacks, focusing on metadata exploitation, CVE examples, and advanced techniques like DNS rebinding for comprehensive cloud protection.
Keeping Up with the Web Application Security
Explore strategies for maintaining robust web application security in an ever-evolving digital landscape. Learn from industry experts about current threats and effective countermeasures.
Verena - End-to-End Integrity Protection for Web Applications
Explore end-to-end integrity protection for web applications, focusing on safeguarding sensitive information against server-side attacks and ensuring data authenticity for users.
Runtime Recovery of Web Applications under Zero-Day ReDoS Attacks
Explore techniques for protecting web applications against zero-day ReDoS attacks, focusing on runtime recovery strategies to maintain system functionality and security.
The Weakest Link
Sicherheitslücken in Mobilfunk-Webapps ermöglichen Angreifern Rufumleitungen und Kontoübernahmen durch einfache Newsletter-Links. 40% der österreichischen Nutzer waren 2020 betroffen.
Max Level Web App Security
Learn advanced web application security techniques, including threat modeling, secure coding practices, and vulnerability assessment strategies for robust protection against cyber threats.
A New Era of Security - How Web Platform Features Can Save Your Application
Explore modern web security features to protect against XSS, CSRF, and other common threats. Learn how to implement CSP3, Trusted Types, and Fetch Metadata Request Headers in your applications.
Call to Arms - A Tale of the Weaknesses of Current Client-Side XSS Filtering
Uncovers 17 flaws in Chrome's XSS Auditor, demonstrating bypasses and presenting a tool for generating attacks. Analyzes filter effectiveness against real-world vulnerabilities, proposing future improvements.
Libinjection - A C Library for SQLI Detection and Generation Through Lexical Analysis
Innovative C library for SQL injection detection using lexical analysis, offering high precision and accuracy. Trained on real attacks, it categorizes threats and provides templates for new attack detection.
Attacking Web Services - Next Generation of Vulnerable Enterprise Apps
Explore vulnerabilities in enterprise web services and learn advanced techniques for identifying and exploiting security flaws in next-generation applications.
Announcing OWASP Guide to Securing Web Applications & Services 2.0
Comprehensive guide to securing web applications and services, covering best practices, vulnerabilities, and mitigation strategies for developers and security professionals.
ModSecurity as Universal Cross-Platform Web Protection Tool
Explore ModSecurity's evolution into a cross-platform WAF, its early attack detection capabilities, and its use of OWASP Core Rule Set for protecting Apache, IIS, and nginx servers.
Truncating TLS Connections to Violate Beliefs in Web Applications
Exploring TLS truncation attacks to exploit web application flaws, demonstrating vulnerabilities in authentication systems and their impact on popular platforms like Helios, Microsoft Live, and Google.
Dissecting CSRF Attacks & Countermeasures
Explore CSRF attacks, current countermeasures, and a proposed header-based policy for improved web security. Learn detection techniques and a new concept called Storage Origin Security for simplified protection.
Big Data for Web Application Security
Explore how big data analytics can enhance web application security, with real-world examples of proactive and reactive security measures using MapReduce and Cascading.
Web Application Security
Explore web application security fundamentals and best practices with expert Jeremiah Grossman in this comprehensive conference talk from Black Hat Europe 2001.
Web Application Security
Explore web application security fundamentals, vulnerabilities, and best practices with industry experts Dennis Groves and Bill Pennington in this comprehensive conference talk.
Web Hacking Part 1 & 2
Explore advanced web hacking techniques and vulnerabilities in this comprehensive two-part session, covering essential skills for ethical hackers and cybersecurity professionals.