How Federal Prosecutors Use The CFAA
Explore the Computer Fraud and Abuse Act through a federal prosecutor's lens. Gain insights into charging decisions, sentencing factors, and balancing security research with law enforcement needs.
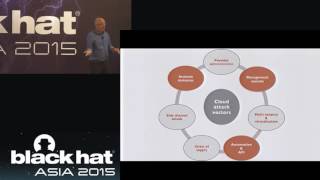
From Zero to Secure in One Minute
Automated cloud security tool for rapid instance lifecycle: pre-configured, patched, encrypted, and auto-mitigated. Introduces "Cloudefigo" for accelerated security in dynamic cloud environments.
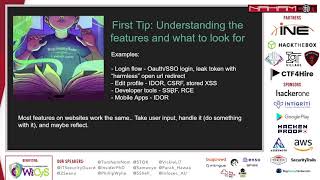
Putting Your Mind to It - Bug Bounties for 12 Months
Insights into successful bug bounty hunting strategies and experiences over a 12-month period, focusing on mindset, persistence, and effective techniques for finding vulnerabilities.
Unleash the Infection Monkey - A Modern Alternative to Pen-Tests
Explore a new open-source tool for testing network security resilience. Learn how the Infection Monkey simulates attacks, uncovers vulnerabilities, and provides a cost-effective alternative to traditional penetration testing methods.
A Radiography of a SBOM Vulnerability Scanner
Explore Software Bill of Materials (SBOM) for enhanced cybersecurity. Learn about SBOM tools, formats, and integration in DevSecOps pipelines. Practical examples using Syft, Grype, and bomber for vulnerability scanning.
Testing Java Microservices - From Development to Production
Learn techniques for testing microservices, from isolating components to automating security scans. Overcome challenges in distributed systems and ensure robust performance across development, QA, and production.
The Secret Codes Tell the Secrets
Exploración de códigos secretos en dispositivos Android, revelando vulnerabilidades de seguridad y métodos de bypass en teléfonos de principales fabricantes. Incluye demostraciones prácticas y herramientas de fuzzing.
Exploiting Windows Hello for Business
Uncover vulnerabilities in Windows Hello for Business and learn to scan and secure corporate environments with a new toolset for enhanced Active Directory visibility.
Kill All Humans - Bugs - Machine Learning to the Rescue of Code Review
Explore machine learning techniques for efficient security code reviews, reducing false positives and automating vulnerability classification in large-scale applications.
Sysadmins' Introduction to Vulnerability Scanning
Explore vulnerability scanning essentials for sysadmins, covering software vulnerabilities, networking, scanning tools, and server inspection. Learn how ops involvement can enhance overall security processes.
HTML5 Top 10 Threats - Stealth Attacks & Silent Exploits
Explores top 10 HTML5 security threats, including CORS attacks, clickjacking, XSS, web storage vulnerabilities, and more. Demonstrates real-life examples and discusses defense strategies against emerging attack vectors.
Out of Control - Demonstrating SCADA Device Exploitation
Explore SCADA device exploitation in oil and gas pipelines, examining control systems, vulnerabilities, and potential consequences of security breaches in critical infrastructure.
Silos to Seamless - Creating a Comprehensive Security Program
Learn to create a comprehensive security program, addressing threats, asset protection, and incident response while emphasizing the human element in cybersecurity.
Recon ng and Beyond - Tim Tomes
Explore advanced reconnaissance techniques using Recon-ng, covering modules like Meta Crawler, Profiler, and vulnerability scanning. Learn to leverage search engines and GitHub for effective information gathering.
Container Chaos - Docker Security Container Auditing
Explore Docker security, container auditing, and DevOps practices. Learn about vulnerability scanning, automation, and best practices for secure containerization in this comprehensive overview.
Building a Scalable Vulnerability Management Program for Effective Risk Management
Learn to build and maintain a scalable vulnerability management program, covering asset prioritization, scanning, remediation, reporting, and continuous improvement for effective risk management.
Burping for Joy and Financial Gain
Learn techniques for enhancing web application security testing, including custom passive scanning, regex extraction, and bypassing client-side anti-automation measures.
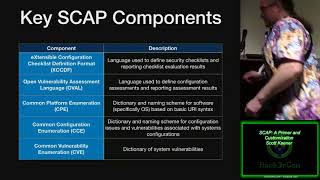
SCAP - A Primer and Customization
Comprehensive overview of SCAP, covering basics, components, tools, and customization techniques for effective security configuration assessment and management.
Container Security Deep Dive
Explore container security essentials, from base image protection to runtime security, covering deployment pipelines, vulnerability scanning, and real-time alerting in containerized environments.
Essential-8 Security in Practice with Kubernetes
Implementing Essential-8 security for large-scale data processing on Kubernetes. Balancing open-access needs with government security requirements. Covers infrastructure, deployments, network filtering, and incident response.
Building Images for the Secure Supply Chain
Explore techniques to enhance container image security, reduce vulnerabilities, and improve supply chain integrity. Learn about minimizing dependencies, updating images, and using tools like apko for reproducibility and SBOM generation.