Wolfi: Introduction to the Linux Undistro for Building Small, Up-to-Date, CVE-Free Cloud Images
Discover Wolfi, an innovative Linux 'undistro' for creating small, secure cloud images with minimal attack surfaces and reduced CVE threats. Learn its architecture and tools for keeping software updated.
Wolfi - A Secure-by-Default Distro for Curing Container CVE Chaos
Explore Wolfi, a Linux distribution for building secure, minimal containers. Learn packaging techniques with apko and melange to create vulnerability-free containers and improve your Docker image security.
Reducing Alert Fatigue with Container Scans: Correlate, Prioritize and Filter Based on Usage
Strategies to manage container vulnerabilities: correlate with runtime data, prioritize based on usage, and filter false positives for efficient security in multi-container applications.
Docker Scout - Securing the Complete Software Supply Chain
Explore Docker Scout's real-time vulnerability detection, remediation suggestions, and policy evaluation for enhanced software supply chain security across the entire development lifecycle.
Demystifying the Linux Kernel Security Process
Explore the Linux kernel security process with Greg Kroah-Hartman. Learn about vulnerability management, change propagation, and maintaining system security in this insightful session.
Bringing Containers to Enterprise: Security Challenges and Solutions
Overview of container security, isolation techniques, and enterprise use cases. Explores user namespaces, POSIX capabilities, and Seccomp support to enhance protection against vulnerabilities and exploit attacks.
Kernel Self-Protection Project: Eliminating Bug Classes and Blocking Exploitation Techniques
Overview of Kernel Self-Protection Project's progress, highlighting security defenses implemented in Linux kernels 4.19-5.3, ongoing developments, and areas needing assistance in enhancing kernel security.
SecDevOps: A View from the Trenches
Explore SecDevOps implementation strategies and real-world challenges with insights from industry experience, focusing on practical approaches to integrate security into DevOps workflows.
Restricted Address Spaces for Container Security
Explore container security through restricted address spaces, focusing on vulnerabilities, namespace management, and performance implications in Linux systems.
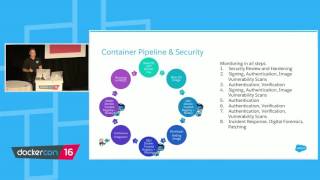
Securing the Container Pipeline at Salesforce - Docker Use Case
Securing Docker containers at Salesforce: infrastructure, pipeline security, monitoring, forensics, and automation for rapid containerization while maintaining data sensitivity and customer trust.
Securing Containers - One Patch at a Time
Explore CVE-2016-9962: discovery, implications, and resolution. Dive into kernel boundaries, system calls, and address space randomization for enhanced container security.
Linux System Security Tutorial
Comprehensive exploration of Linux system security principles and best practices, emphasizing practical strategies for robust protection in enterprise environments.
Continuous Integration, Packaging, Delivery, and Security - Best Practices for Modern Application Development
Explore modern application delivery pipelines, focusing on security, quality, and integrity. Learn to manage open-source components, mitigate supply chain risks, and implement continuous security practices.
Container Security: It's All About the Supply Chain
Explore container security as a supply chain lifecycle issue, focusing on integrating validation at multiple points to achieve assurance in the software development process.
Container Security 101
Comprehensive introduction to container security, covering key concepts, best practices, and practical strategies for securing containerized applications.
Security Risks in Third-Party GitHub Actions - Overlooked Consequences
Explore security risks in GitHub Actions, including build permission issues and "unpinnable actions." Learn about potential consequences and challenges in protecting against compromised third-party actions.
Securing Vulnerable Images with Copa - Hot Fix Techniques
Learn to secure container images instantly using Copa, addressing vulnerabilities without full rebuilds. Explore real-time scanning, patching, and filtering techniques for efficient image protection.
From Risks to Resilience: Leveraging CNCF Projects Against Kubernetes' OWASP Top 10
Explore strategies to mitigate OWASP Kubernetes Top Ten security risks using CNCF projects. Learn actionable insights to enhance the security of your Kubernetes deployments.
Secure Development with Docker - Workshop
Comprehensive workshop on securing software supply chains using Docker, covering common attacks, remediation strategies, and leveraging Docker Scout for actionable insights and early problem detection.
One-Click Code Fix - Securing Code Using AI
Automate vulnerable code remediation in production using AI. Learn practical strategies and see demos for efficient, robust code repair techniques.
Keep Hackers Out of Your Cluster with These 5 Simple Tricks
Discover data-driven strategies to enhance Kubernetes cluster security, focusing on real-world attacks and high-impact vulnerabilities. Learn effective mechanisms to protect against malicious workloads and container escapes.