Software Composition Risk - Determining Actual Risk and Taking Action
Explore software composition risk assessment, mitigation strategies, and proactive processes to enhance enterprise security beyond vulnerability scanning and manual updates.
Patching Your Way to Compliance with a Small Team and Technical Debt
Learn strategies to overcome system patching challenges with limited resources, focusing on breaking the cycle of technical debt and meeting security compliance requirements.
Your Kubernetes Single-Pane of Glass with Kubescape
Explore Kubescape, a comprehensive tool for Kubernetes security and compliance management, offering a unified view of cluster health and vulnerabilities.
Cloud Native Live - Locking Down Your Cluster
Explore strategies for enhancing Kubernetes cluster security, including best practices, tools, and techniques to protect against vulnerabilities and unauthorized access.
Policy Driven Approach to Secure CI/CD Workflow
Explore how Tekton, ArgoCD, and Kyverno can enhance CI/CD pipeline security, compliance, and reliability. Learn to automate policy enforcement and address supply chain vulnerabilities in Kubernetes environments.
Kubernetes Security Response Committee: Introduction and Deep Dive
Explore the Kubernetes Security Response Committee's role, vulnerability lifecycle, and key findings from the 2022 security audit. Learn about reporting processes and community impact.
Container Patching: Making It Less Gross Than the Seattle Gum Wall
Explore strategies for efficient container patching, including prevention, detection, fixing, and monitoring. Learn about opensource tools and best practices to streamline the process and meet security requirements.
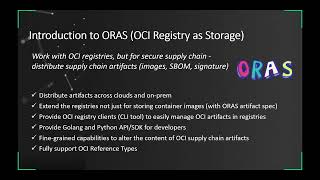
Secure Container Supply Chain with Notation, ORAS, and Ratify
Explore tools for securing container supply chains: Notation for signing artifacts, ORAS for distributing OCI artifacts, and Ratify for verifying container images.
Kubescape Roadmap - Future Developments in Kubernetes Security
Explore the future of Kubernetes security with Kubescape's development plans and upcoming features in this informative CNCF presentation.
Flux at the Point of Change - Using Kubernetes Golang SDK and Flux API to Automatically Fix and Deploy CVEs - Lecture
Explore automated CVE remediation in Kubernetes using Client-Go SDK and Flux API. Learn to enhance security across enterprise applications and golden images.
Enforcing a Secure Supply Chain on Kubernetes
Explore implementing and enforcing a secure supply chain in Kubernetes using open-source projects, including Sigstore keyless workflow and signature verification policies.
Docker Security Insights - Vulnerabilities and Best Practices
Explore Docker security vulnerabilities, countermeasures, and best practices for production environments. Learn about container risks, secrets management, content trust verification, and open-source library considerations.
Securing Containers on the High Seas
Strategies for secure container implementation, focusing on infrastructure, architecture, tooling, policies, and processes. Explores container lifecycle security from development to production.
Breaking Out of the Container Without Zero Day - Security Risks in DevOps
Explore container security risks in DevOps environments, focusing on potential vulnerabilities and attack vectors beyond zero-day exploits. Learn strategies to enhance container security and protect your infrastructure.
Containers Security Layers and How Not to Break Them
Explore container security layers and best practices to maintain their integrity, presented by an expert from Palo Alto Networks.
GitHub Actions Security Landscape
Explore the security landscape of GitHub Actions, uncovering potential vulnerabilities and best practices for safeguarding your CI/CD pipelines.
Minimizing Blast Radius of Chained Kubernetes Misconfigurations and Image Vulnerabilities
Explore strategies to minimize security risks in Kubernetes deployments, focusing on misconfigurations, image vulnerabilities, and balancing security with usability in cloud-native environments.
What is Lacking in Linux Security and What Should We Do About It - Panel Discussion
Experts discuss current Linux security challenges and potential solutions, exploring vulnerabilities, best practices, and future improvements for enhanced system protection.
My Container Image Has 500 Vulnerabilities - Now What?
Learn strategies to address and mitigate vulnerabilities in container images, enhancing security practices for Docker deployments.
Container Image Vulnerability Management - Strategies and Best Practices
Practical guide to addressing container image vulnerabilities, covering base image selection, Dockerfile optimization, code dependency checks, and advanced techniques like multistage builds.
Cleaning up Vulnerable Images from Kubernetes Nodes
Explore Eraser, an open-source solution for automating the scanning and removal of vulnerable images from Kubernetes nodes, enhancing supply chain security in cloud-native environments.