Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.
Application Security Verification Standard - OWASP Flagship Project
Comprehensive guide to OWASP's Application Security Verification Standard, covering its history, development, and implementation strategies for robust application security.
OWASP Serverless Top 10 - Security Risks and Protections
Explore serverless security risks, challenges, and protective measures. Learn about OWASP Serverless Top 10 and DVSA tool for understanding serverless security implications and processes.
Practical Mobile App Attacks By Example
Explore real-world mobile app vulnerabilities and attack techniques through hands-on demonstrations, enhancing your understanding of mobile security risks and defense strategies.
OSINT to Compromise - Techniques for Information Gathering
Explore OSINT techniques for ethical hacking and cybersecurity, learning how to gather and analyze open-source intelligence to identify vulnerabilities and enhance digital defense strategies.
Good Bot, Bad Bot: Characterizing Automated Browsing Activity
Explore Aristeus, a system for deploying honeysites to study malicious bot behavior. Learn about bot traffic patterns, attack strategies, and the importance of understanding automated browsing activity for web security.
Hack Your APIs in 15 Minutes or Less - Exploiting Shadow APIs and Data Vulnerabilities
Learn to identify and exploit API vulnerabilities, understand hacker techniques, and explore creative methods for data theft in this eye-opening talk on modern cybersecurity challenges.
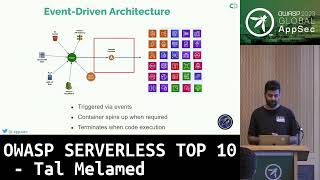
OWASP Serverless Top 10 - Understanding Security Risks in Serverless Applications
Explore the top 10 security risks in serverless architectures, understanding vulnerabilities and best practices for securing cloud-native applications.
Automated Security Testing With OWASP Nettacker
Learn automated security testing techniques using OWASP Nettacker, a powerful open-source tool for vulnerability assessment and information gathering in web applications and networks.
Benchmarking the Security of Your Software Supply Chain
Learn to assess and enhance the security of your software supply chain through benchmarking techniques, improving overall cybersecurity posture and reducing vulnerabilities.
Mitigate Risks in Code - Protect Your Software-based Supply Chain
Explore strategies to mitigate risks in code and safeguard your software-based supply chain, enhancing overall security and resilience in software development.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
Docker for Pentesters
Learn essential Docker techniques for penetration testing, enhancing your cybersecurity skills and improving your ability to identify vulnerabilities in containerized environments.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
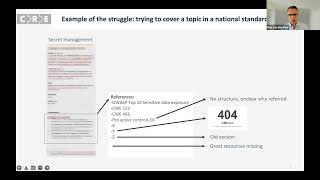
Understanding the Complete Chain of Application Security Using OpenCRE.org
Explore a comprehensive approach to application security using openCRE.org, covering key concepts and best practices for robust software protection.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
Helpful Hackers - Keynote by Astrid Oosenbrug
Explore the world of ethical hacking and its positive impact on cybersecurity with insights from Astrid Oosenbrug's keynote address on helpful hackers.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
Exposing Security Flaws in Trading Technologies
Uncovers vulnerabilities in popular trading platforms, highlighting risks in electronic trading. Discusses security gaps in websites, desktop apps, and mobile apps used for stock and cryptocurrency trading.
OWASP Glue Tool: Security Automation Made Easier
Learn about OWASP Glue Tool, a Ruby gem for security automation that coordinates multiple analysis tools and generates reports, simplifying the process of integrating security into development workflows.
Robots with Pentest Recipes - Automating Security Testing in DevOps
Explore automated security testing using Robot Framework to integrate tools like OWASP ZAP and Nmap. Learn to create easy-to-write test recipes for continuous delivery pipelines, enabling cross-team collaboration in application security.