Password Exploitation Techniques - Class 1
Learn techniques for password exploitation, including cracking methods and security vulnerabilities, from expert speakers in this comprehensive cybersecurity session.
Password Exploitation Techniques - Class 2
Learn advanced techniques for password exploitation, including cracking methods and security measures, from industry experts in this comprehensive cybersecurity session.
A New "Water" Watering Hole - Cyber Threats to Water Utilities
Explore intrusion analysis and threat intelligence for water utilities with Dragos experts. Learn analytic techniques to uncover unique cyber threats and understand the importance of community partnerships.
Industrial Control Systems Cybersecurity - 2020 Year in Review and Threat Landscape
Explore key findings from 2020's ICS cybersecurity landscape, including new threat groups, vulnerabilities, and insights from threat hunts and incident response engagements.
Evaluating ICS Vulnerabilities - Prioritization and Mitigation Strategies
Explore ICS vulnerability analysis, prioritization, and mitigation strategies. Learn to assess risks, optimize ROI on security efforts, and implement effective monitoring in industrial control systems.
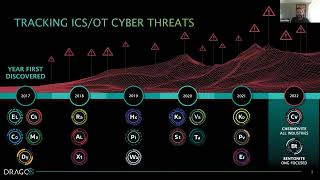
ICS/OT Cybersecurity Year in Review 2022 - Executive Briefing
Explore key ICS/OT cybersecurity insights from 2022, including top threats, new threat groups, vulnerabilities, and incident response stories, with data-driven analysis and recommendations.
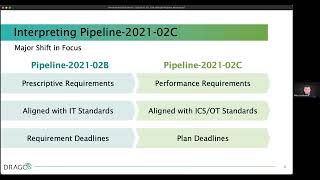
TSA Pipeline Security Directive SD02C Workshop
Explore TSA's Pipeline Security Directive SD02C, focusing on cybersecurity measures for critical infrastructure protection in the oil and gas industry.
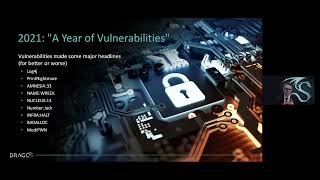
2021 ICS/OT Cybersecurity Vulnerability Briefing - Year in Review
Comprehensive analysis of 2021 ICS/OT vulnerabilities, offering insights on trends, high-profile cases, and actionable guidance for prioritizing and addressing cybersecurity risks in industrial environments.
OWASP Top 10 - Application Security Risks
Explore the latest OWASP Top 10 web application security risks with expert Andrew van der Stock. Learn about critical vulnerabilities and effective mitigation strategies for safer software development.
Mobile-First Websites Security Evaluation - Attacker-Friendly or User-Friendly?
Evaluate security vulnerabilities in mobile-first websites, exploring potential risks and attacker-friendly features. Learn to identify and mitigate threats in mobile web development.
Building an AppSec Program with a Budget of $0 - Beyond the OWASP Top 10
Explore OWASP projects to build a comprehensive AppSec program without spending money. Learn how to implement open-source tools for training, development, testing, and defense to create a robust security framework.
HUNT: Data-Driven Web Hacking and Manual Testing
Turbocharge web hacking with HUNT, a Burp Suite extension using real threat intelligence to provide parameter-level vulnerability suggestions and organize testing methodologies for more thorough assessments.
DNS Hijacking Using Cloud Providers: No Verification Needed - AppSec EU 2017
Explore advanced domain hijacking techniques, including undisclosed methods, to understand vulnerabilities in DNS providers and cloud services. Learn to identify and mitigate risks beyond common subdomain takeover scenarios.
Fast Forwarding Mobile Security with the Mobile Security Testing Guide
Explore mobile security advancements and best practices using the Mobile Security Testing Guide (MSTG) in this comprehensive OWASP presentation.
Slack App Security: Securing Workspaces from a Bot Uprising
Explore Slack app security, potential risks, and solutions for safeguarding workspaces. Learn about the app directory's history, unique security challenges, and Slack's efforts to enhance user protection.
Open Source Dependencies: Risks and Impacts - AppSec EU 2017
Explore the risks of open-source dependencies in software development, including potential impacts of code removal or malicious modifications on major organizations and applications.
Improving the Security of Software Defined Infrastructures - AppSec EU 2017
Explore security challenges in Software Defined Infrastructures, learn attack surfaces, vulnerability identification techniques, and remediation strategies for configuration management tools like Puppet or Chef.
Essential TLS Hardening for Better Web Security
Explore essential TLS hardening techniques for enhanced web security with Justin Mayer, founder of Monitorial.com. Learn practical strategies to identify and address potential vulnerabilities in your web applications.
Threat Modeling for Mobile Applications
Explore threat modeling techniques for mobile applications with expert Amit Sethi. Learn to identify and mitigate security risks in mobile development.
Hacking Alexa and Cortana: Vulnerabilities in Voice Assistant Partnerships
Explore innovative "Evil Maid" attacks on Windows, vulnerabilities in Cortana-Alexa integration, and the challenges of merging new concepts with existing security mechanisms. Gain insights into AI and IoT security.
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.