Bug Hunting as a Team: Challenges and Insights - LevelUp 0x04
Insights on collaborative bug hunting: organizing teams, sharing information, splitting bounties, and overcoming challenges in the evolving field of cybersecurity.
LevelUp 0x04: Advanced Bug Bounty Techniques - Day 2
Explore advanced bug bounty techniques and strategies with industry experts in this comprehensive cybersecurity event focused on enhancing hacking skills and knowledge.
IoT Security - Attacker's Perspective on Common Vulnerabilities
Explore IoT vulnerabilities from an attacker's perspective, covering famous exploits, OWASP IoT Top10, and practical attack methodologies. Gain insights for both security professionals and IoT developers.
Critical Vulnerabilities and Bug Bounty Programs
Explore critical vulnerabilities uncovered through bug bounty programs, their impact, and strategies for effective vulnerability management and disclosure in cybersecurity.
How the Crowd Outperforms Traditional Security Testing
Explore how crowdsourced security testing outperforms traditional methods, with insights on implementation, benefits, and real-world examples from successful bug bounty programs.
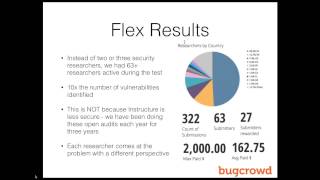
Key Takeaways from Instructure's Bug Bounty Program
Discover insights from Instructure's Bug Bounty program, including their innovative approach to security audits, crowdsourced penetration testing, and key lessons learned for enhancing cybersecurity practices.
MarkDoom- How I Hacked Every Major IDE in 2 Weeks - Matt Austin, LevelUp 2017
Explore web hacking techniques used to exploit major IDEs and desktop applications, revealing high-severity vulnerabilities in popular development tools.
Pentesting vs Bug Bounty - Approaches and Methodologies
Explore the differences between bug bounty hunting and penetration testing methodologies, comparing approaches, impacts, and scoping techniques.
How I Hacked 55 Banks and Cryptocurrency Exchanges - LevelUpX Series 3
Alissa Knight reveals tactics used to breach 55 financial institutions, offering insights into vulnerabilities in FinTech apps and APIs. Learn from a veteran hacker's experience in cybersecurity.
It's Not a Vulnerability, It's a Feature - Exploiting Built-in Functionality
Explore how offensive security has evolved from CVEs to TTPs, and learn to leverage built-in features for security testing and potential monetization through creating and sharing TTPs.
Car Hacking Explained for Bug Hunters - Automotive Security Vulnerabilities and Methodologies
Explore automotive security vulnerabilities, from IoT to CAN bus hacking. Learn methodologies, attack surfaces, and bug prioritization for car hacking, covering infotainment systems, APIs, and mobile apps.
Recognition Primed Bug Bounty Hunting - Maximizing Impact and Success
Enhance bug bounty hunting skills through decision-making techniques from emergency services. Learn to maximize impact, escalate findings, and make critical choices for bigger scopes and larger rewards.
Managing a Bug Bounty Program From a Hacker's Perspective - NahamCon 2022 EU
Insights on managing bug bounty programs from an ethical hacker's perspective, covering strategies, challenges, and best practices for effective vulnerability disclosure and collaboration.
Bug Bounty Methodology and Hacking the US Government - Interview with Jack Cable
Insights from a top bug bounty hunter on hacking methodology, government cybersecurity, and career advice for aspiring ethical hackers.
Your Guide to Burp Suite - Setup and Usage in 30 Minutes
Learn to set up and effectively use Burp Suite for web security testing in under 30 minutes, covering essential features and functionalities.
SPI Flash Extraction for Bug Bounty Hunters - LevelUpX Series 13
Hands-on guide to extracting SPI flash contents from hardware devices, focusing on techniques and tools for bug bounty hunters to uncover valuable data and impactful vulnerabilities.
Live Hacking Events - What They Are and How They Work
Explore Live Hacking Events with HackerOne's Community Team. Learn about these unique cybersecurity gatherings, their benefits, and how to participate in this exciting hacking format.
Recon Sunday with Top HackerOne Paid Hackers - Dawgyg, Mayonaise, and cdl
Live hacking event featuring top-paid hackers Dawgyg, Mayonaise, and cdl discussing reconnaissance techniques and strategies for bug bounty hunting on HackerOne's platform.
Pentesting, Bug Escalation, and Career Insights - Interview with Codingo
Insightful discussion on pentesting, bug escalation, OSCP certification, and industry experiences, offering valuable insights for aspiring and seasoned cybersecurity professionals.
Introduction to Web Hacking - OWASP Juice Shop
Comprehensive introduction to web hacking using OWASP Juice Shop, covering essential techniques and vulnerabilities for aspiring ethical hackers and security enthusiasts.
Hacking Uber, Working at Synack, and the 120 Reports in 120 Days Challenge
Insightful discussion on ethical hacking experiences, including Uber vulnerabilities, Synack employment, and a unique 120-day bug bounty challenge. Valuable insights for aspiring cybersecurity professionals.