
Lessons from Trusting JavaScript Cryptography - Biting into the Forbidden Fruit
Exploring real-world JavaScript cryptography implementations, debunking myths, and providing an updated perspective on JS crypto security through vulnerability analysis and practical examples.
OWASP Periodic Table of Vulnerabilities
Explore a new approach to web security using the OWASP Periodic Table of Elements, focusing on eliminating vulnerabilities through perimeter technologies and application frameworks.
SBOMs: Essential for Embedded Systems
Explore the importance of Software Bill of Materials (SBOM) in embedded systems, regulatory expectations, and implementation in open source projects for improved cybersecurity and risk management.
Open Source Supply Chain Threat Landscape - A Moving Target
Explore the evolving landscape of open source supply chain threats, their impacts, and strategies for implementing developer-first security to counter sophisticated attacks.
Security as Code: A DevSecOps Approach
Explore DevSecOps and Security as Code principles, focusing on SQL injection prevention and vulnerability analysis using Code2LV and data flow techniques.
Security Analysis of Industrial Serial Device Servers
Explore security vulnerabilities in industrial serial device servers and learn effective analysis techniques for identifying and mitigating potential threats.
Only an Electron Away from Code Execution
Explore vulnerabilities in Electron-based applications and learn techniques for achieving code execution, presented by security researcher Silvia Väli at Hack.lu 2018.
The Path Towards Automated Heap Exploitation
Explore automated heap exploitation techniques and strategies for enhancing cybersecurity defenses in this insightful conference talk by Thaís Moreira Hamasaki.
Dissecting the 0-Day Supply Chain Vulnerability in Argo CD
Explore the discovery and implications of a critical 0-day vulnerability in Argo CD, including attack methods, remediation steps, and its impact on the ecosystem.
KeyBleed: Attacking the OneKey Mini Cryptocurrency Wallet - Hack In The Box 2023
Revealing vulnerabilities in cryptocurrency hardware wallets, focusing on the OneKey Mini's security flaws. Demonstrates live exploit to extract and crack the seed, recovering stored funds in under one second.
Open Wounds: The Last 5 Years Have Left Bluetooth to Bleed
Explore critical Bluetooth vulnerabilities from the past 5 years, their impact on device security, and potential mitigation strategies in this eye-opening cybersecurity analysis.
Remotely Exploiting the ClamAV Antivirus Engine - CVE-2023-20032 Case Study
Explore a case study on exploiting CVE-2023-20032 in ClamAV, demonstrating remote code execution and ASLR bypass techniques applicable to similar antivirus software vulnerabilities.
Exploiting the Lexmark PostScript Stack
Explore Lexmark PostScript stack exploitation, covering internals, language basics, mitigations, and achieving remote code execution through out-of-bounds read and type confusion vulnerabilities.
Using Data-Driven Metrics to Anticipate and Prevent Security Incidents
Learn how GitHub's PSIRT Engineering team uses data-driven metrics and variant analysis to anticipate and prevent security incidents, reducing pressure on incident response and enhancing product security.
2022 ICS/OT Cybersecurity Year in Review - Vulnerability Trends and Mitigation Strategies
Insights on ICS/OT vulnerabilities from 2022, including trends, notable cases, and mitigation strategies. Learn to prioritize and address cybersecurity risks in industrial control systems.
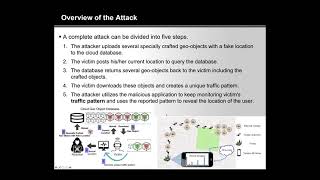
ARSpy: Breaking Location-based, Multi-player Augmented Reality Applications for User Location Tracking
Explore techniques for compromising user location data in multiplayer AR games, examining vulnerabilities and potential security risks in location-based applications.
Firmware Vulnerabilities in Critical Infrastructure - Tools and Techniques for Security Analysis
Explore firmware vulnerabilities in critical infrastructure using open-source tools. Learn techniques for deep security analysis, uncovering risks, and leveraging AI to simplify research and reverse engineering.
Opening the JAR: The Hitchhiker's Guide to JAR File Dependencies
Explore JAR file dependencies, their complex structures, and various inclusion methods. Learn about edge cases, oddities, and potential vulnerabilities in Java program dependencies.
The How and Why of the OWASP Top Ten 2021
Explore the OWASP Top Ten 2021 update, its significance, and data-driven insights. Learn about critical application security risks, analysis methodologies, and industry impact.
SUDO Security Policy Bypass Vulnerability - CVE-2019-14287
Explanation and demonstration of the sudo security policy bypass vulnerability (CVE-2019-14287), including how it works and can be exploited. Includes practical examples and technical details for cybersecurity professionals.
Exploit Hall of Fame - Techniques and Innovations
Renowned security researcher Thomas Dullien explores notable exploits, offering insights into vulnerability analysis and exploitation techniques in this engaging presentation.