Intro to Security and Network Forensics - Threat Analysis
Comprehensive overview of security threats, including penetration testing, vulnerability analysis, and common attack methods like phishing and SQL injection, with practical demonstrations.
Vulnerability Analysis and Penetration Testing Lab - DMZ Setup and Scanning
Hands-on lab exploring vulnerability analysis and penetration testing techniques, covering network scanning, fingerprinting, and security tool usage for identifying system weaknesses.
Introduction to Security and Network Forensics - Threat Analysis - Lecture 8
Comprehensive overview of threat analysis techniques, including penetration testing, vulnerability assessment, and common attack methods like SQL injection and phishing.
Radio Hack Shack - Security Analysis of Radio Transmission
Explore radio transmission security vulnerabilities and hacking techniques with expert Paula Januszkiewicz in this insightful analysis of radio communication risks and countermeasures.
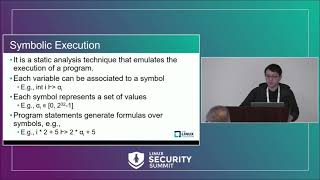
Triaging Kernel Out-of-Bounds Write Vulnerabilities
Explore techniques for triaging kernel out-of-bounds write vulnerabilities, including symbolic execution, capability summarization, and exploitability evaluation.
Dependency Hijacking Vulnerability in Microsoft Teams - Supply Chain Security Gaps
Explore real-world dependency hijacking in Microsoft Teams, understanding software supply chain vulnerabilities and learning strategies to protect infrastructure, SDLC, and code.
Vulnerable by Design - The Backdoor That Came Through the Front
Explore vulnerabilities in software design, historical backdoors, and their implications for security. Learn about notable cases and techniques for creating and detecting backdoors.
Exploit Development for Mere Mortals - BSidesRI 2013
Learn essential exploit development techniques and strategies for beginners, focusing on practical skills and real-world applications in cybersecurity.
Examining ICS Vulnerabilities: Analysis and Mitigation Strategies - Dragos Webinar
Explore ICS/OT vulnerability analysis, focusing on advisory errors, mitigation challenges, and severity discrepancies. Learn to prioritize and address critical industrial cybersecurity issues effectively.
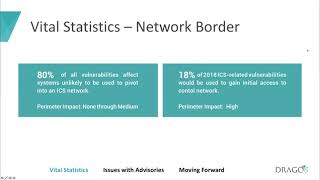
ICS Vulnerabilities in 2018 - Year in Review Webinar
Explore key findings from Dragos' 2018 ICS vulnerabilities report, covering vital statistics, advisory accuracy, and challenges in industrial cybersecurity.
Ripple20 Vulnerabilities in Industrial IoT - Analysis and Mitigation Strategies
Senior experts provide in-depth analysis of Ripple20, a critical vulnerability affecting Industrial IoT devices, exploring its impact, detection challenges, and mitigation strategies.
Practical Threat Modeling for Real-World and Cloud Situations in Hybrid Work Environments
Practical guide to threat modeling for cloud and hybrid work environments, covering creation, identification, addressing, and validation of threats with real-world examples and tools.
OWASP Dependency Track - Software Composition Analysis and Vulnerability Management
Explore OWASP Dependency Track: manage software components, analyze vulnerabilities, and enhance security with features like Software Bill of Materials, policy engine, and dependency graphs.
Pwning WhatsApp - The Dark Side of Web-based Messaging Apps
Explore vulnerabilities in web-based messaging apps, focusing on WhatsApp. Learn about potential security risks and exploitation techniques in popular communication platforms.
A Risk-Based Approach to API Security
Explore a risk-based approach to API security, focusing on threat modeling, vulnerability assessment, and mitigation strategies to enhance your organization's API protection.
A Weakness in Chrome and a New Hacking Technique
Explore a critical Chrome vulnerability and innovative hacking method presented by security experts. Gain insights into cutting-edge web security threats and defense strategies.
How to Find the Next Great Deserialization CVE - AppSecUSA 2016
Explore deserialization attacks, learn to find and exploit vulnerabilities, and discover open-source protection methods. Gain insights into the challenges of traditional AppSec defenses against these threats.
Bugs Ruin Everything - Keynote on Vulnerability Analysis and Exploitation
Explore vulnerability analysis techniques, their strengths and weaknesses, and real-world case studies with security expert Charlie Miller in this engaging keynote from AppSecEU 2016.
Why Secure Development Programs Are Essential for Application Security
Explore integrating application security into development processes, focusing on proactive measures, resource allocation, and adapting to Agile and DevOps methodologies for effective risk management.
The Top 10 Web Hacks of 2014 - AppSec EU 2015
Explore the most significant web security vulnerabilities of 2014, presented by industry experts. Gain insights into attack vectors and learn essential defense strategies.
Copy Pest - A Case Study on the Clipboard, Blind Trust, and Invisible Cross-Application XSS
Explore clipboard vulnerabilities and cross-application XSS in this case study on invisible security threats and blind trust in web applications.