Timing Attacks Against Web Applications: Are They Still Practical? - DefCamp - 2018
Explore the practicality of timing attacks on web applications, including prerequisites, calculation methods, and potential consequences. Learn about attack resources and possible solutions.
20 Ways Past Secure Boot
Explore 20 methods to bypass secure boot, including debug access, exploits, timing attacks, glitches, and design flaws. Learn about real-world examples and security implications.
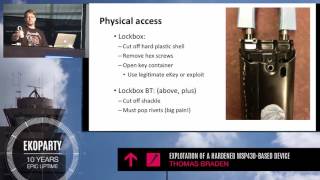
Exploitation of a Hardened MSP430-Based Device - Braden Thomas - Ekoparty Security Conference - 2014
Reverse-engineering and exploiting a hardened MSP430 device: techniques for firmware extraction, analysis, and data retrieval from RAM, with focus on overcoming JTAG security measures.
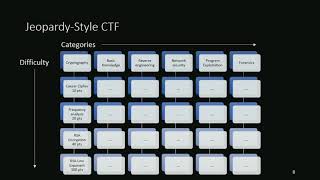
How the Best Hackers Learn Their Craft
Discover the proven system for building elite hacker teams, from talent identification to competition success. Learn surprising strategies for developing top-tier cybersecurity skills and fostering creative problem-solving abilities.
Timeless Timing Attacks
Explore novel timing attacks resilient to network jitter, uncovering vulnerabilities in cryptosystems and applications. Learn about cross-site and Wi-Fi password brute-forcing techniques.
Evading Anti-APT Technologies
Learn advanced techniques to bypass anti-APT technologies, including sandbox weaknesses, timing attacks, and dynamic analysis. Gain insights into evading endpoint security and improving your cybersecurity skills.
My Ticks Don't Lie - New Timing Attacks for Hypervisor Detection
Explore new timing attacks for hypervisor detection, crucial for sandbox evasion in malware analysis. Learn about hardware-assisted virtualization vulnerabilities and low-level measurement techniques.
Next Level Cheating and Leveling Up Mitigations
Explore sophisticated attacks on anti-cheat systems in multiplayer gaming, including practical demonstrations and implications for game security and the future of cheat prevention.
On Subnormal Floating Point and Abnormal Timing
Explores timing vulnerabilities in x86 floating-point operations, demonstrating practical attacks on Firefox and a privacy-focused database. Introduces a constant-time math library as a potential mitigation.

Reverse-Engineering the Supra iBox - Exploitation of a Hardened MSP430-Based Device
Detailed walkthrough of reverse-engineering and exploiting a hardened MSP430-based key storage device, covering firmware extraction, crypto analysis, and various attack techniques.
Racing Towards Practical Timing Attacks
Explore practical timing attacks in web applications, focusing on detection, exploitability, and defense. Learn to distinguish theoretical vulnerabilities from real threats using the 'time trial' tool.
AIS Exposed - Understanding Vulnerabilities and Attacks 2.0
Explore vulnerabilities in Automatic Identification Systems, including malicious routes, hijacking, spoofing, and DoS attacks. Learn about real-world experiments and proposed countermeasures.
CacheBleed - A Timing Attack on OpenSSL Constant Time RSA
Explore a timing attack on OpenSSL's constant-time RSA implementation, uncovering vulnerabilities in cryptographic systems and their potential impact on security.
Prefix Siphoning - Exploiting LSM-Tree Range Filters for Information Disclosure
Explores key disclosure timing attacks on LSM-tree based key-value stores using range filters, demonstrating security vulnerabilities in data storage systems.
JavaScript - The Evil Parts
Explore JavaScript's security vulnerabilities, design flaws, and potential for application hijacking. Learn about obfuscation techniques and enterprise-level attacks in this eye-opening talk.
Clocks Have Ears - Timing and Browser-Based Local Network Port Scanner
Discover how browser-based timing attacks can be used for local network port scanning, exploring innovative security techniques and network vulnerability assessment methods.
Side Channels and Leakage in Cryptography
Explore cutting-edge research on cryptographic vulnerabilities and protection mechanisms in this expert-led session from a prestigious conference.
Side Channels and Backdoors in Cryptographic Systems
Explore side channels, backdoors, and security vulnerabilities in various systems. Learn about mitigations, lessons from past failures, and best practices for secure key generation and boot processes.
Side-Channel Analysis Advancements - CHES 2024
Explore advanced side-channel analysis techniques and their applications in cryptography at this CHES 2024 session, chaired by Shivam Bhasin.
Web Timing Attacks That Actually Work - Practical Techniques and Tools
Discover practical web timing attack techniques to uncover server secrets, masked vulnerabilities, and hidden attack surfaces using efficient, real-world methods and open-source tools.
Amplifying Threats: The Role of Multi-Sender Coordination in SMS-Timing-Based Location Inference Attacks
Explore how multiple SMS senders can enhance location inference attacks through timing side channels, revealing improved accuracy and potential security vulnerabilities in mobile networks.