The Swiss Cheese Security Pattern - Building Secure Data Architectures
Adopt a multi-layered approach to data security, minimizing risks through strategic architecture and mindset shifts in asset protection.
Bridging the Dev-Sec Divide: Three Tips for Agile Developers
Discover proven steps to build and grow a DevSec culture in your tech organization, bridging the gap between development and security teams.
Developer Security Essentials
Discover how attackers exploit code vulnerabilities and learn to identify and fix complex security issues efficiently. Participate in a hands-on hacking session to address open source security problems.
Data Security and Storage Hardening in Rook and Ceph
Explore data security and storage hardening in Rook and Ceph. Learn about threat modeling, security zones, encryption, access controls, and infrastructure hardening for robust software-defined storage.
Iterative Threat Modelling - Security in Agile Development
Learn iterative threat modeling for agile development. Explore misconceptions, methodologies, and practical examples using OWASP Juice Shop. Discover effective ways to identify, prioritize, and mitigate security risks.
Detecting Known Unknowns in DevSecOps - A Tailored Defensive Approach
Explore TTP-based threat hunting with the Pandora Project. Learn about tailored defensive solutions, methodology workflows, and practical use cases for detecting known unknowns in cybersecurity.
14 Easy Lessons for Thinking About Complex Adversarial Systems
Explore 14 key insights for analyzing complex adversarial systems, enhancing your understanding of security challenges and strategic thinking in cybersecurity.
Enabling Rack-Scale Confidential Computing Using Heterogeneous Trusted Execution Environment
Explore heterogeneous trusted execution environments for large-scale confidential computing, addressing GPU protection challenges and offering a scalable solution for data-intensive tasks without chip-level modifications.
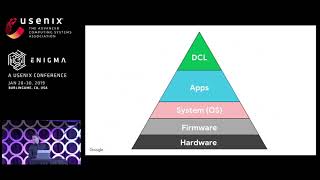
Insider Attack Resistance in the Android Ecosystem
Exploring insider attack threats in mobile ecosystems and Android's multi-level defense strategies, including hardware-level protections and system software transparency to enhance user security.
Architecting for Security in the Cloud - 2017
Discover strategies to identify and close security gaps in cloud applications, building robust architectures that can withstand Internet attacks while maintaining scalability and agility.
Designing Secure Applications in the Cloud - Security Patterns and Best Practices
Explore three security patterns for cloud applications to prevent malicious attacks, protect sensitive data, and manage access control. Learn to design robust, secure cloud services.
Hypervisor-Based Integrity: Protecting Guest Kernels in Cloud Environments
Explore hypervisor-based integrity protection for guest kernels in cloud environments, focusing on threat models, runtime protection, and implementation challenges.
OWASP Security Knowledge Framework - Making the Web Secure by Design
Learn about OWASP's Security Knowledge Framework for designing secure web applications, focusing on proactive security measures and best practices for developers.
Ad Hoc Mutable Infrastructure for Security Management - Cloud Service Security
Explore ad hoc mutable infrastructure for enhanced cloud security management, focusing on active directory identity management and automated threat mitigation techniques.
So, You Want To Use A WebView? - Security Considerations and Best Practices
Explore WebView security challenges, interfaces, testing methods, and threat models. Learn best practices for implementing secure WebViews in mobile applications.
Ten Secrets to Secure Mobile Applications
Discover key strategies for securing mobile apps, focusing on encryption, web service design, and user privacy. Learn to threat model and address top vulnerabilities using OWASP Mobile Top Ten framework.
The Evil Friend in Your Browser - Browser Extension Security Risks
Explore the security risks of browser extensions, their potential for data breaches, and the limitations of current security models. Learn about threat analysis and user protection strategies.
Building a Valid Threat Library for Cloud-Based Applications
Leveraging cloud monitoring and logging to create dynamic threat libraries for Azure and AWS, enhancing application threat models in critical infrastructure sectors like energy and transportation.
Turning Engineers into Extended Blue Team Members - Security Strategies
Strategies for empowering engineers to become part of the security team, including threat modeling, incident-driven learning, and security testing integration into development processes.
OWASP Top 10 - Introduction to Web Application Security Risks
Comprehensive overview of OWASP Top 10, exploring critical web application security risks and effective mitigation strategies for developers and security professionals.
Addressing Evolving Threat Models in Cloud Security with Open Source Software
Explore evolving cloud security threats and learn strategies to address them using open source tools, focusing on context-aware scanning, threat graphs, and efficient alert management.