Great Security Is One Question Away
Discover how asking the right security questions can transform your Python development practices and enhance overall project safety.
Invisible Infiltration of AI Supply Chains: Protective Measures from Adversarial Actors
Explore protective measures against adversarial actors infiltrating AI supply chains. Learn to secure data, models, and pipelines, implement security controls, and mitigate risks in AI systems.
OWASP Cornucopia - Introduction to Application Security Card Game
Explore OWASP Cornucopia, a card game designed to help software developers identify security requirements in web applications, with expert insights from Johan Sydseter.
API Security By Design
Explore API security best practices and design principles to build robust, secure systems with expert insights from Jose Haro Peralta.
How Hacking Works - Web Edition
Explore web exploitation techniques and tools to enhance software security. Learn through gamified environments to build skills for safer development practices.
Threat Modeling at Scale: More Than Shifting Left
Empower developers with scalable threat modeling techniques to enhance application security, save time and money, and make secure development more attainable.
Step-by-Step: Application Security Architecture
Comprehensive guide to application security architecture, covering threat modeling, security controls, and best practices for robust software design and implementation.
Cybersecurity Threats and Models
Explore cybersecurity threats and models, gaining insights into critical security concepts and strategies for protecting digital assets and information systems.
We Are Doing It Wrong: Threat Modeling
Explore common pitfalls in threat modeling and learn how to avoid them. Gain insights from real-world breaches and discover effective strategies for securing software development.
The North Star: Risk-Driven Security - DevSecCon
Discover risk-first threat modeling to identify and prioritize security vulnerabilities, focusing on business risks for effective risk reduction and stakeholder buy-in.
Empowering DevSecOps - Risk-Driven Security and Scaling Application Security
Discover risk-driven security and scale application security across your organization. Learn threat modeling techniques, identify crucial vulnerabilities, and enable business-wide security partnerships.
Exploring Card Games in Threat Modeling - Enhancing Security Posture
Explore innovative card games for threat modeling, including Elevation of Privileges, OWASP Cornucopia, and OWASP Cumulus. Learn how these engaging tools can enhance your organization's security posture through interactive gameplay.
DevSecOps Unveiled: Integrating Security in the Development Lifecycle
Explore DevSecOps principles and practices for seamlessly integrating security into the development lifecycle. Learn to foster collaboration, automation, and shared responsibility for proactive vulnerability management.
SLSA: Enhancing Software Supply Chain Security - More Than Just a Garnish for Your Pipelines
Explore SLSA principles for securing software supply chains. Learn threat models, security levels, and how to contribute to this OpenSSF project for enhanced DevSecOps processes.
(Ab)user Experience: The Dark Side of Product and Security
Explore threat modeling techniques to understand and mitigate potential misuse of digital products by engaging security teams in the product development process.
Securing Applications in the Software Development Life Cycle (SDLC) - Beginner
Aprenda prácticas de codificación segura para mitigar riesgos de seguridad y proteger datos en el desarrollo de software moderno.
Software Supply Chain Security: Definition and Importance - Episode 1
Explore the key pillars of software supply chain security in this comprehensive podcast episode. Gain insights into problem definition, essential terms, and practical implementation strategies for enhancing your organization's security posture.
Protecting Small Businesses from Cyber Attacks - Strategies and Real-World Scenarios
Explore attacker strategies, real-world scenarios, and cost-effective measures to protect small businesses from cyber threats. Learn to engage employees through gamification for enhanced security.
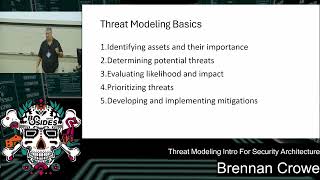
Threat Modeling Introduction for Security Architecture
Aprende a integrar el modelado de amenazas en revisiones anuales de gobernanza y arquitectura de seguridad. Explora conceptos clave como vectores de ataque, superficies de ataque y ciclos de vida de ataques.
Modelling Threats Out in the Open Source - SOOCon23 Security
Explore open-source threat modeling techniques to enhance software security and identify potential vulnerabilities in your projects.
What's Not So New in the New OWASP Top 10 - Devoxx Poland 2022
Explore OWASP Top 10 updates, focusing on insecure design. Learn defense-in-depth strategies, secure design principles, and threat modeling methodologies like STRIDE for improved web application security.