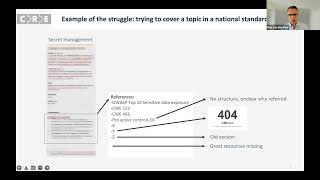
Understanding the Complete Chain of Application Security Using OpenCRE.org
Explore a comprehensive approach to application security using openCRE.org, covering key concepts and best practices for robust software protection.
Real World Security - Software Supply Chain
Explore software supply chain security through a case study on misconfigured registries, threat modeling, and best practices for securing the build-ship-run pipeline.
Attack Tree Vignettes for Containers as a Service Applications - Risk-Centric Threat Modeling
Explore attack tree vignettes and risk-centric threat models for Containers as a Service applications, focusing on security challenges in cloud adoption and containerization.
Software Security Initiative Capabilities - Where to Begin
Explore key capabilities for starting a software security initiative, including penetration testing, code review, and secure design review. Learn benefits, drawbacks, and integration into mature security practices.
Open Source Approaches to Security for Applications and Services - Mozilla Case Study
Explore open-source security approaches for applications and services, covering threat modeling, bug bounties, and measuring security effectiveness in Mozilla's ecosystem.

15 Years of Web Security - The Rebellious Teenage Years
Explore web security's evolution, challenges, and future trends with insights on threat modeling, vulnerability data, and emerging solutions like cyber insurance and security guarantees.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
Everything is Terrible: Building, Configuring, and Securing Software - Three Perspectives
Explore perspectives on building, configuring, and securing software from developers, operations, and security experts. Learn strategies for collaboration, empathy, and optimizing workflows across teams.
Building a Better Hacker to Improve Cybersecurity Defense
Explore how understanding hacker mentality bridges the gap between developers and security teams, leading to more effective cybersecurity strategies and proactive threat prevention.
Leveling Up Your Application Security Program
Learn strategies to enhance your organization's application security program, focusing on key improvements and best practices for robust cybersecurity.
Practical Threat Modeling with Microsoft's Threat Modeling Tool 2016
Learn practical threat modeling using Microsoft's Threat Modeling Tool 2016. Explore data flow-based techniques, risk assessment, and countermeasures for effective application security.
Idiot Proof Is Not Enough: Make It Villain Proof - Application Security
Learn strategies to secure applications against sophisticated attackers, going beyond basic safeguards to create robust, villain-proof systems.
Making SSL Warnings Work - Improving Security and User Experience
Explore strategies to improve SSL warnings in Chrome, focusing on reducing false positives and enhancing user understanding of security threats through clear design and communication.
Threat Modeling - A Brief History and the Unified Approach at Intuit
Unified approach to threat modeling combining STRIDE and asset-based methods. Focuses on identifying assets, attacker profiles, and controls for software architecture and system deployments.
Frameworks and Theories in Application Security - OWASP AppSec Europe 2014
Comprehensive coverage of AppSec Europe 2014 conference, featuring expert talks on anonymous communications, threat modeling, risk analysis, and web security. Insights for developers and security professionals.
Threat Modeling Made Interactive - Using Poirot for Dynamic Security Analysis
Interactive demonstration of Poirot, a tool for modeling and analyzing system security during design phase, enabling real-time threat assessment and mitigation strategies.
AppSecUSA 2014 Builders Track - Friday Sessions
Explore key AppSec topics: mobile security, threat modeling, continuous security, and component vulnerabilities. Gain insights from industry experts to enhance your application security practices.
Fix the Damned Software - Improving Application Security Design
Explore strategies for building security into software development, moving beyond vulnerability discovery to secure design and implementation. Learn from industry experience and BSIMM data.
OWASP Top 10 Mobile Risks: 2014 Reboot
Explore the updated 2014 OWASP Top 10 Mobile Risks, comparing changes since 2011, understanding new threats, and learning recommended fixes for iOS, Android, and Windows Phone platforms.
Next Generation Red Teaming - Integrating Application-Centric Attacks
Explore advanced red teaming techniques integrating application-specific attack surfaces for more realistic and effective security assessments across multiple domains.
Threat Modeling - Key Methodologies and Applications from OSS CIP Perspective
Explore key threat modeling methodologies and their applications in open source civil infrastructure platforms, enhancing security practices for critical systems.