Measuring End-to-End Security Engineering
Introducing a new SDL approach: End-to-End Security Engineering. Covers full product lifecycle, defines 'perfect secure system', and produces metrics to measure security state at each point. Focuses on collective understanding and effectiveness.
Juggling the Elephants - Making AppSec a Continuous Program
Strategies for implementing a continuous AppSec program that integrates security initiatives, enables DevOps, and addresses portfolio-wide coverage while prioritizing risks and fostering continuous improvement.
Offensive Threat Models Against the Supply Chain
Applying adversarial threat models to supply chain systems, focusing on realistic attack patterns and emulating cybercriminal tactics to enhance defensive measures and risk reduction strategies.
A Pragmatic Approach for Internal Security Partnerships
Strategies for effective security partnerships with engineering teams, focusing on shared risk views, automation, and integrating security into product roadmaps.
A Seat at the Table: Effective Security Collaboration in DevOps - AppSecCali 2019
Discover effective collaboration strategies for security professionals in the DevOps era, focusing on new skills, approaches, and speed to engage early and add value in software development.
Threat Modeling with PASTA - Application Security Case Studies
Explore risk-centric threat modeling using PASTA methodology, with case studies in IoT, E-Commerce, and Mobile Applications. Learn to align design and coding techniques with application use cases and potential threats.
Embedding GDPR Into the Secure Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, and breach notification processes.
Threat Modeling for Mobile Applications
Explore threat modeling techniques for mobile applications with expert Amit Sethi. Learn to identify and mitigate security risks in mobile development.
Adding Privacy to Threat Modeling - Game On!
Explore how LogMeIn extended the Elevation of Privilege card game to incorporate privacy considerations, bridging knowledge gaps between development, security, and compliance teams through gamification.
Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.
Practical Threat Modeling for Real-World and Cloud Situations in Hybrid Work Environments
Practical guide to threat modeling for cloud and hybrid work environments, covering creation, identification, addressing, and validation of threats with real-world examples and tools.
Normalizing AppSec Issues for Contextual Risk-Based Prioritization at Enterprise Scale
Explore a new approach to Application Security that focuses on critical risks by incorporating contextual intelligence, improving efficiency and delivery in enterprise-scale programs.
Threat Modeling of Containerized Applications - Three Levels of Complexity
Optimize threat modeling for containerized applications, focusing on efficiency, new dimensions, and real-world impact. Learn to measure success and implement incremental improvements in application security.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
Flipping the Script on Application Security
Explore innovative approaches to application security, challenging traditional methods and introducing fresh perspectives for more effective protection strategies.
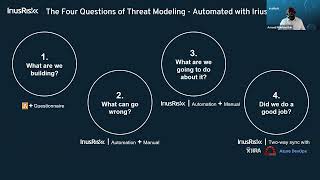
Using IAC to Accelerate Threat Modeling
Explore innovative techniques for accelerating threat modeling using Infrastructure as Code (IAC), enhancing security practices in software development and deployment.
Evolving Threat Modeling Through the Open Threat Model Format
Explore the Open Threat Model Format and its role in advancing threat modeling practices for improved cybersecurity risk assessment and mitigation strategies.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Threat Modeling In and For Your Organization
Comprehensive guide to implementing threat modeling practices within organizations, enhancing security strategies and fostering a proactive approach to identifying potential vulnerabilities.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.