MISP Workflow - An Improved Way to Support CTI Pipelines
Enhance CTI pipelines with improved MISP workflow techniques. Learn efficient strategies for threat intelligence management and streamline your cybersecurity processes.
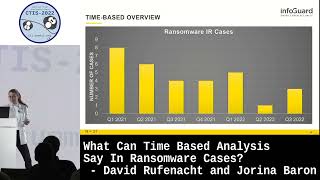
What Can Time-Based Analysis Reveal in Ransomware Cases?
Explore time-based analysis techniques for investigating ransomware incidents, uncovering crucial insights to enhance cybersecurity strategies and incident response.
Effectiveness in Simplicity - The Taskmasters APT
Explore the Taskmasters APT's effectiveness through simplicity in this concise presentation by Elmar Nabigaev, focusing on key insights and practical applications.
The Glitch in the Matrix
Explore advanced malware analysis techniques and cutting-edge evasion methods used by sophisticated threats. Gain insights into detecting and countering elusive malicious software.
Introducing HAMISPA - High Availability MISP in AWS
Learn to deploy a highly available MISP (Malware Information Sharing Platform) in AWS for enhanced threat intelligence sharing and collaboration.
Threat Intelligence Contextualized Knowledge Base
Explore advanced threat intelligence techniques using contextualized knowledge bases to enhance cybersecurity defenses and improve incident response capabilities.
WHIDS Integration with MISP
Explore WHIDS integration with MISP for enhanced threat intelligence sharing and incident response capabilities in cybersecurity operations.
The New Indicator Scoring Method Introduced in MISP 2.4.116
Explore the updated indicator scoring system in MISP 2.4.116, enhancing threat intelligence analysis and improving decision-making for cybersecurity professionals.
KillTheHashes - 30 Million Malware DNA Profiling Exercise - Hack.lu 2016
Explore malware profiling techniques and tools for identifying unique digital fingerprints, enabling early detection and categorization of new threats through characteristic family analysis.
Visualizing MISP and ATT&CK Data in Maltego
Explore techniques for visualizing threat intelligence data from MISP and ATT&CK frameworks using Maltego, enhancing cybersecurity analysis and decision-making.
MISP Project - One Year of Improvements
Explore recent advancements in the MISP threat intelligence platform, including enhanced features, improved performance, and expanded capabilities for cybersecurity professionals.
Simple Analysis Using Passive DNS
Explore passive DNS analysis techniques for threat detection and investigation, featuring insights from industry experts on leveraging pDNS data effectively.
Central Intelligence Vetting Platform - MISP Summit 2018
Explore the Central Intelligence Vetting Platform presented at MISP Summit 2018. Learn about innovative approaches to intelligence analysis and information sharing in cybersecurity.
Enrichment and Quality IoC Creation from OSINT
Explore techniques for creating high-quality IoCs from open-source intelligence and enhancing threat data enrichment in MISP for improved cybersecurity analysis and information sharing.
Quantitatively Comparing APTs with MISP - MISP Summit 2018
Explore quantitative methods for comparing Advanced Persistent Threats using MISP, enhancing threat intelligence analysis and cybersecurity strategies.
Master of Clusters - MISP Summit 2018
Explore advanced clustering techniques for threat intelligence data analysis and visualization in MISP, enhancing cybersecurity insights and decision-making processes.
From Twitter to MISP - Catching and Qualifying IOCs
Explore a method for capturing and qualifying Indicators of Compromise (IOCs) from Twitter and integrating them into MISP for enhanced threat intelligence.
Building a Security Ecosystem with MISP and McAfee
Explore the integration of MISP and McAfee technologies to enhance threat intelligence sharing and create a robust security ecosystem for improved cybersecurity.
The Holy Grail for STIX and MISP Format - MISP-STIX
Explore MISP-STIX integration for enhanced threat intelligence sharing, focusing on data conversion and interoperability between MISP and STIX formats.

CTI Operational Procedures with Jupyter Notebooks and MISP
Learn to enhance Cyber Threat Intelligence operations using Jupyter Notebooks and MISP. Explore practical techniques for data analysis, visualization, and threat information sharing.
DocIntel - A Context-Centric Threat Intelligence Platform
Explore a context-centric threat intelligence platform for enhanced cybersecurity analysis and decision-making in this insightful presentation by Antoine Cailliau.