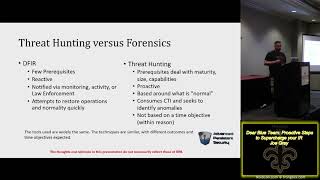
Dear Blue Team - Proactive Steps to Supercharge Your IR
Proactive strategies for enhancing incident response, covering threat intelligence, forensics, and threat hunting. Explores tools and techniques for effective cybersecurity defense.
Applying Thermodynamic Principles to Threat Intelligence
Explore thermodynamic principles applied to cyber threat intelligence, enhancing analysis and decision-making in cybersecurity through innovative conceptual frameworks.
The Marriage of Threat Intelligence and Incident Response or Threat Hunting for the Rest of Us
Learn to integrate threat intelligence with incident response and threat hunting, exploring detection, analysis, containment, and eradication strategies for effective cybersecurity.
Advanced Attackers Hiding Inside Encrypted Traffic at the Endpoint
Explore advanced techniques used by attackers to hide within encrypted traffic at endpoints, covering threat evolution, APTs, and emerging cybersecurity challenges.
The Hybrid Analyst - How Phishing Created A New Type of Intel Analyst
Explore how phishing attacks have led to the emergence of hybrid intelligence analysts, combining threat intelligence and phishing analysis skills for enhanced cybersecurity.
Intelligence Creating Intelligence - Leveraging What You Know to Improve Finding What You Don't
Explore techniques for creating and leveraging threat intelligence, from data collection to implementation, to enhance cybersecurity efforts and improve threat detection capabilities.
Stable 15 Threat Intel On The Fly Tazz
Learn rapid threat intelligence techniques to enhance cybersecurity defenses and respond effectively to emerging threats in real-time.
Stable 36 Mirai - Satori OMG and Owari IoT Botnets - Oh My
Explore Mirai-based IoT botnets like Satori, OMG, and Owari. Learn about their configurations, obfuscation techniques, and exploitation methods for improved network security.
Cyber Intelligence - There Are No Rules and No Certainties
Explore cyber intelligence frameworks, attribution techniques, and practical approaches to managing and automating intelligence processes in the digital domain.
Comparing Malicious Files
Explore techniques for comparing malicious files, including sample identification, shared engines, and various metadata analysis methods to enhance threat detection and incident response.
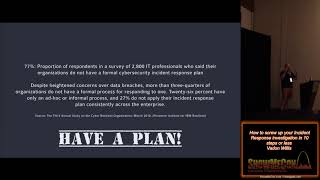
How to Screw Up Your Incident Response Investigation in 10 Steps or Less
Learn common pitfalls in incident response investigations and how to avoid them, improving your cybersecurity preparedness and effectiveness in handling breaches.
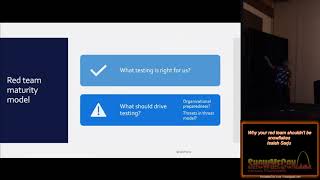
Why Your Red Team Shouldn't Be Snowflakes
Explore strategies for effective red team operations, including maturity models, threat intel, and testing types. Learn to enhance cybersecurity preparedness and level up quickly.
The TIP of the Stinger - Efficiently Using Threat Intelligence With TheHive
Explore efficient threat intelligence utilization with TheHive platform, enhancing cybersecurity practices and incident response capabilities.
Well What Have We Here - A Year of Cyber Deception, Attribution, and Making Attackers Rethink Their Approach
Explore cyber deception techniques, attribution strategies, and methods to disrupt attacker behavior in this comprehensive cybersecurity presentation.
Stable 34 - Waking Up the Data Engineer in You
Explore threat intelligence, attack techniques, and data analysis for enhanced cybersecurity. Learn from an expert about remote services, OSEM, and effective data modeling strategies.
Judo Threat Intelligence - Frank Angiolelli
Explore threat intelligence principles, exploit kits, and custom alert building. Learn tactical actions and AI applications in cybersecurity from an experienced professional.
The Spider Economy - Emotet, Dridex, and TrickBot Oh My
Explore the interconnected world of malware families Emotet, Dridex, and TrickBot, understanding their evolution, tactics, and impact on cybersecurity landscapes.
Dance Fancybear Dance - A Study in macOS Cat Self
Explore macOS security through the lens of art forgery, threat profiling, and red teaming. Learn practical techniques for information gathering, software development, and testing in cybersecurity.
Lend Me Your IRs
Explore incident response techniques and best practices for effective cybersecurity management in this informative presentation by Matt Scheurer at BSides Cleveland 2021.
Chats, Cheats and Cracks - Abuse of Collaboration Platforms in Malware Campaigns
Explores abuse of collaboration platforms like Discord and Slack in malware campaigns, covering distribution methods, command and control, and protective measures.
Targeted Automation for Malware Analysis
Explore targeted automation techniques for efficient malware analysis using open-source tools, enhancing threat intelligence and collaboration within organizations.