Behaviors and Patterns of Rogue Hosting Providers
Exploration of rogue hosting providers' behaviors, patterns, and impact on cybercrime. Insights into threat intelligence techniques for identifying and combating abusive hosting services, with focus on Dutch infrastructure.
Insight Into TTPs Of A Middle Eastern Threat Actor
Insight into Middle Eastern threat actor MuddyWater's tactics, including spear-phishing, backdoors, and cyber espionage. Explores recent tool evolution, obfuscation techniques, and prevention strategies.
Hey Attacker! I Can See You!
Exploring cloud-scale deception technology to track and analyze attackers, enhancing Azure security through psychological and technical approaches for better threat intelligence and user protection.
Wash Your Hands! This Is Bot Country
Network security challenges in remote work: risks, tools, and strategies for protecting expanded perimeters from IoT vulnerabilities and global threats. Tips for forensics and threat intelligence.
Zebrocy’s Multi-Language Malware Salad
Explore Zebrocy's unique APT tactics, multi-language malware, and evolving techniques in this cybersecurity analysis by Kaspersky's Kurt Baumgartner.
Following APT OpSec Failures
Explore APT OpSec failures, uncovering personal connections, privacy issues, and confirmed links in cyber espionage operations. Gain insights into evolving tactics and vulnerabilities.
Distributors, Developers and Tools Behind Black Flag Comms
Explore tools, practices, and attribution in black flag communications, focusing on ISIS's digital presence and media strategies.
Tracking Internet Threats by Visualizing IP and DNS Data
Visualize IP and DNS data to track Internet threats using innovative techniques like particle physics models and network graphs for enhanced cybersecurity intelligence.
Cyber in a World of Cloud
Explore cloud security challenges and advantages, including threat adaptation, data-driven defense, and self-protection mechanisms in hyperscale environments.
The Billion Dollar APT
Explore the inner workings of a sophisticated billion-dollar cybercrime operation, its methods, and how law enforcement combats these high-stakes digital threats.
Desert Falcons on a Cyberhunt
Explore the tactics of cyber espionage group Desert Falcons, including their infection methods, social media exploitation, and targeted campaigns in the Middle East.
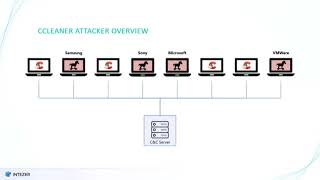
Supply Chain Attack Through CCleaner - Evidence Aurora Operation Still Active
Análisis detallado del ataque de cadena de suministro a CCleaner, explorando su sofisticación, objetivos y conexiones con el grupo APT17/Axiom, destacando la persistente amenaza de ataques estatales avanzados.
The Next Gen PlugX - ShadowPad - A Dive into the Emerging China-Nexus Modular Trojan, Pangolin8RAT
Explore the emerging Pangolin8RAT trojan, its potential as a successor to PlugX and ShadowPad in Chinese cyber operations, and its attack timeline from 2020 to 2021.
Who Did It - How We Attributed Campaigns of a Cyber Mercenary
Uncover the tactics of a cyber mercenary operating in underground forums, exploring their global campaigns, targeting methods, and strategic operations from 2016-2021.
No Royal Road - Notes on Dangerous Game
Explores attribution fatigue in cybersecurity, examining nation-state hacking, stolen toolchains, and the evolution of cyber threats beyond espionage into active operations.
Why the World Must Take Notice of the Rising Asian Dark Web
Explore the rising Asian dark web markets, their usage patterns, and user motivations. Gain insights into new research findings across various Asian countries' dark web landscapes.
Worm Charming - Harvesting Malware Lures for Fun and Profit
Explore YARA rules for extracting malware samples from VirusTotal, learning techniques to identify attacker infrastructure and analyze real-world threats.
Don't Eat Spaghetti with a Spoon - An Analysis of the Practical Value of Threat Intelligence
Explore the effectiveness of Threat Intelligence in predicting Internet malicious activity through analysis of over a million indicators across diverse real-world network sensors.
Charged by an Elephant - An APT Fabricating Evidence to Throw You in Jail
Explore ModifiedElephant's decade-long operation, incriminating activists through planted evidence. Uncover the concerning ties to commercial surveillance and multiple regional threat actors targeting victims.
To Loot or Not to Loot - That Is Not a Question When State Nexus APT Targets Online Entertainment
Dissecting APT attacks on online entertainment companies, revealing espionage motives beyond financial gain. Analyzes 20+ operations since 2018, exposing tactics and implications for data-rich targets.

SideWinder Uncoils to Strike
Explore the aggressive SideWinder threat actor's tactics, infection chain, and infrastructure. Learn about their evolving techniques and effective mitigation strategies.