Improving Collaboration and Reducing Risk in Security Operations - Part 2
Explore strategies for enhancing IT-business collaboration and risk management in organizations of all sizes, with insights from security leaders on SOC challenges and solutions.
How AI Impacts Reconnaissance and Bug Bounties in Cybersecurity
Exploring AI's impact on cybersecurity, this interview covers its role in bug bounties, potential risks, job market effects, and defensive strategies against malicious AI use.
Ransomware in Action - MedusaLocker ReadText34
Explore MedusaLocker ransomware's behavior and tactics through dynamic analysis, gaining insights into its encryption process and file manipulation techniques.

SOC Analyst: Top Interview Questions and Answers for Security Operations Center - 2024
Master SOC analyst interview skills with scenario-based prep on threat detection, incident response, and vulnerability management. Gain practical insights to excel in security operations and stand out to potential employers.
Detection Engineering Demystified - Building Custom Detections for GitHub Enterprise
Learn to build custom detections for GitHub Enterprise, focusing on identifying attacker behavior and protecting intellectual property through practical Detection Engineering techniques.
The B-Side of Ransomware - Exploring Lesser-Known Threats
Explore lesser-known ransomware attacks, their tactics, and why they failed to gain notoriety. Gain insights into the evolving threat landscape and enhance cybersecurity preparedness against diverse potential attacks.
Using Game Theory to Study the Evolution of Ransomware - Checkmate
Explore ransomware evolution through game theory, analyzing attacker-defender dynamics and recurring tactics to improve cybersecurity strategies and balance the odds against multiple threats.
Operation So-seki: Investigating Pro-Russian Hacktivist DDoS Attacks
Investigación detallada sobre un grupo hacktivist pro-ruso, sus ataques DDoS y tácticas. Análisis de infraestructura, herramientas y contramedidas basado en el seguimiento de más de 1000 ataques durante un año.
Intel-Driven Adversary Simulation for A Holistic Approach to Cybersecurity
Explore intelligence-driven adversary simulation for comprehensive cybersecurity risk management. Learn to integrate threat intelligence, best practices, and cross-functional teams to enhance organizational security posture.
Practical Steps to False Positive Reduction and Benign File Analysis
Learn efficient techniques for identifying false positives and analyzing clean files in malware analysis. Gain actionable tips from real-world examples to enhance your workflow and save time and resources.
Leveraging Online Sandboxes for Triage Analysis - MM#07
Explore popular online sandboxes for malware analysis, including AnyRun, Triage, and VirusTotal's behavioral output. Learn effective techniques for leveraging these tools in investigations.
Tales from Incident Response - Unmasking the Threat Actor's Inner Sanctum
Unmasking threat actors' inner workings through incident response tales. Gain insights into cybersecurity challenges and strategies from a principal advisor's real-world experiences at a major hacking conference.
War Stories from the SOC - Cybersecurity Incident Response Lessons
Cybersecurity expert shares real-world experiences from Security Operations Center, offering insights into threat detection, incident response, and best practices for defending against cyber attacks.
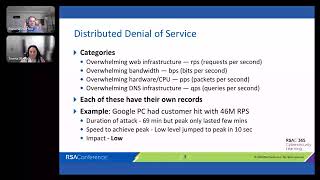
Navigating Record-Breaking DDoS Attacks - Lessons Learned and Best Practices
Experts share insights on combating evolving DDoS attacks, discussing attacker motivations, methods, and best practices for defending against increasingly complex and frequent threats.
Mapping APT TTPs with MITRE ATT&CK Navigator
Explore MITRE ATT&CK Navigator for planning and orchestrating Red Team operations, enhancing cybersecurity strategies with advanced threat mapping techniques.
Introduction to the MITRE ATT&CK Framework
Comprehensive overview of MITRE ATT&CK framework for cybersecurity professionals, covering its application in red team and blue team operations with practical insights and resources.
Top Five Security Tips for Organizations
Discover five essential security tips for organizations, covering strong authentication, minimalism, updates, backup isolation, and staying informed on threats and best practices.
A Blueprint for Modern Security Operations
Discover a fresh approach to cybersecurity, combining reactive and proactive techniques with AI to effectively defend against sophisticated threats.
Power of AI: DevSecOps and Cloud Artifact Signing Explored - Sessions 1 and 2
Explore AI's impact on DevSecOps and cloud artifact signing. Learn how AI enhances security automation, vulnerability scanning, and threat detection. Discover tools for ensuring trust and integrity in cloud environments.
Mapping Your External Attack Surface: Illuminating Hidden Vulnerabilities
Illuminate hidden assets and vulnerabilities in your external attack surface using powerful reconnaissance tools. Proactively defend your digital perimeter and stay ahead of potential threats.
What's Next for Security Professionals - Innovations in Threat Prevention and AI-Driven Security
Explore the convergence of security capabilities, AI-driven innovations, and insights from industry leaders to transform your organization's security approach.