
Cyber Threat Hunting and DFIR - Understanding Malware Attack Steps
Explore cyber threat hunting and DFIR techniques, including malware attack paths, detection methods, and essential skills for strengthening organizational cybersecurity defenses.
Decoding Security Operations - A Complete SOC 101 Crash Course
Master Security Operations Center essentials: monitoring, threat detection, incident response. Gain insights to enhance organizational security posture and understand key SOC roles in modern cybersecurity.
XZ Backdoor - Navigating the Complexities of Supply Chain Attacks Detected by Accident
Explore the intricacies of supply chain attacks through the lens of the XZ Backdoor incident, uncovering detection methods and implications for cybersecurity professionals.
Fighting Digital Threats in the Age of AI
Explore strategies to combat evolving digital threats in the AI era, focusing on cybersecurity challenges and innovative defense mechanisms for the modern technological landscape.
PhishDefend - A Reinforcement Learning Framework for AI-Augmented Phishing Detection and Response
Explore a reinforcement learning framework for measuring AI-augmented phishing detection and response, enhancing cybersecurity strategies against evolving threats.
ZERO-RULES Alert Contextualizer and Correlator for Detecting Multi-Stage Cyber Attacks
Leveraging AI models to connect security events into MITRE ATT&CK campaigns, enhancing detection of multi-stage cyber attacks and shifting focus from individual incidents to targeted campaigns.
The Double-Edged Sword of AI in Cybersecurity
Explore AI's dual impact on cybersecurity: enhancing defenses while posing new threats. Gain insights from expert Alexander Benoit on navigating this complex landscape in the digital age.
Stay Ahead of API Security Threats with Machine Learning Detection
Explore ML-powered API security controls to detect abuse, misconfigurations, and business logic attacks without adding overhead. Learn to protect sensitive data and critical business information.
A Blueprint for Modern Security Operations
Discover a fresh approach to cybersecurity, combining reactive and proactive techniques with AI to effectively defend against sophisticated threats.
Breaching the Depths of the Abyss: Exposing Rootkits - Track 2, Session 4
Dive deep into rootkits: explore their inner workings, detection techniques, and countermeasures. Learn to identify and neutralize these stealthy threats using advanced tools like Living Off The Land Drivers.
Building a Canarytoken to Monitor Windows Process Execution - Track 2
Explore building Canarytokens to monitor Windows process execution, creating alerts for unexpected commands and strengthening defense against potential attacks.
Detection as Code - Buzzword or Panacea?
Explore the reality of Detection-as-Code in cybersecurity. Separate hype from facts and understand its potential benefits for blue teams and threat detection programs.
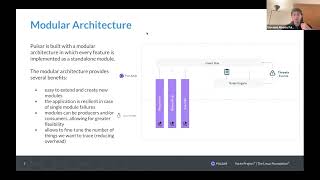
Embedded Runtime Security with Pulsar - YPS 2023.11
Explore Pulsar, an eBPF-powered threat detection system for IoT. Learn its architecture, capabilities, and integration with Yocto Project for enhanced embedded system security.
Weak Supervision and Next-Gen AI-Based Threat Detection
Explore weak supervision for efficient AI-based threat detection in network security, leveraging analyst heuristics to build predictable models and overcome traditional machine learning challenges.
Dragos Platform: Asset Inventory for Enhanced Detection and Response in OT Cybersecurity
Explore advanced OT cybersecurity with Dragos Platform's enhanced asset inventory, vulnerability management, and threat detection capabilities for industrial environments.
Cyber Physical Systems and Mobile Security - Threat Landscape and Innovations
Explore cyber security challenges in physical systems and mobile devices. Learn about innovative edge computing and AI solutions for threat detection, containment, mitigation, and recovery.
Sbud - Information Visualization in Information Security
Explore innovative data visualization techniques for enhancing information security analysis and communication, presented by expert Ange Albertini at Hack.lu 2023.
Cloudy with a Chance of Persistence - 2019
Explore cloud persistence techniques and their impact on security in modern computing environments.
Strengthen Resilience With Identity Innovations in Azure Active Directory
Discover Azure AD innovations for enhanced resilience against sophisticated cyber attacks, including platform improvements, advanced threat detection, and expanded digital estate security.
Security Chaos Engineering for Cloud Native Infrastructure
Explore Security Chaos Engineering for proactive cloud-native security. Learn to inject controlled faults, analyze mechanisms, identify blind spots, and enhance resilience against cyber threats.
Purple Teaming and Adversary Emulation in the Cloud with Stratus Red Team
Explore cloud-native adversary emulation with Stratus Red Team. Learn to identify and reproduce malicious activities in AWS and Kubernetes, enhancing threat detection capabilities for cloud environments.