Robot vs Robot: The Future of Automated Cyber Attacks and Defense
Explore the future of cybersecurity as automated malware campaigns face off against AI-powered defenses. Learn how the battle between good and bad AI will shape the landscape of digital security.
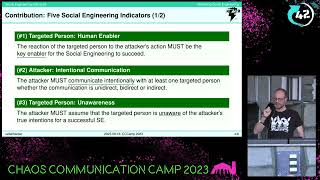
Identifying Social Engineering - Five Key Indicators
Explore five key indicators to identify social engineering in real-world scenarios, literature, and experimental design, enhancing your ability to recognize and mitigate manipulation tactics.

Flare-On FireEye 2018 CTF - Malware Analysis of Flare Minesweeper
Expert malware researcher Amr Thabet discusses the Flare-On FireEye 2018 CTF challenge, providing insights into malware analysis techniques and sharing experiences from high-profile cybersecurity investigations.
Installing and Configuring Suricata for Intrusion Detection
Learn to install and configure Suricata, a powerful open-source threat detection engine combining IDS, IPS, and network security monitoring for enhanced cybersecurity protection.
Installing and Configuring Wazuh for SIEM - Blue Team Operations
Learn to set up Wazuh SIEM for detecting intrusions, attacks, and malicious activity. Covers installation and agent configuration on Windows and Linux for effective security data management.
Unified SOC - Centralized Security Data with OT Visibility for Intelligence-Driven Investigations
Experts discuss unifying Security Operations Centers by integrating OT cybersecurity, threat intelligence, and advanced technologies for comprehensive visibility and efficient investigations in industrial environments.
Hunting Down the Monsters Hidden in Your Software Supply Chain
Uncover and mitigate hidden threats in your software supply chain. Learn effective strategies to enhance security and protect against vulnerabilities.
Do No Harm: OT-Native Approach for Network Monitoring and Cybersecurity
Explore seven principles of OT cyber-network visibility and monitoring for effective cybersecurity in industrial environments. Learn to implement a tailored approach that protects critical infrastructure while maintaining operational integrity.
Next-Gen Detection: Harnessing LLMs for Sigma Rule Automation
Explore innovative approaches to automate Sigma rule generation using LLMs, comparing techniques like RAG, fine-tuning, and prompt-chaining for enhanced threat detection efficiency.
Finetuning Large Language Models for Security Log Detections
Explore finetuning LLMs for advanced security log detection, moving beyond traditional signature-based methods to enhance threat identification capabilities.
Skynet the CTI Intern: Building Effective Machine Augmented Intelligence
Explore integrating LLMs in cybersecurity intelligence, enhancing analyst efficiency while recognizing AI limitations. Learn to create a symbiotic human-AI relationship for proactive defense.
Will Machine Learning Replace the WAF?
Explore the potential of machine learning to revolutionize web application firewalls, examining its capabilities, limitations, and impact on cybersecurity.
AI Driven Automated Security Orchestration in Heterogeneous 6G Networks
Explore AI-driven security orchestration for 6G networks, focusing on automated threat detection and response in complex, heterogeneous environments.
Big Data and Analytics Strategy for Cybersecurity and Privacy
Explore advanced analytics strategies for cybersecurity and privacy, including threat detection, SOC streamlining, and data redaction. Learn to leverage big data and ML for proactive security in modern enterprises.
Infostealer Malware - Understanding the Threat and Impact
Explore the dangers of infostealer malware and learn effective defense strategies. Gain insights into its mechanisms, potential impacts, and ways to protect your digital assets.
Everything Everywhere All at Once - A Guide to Alert Triage and Analysis
Learn effective alert triage and analysis techniques for incident response, including basic triage methods and an information collection checklist to make informed decisions during overwhelming situations.
Hiding in Plain Sight - Hunting Volt Typhoon Cyber Actors
Explore Chinese cyber actors' tactics and defense strategies with experts from FBI, NSA, CISA, and Microsoft. Learn to identify and protect against Volt Typhoon's stealthy network infiltrations.
Unifying XDR and SIEM: A New Era in Security Operations
Explore innovations in AI, attack disruption, threat intelligence, and cloud security to enhance threat detection and response, boosting productivity for security teams.
Oh My Phish - Cybersecurity Awareness and Phishing Prevention
Explore advanced phishing techniques and defense strategies with cybersecurity experts Theram and Dhruv Bisani in this insightful Security BSides London presentation.
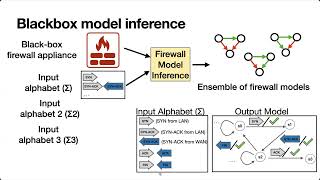
A Modular Generalizable Workflow for Uncovering Evasion Attacks Against Stateful Firewalls
Explore a modular workflow for identifying evasion attacks against stateful firewalls, enhancing network security and threat detection capabilities.
Automating Security Monitoring
Explore efficient security monitoring through automation techniques to handle increasing data volumes, complex architectures, and sophisticated threats while reducing alert fatigue.