
Vulnerabilities in Application Whitelisting - Malware Case Studies
Explores vulnerabilities in application whitelisting through malware case studies, offering insights into security flaws and potential exploits in whitelisting systems.

Malware Management Framework - Detecting WinNTI
Explore a Malware Management Framework for detecting threats like WinNTI, presented by Michael Gough at BSidesLV 2013. Learn effective strategies for cybersecurity and malware detection.
Defense Evasion Modeling - BSidesLV 2013
Explore defense evasion modeling techniques to enhance cybersecurity strategies and stay ahead of evolving threats in this insightful presentation from BSidesLV 2013.

Phish Fights and Not So Long Nights - Integrating Security Onion and Sublime Platform
Explore integration of Security Onion and Sublime Platform for enhanced email security. Learn to triage alerts, investigate suspicious emails, and correlate data for comprehensive defense against email-based attacks.
Big Attacks Equal Big Data - Cybersecurity Insights
Explore the intersection of big data and cybersecurity, focusing on large-scale attacks and their implications for data management and protection strategies.
Ambush - Catching Intruders at Any Point
Learn advanced techniques for detecting and intercepting network intruders using the Ambush system, enhancing your cybersecurity skills and defensive capabilities.
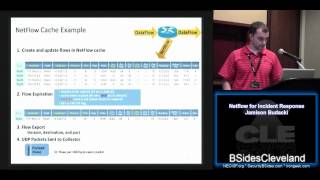
Netflow for Incident Response
Learn to leverage Netflow data for effective incident response, enhancing network security and threat detection capabilities.
Building the Next Generation IDS with OSINT
Explore innovative techniques for enhancing intrusion detection systems using open-source intelligence, improving network security and threat detection capabilities.

Role of Forensic Triage in Cyber Security Trends 2022
Explore forensic triage's crucial role in 2022 cybersecurity trends, enhancing incident response and digital investigation efficiency in an evolving threat landscape.
Cybersecurity Threats and Recommendations for the Electric Power Sector
Overview of cybersecurity threats in electric power, analysis of Biden's 100-day OT security plan, and recommendations for improving threat detection and response in industrial control systems.
5 Key Questions to Accelerate Your OT Cybersecurity Program
Explore a programmatic approach to implementing effective OT cybersecurity, covering visibility, detection, and response. Learn about integrated technologies, threat prevention, and bridging IT-OT gaps.
Bridging the OT Data to Visibility Divide in Industrial Cybersecurity
Explore how Asset Visibility, Network Visibility, and Threat Detection work together to form a strong defense for your entire IT/OT network in industrial cybersecurity.
Securing the Future of Industrial Control Systems: Challenges and Best Practices in OT Cybersecurity
Explore OT cybersecurity challenges, best practices, and industry insights with experts from Dragos, Fortinet, and Schneider Electric as they discuss IT-OT convergence and industrial security essentials.
Detecting and Understanding Unusual Network Activity in Plant Environments
Explore techniques for identifying assets, understanding threats, and guiding incident response in interconnected plant environments to ensure safe and reliable output.
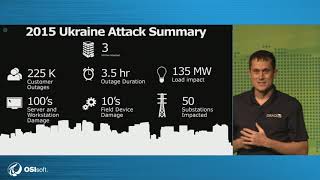
Utilizing Operations Data for Enhanced Cyber Threat Detection
Enhancing industrial control system security by integrating operational data with threat detection platforms for improved situational awareness, faster threat elimination, and better incident response.
Uncovering Industrial Control System Threat Activity Groups
Explore eight industrial threat groups, their tactics, and Dragos' approach to ICS threat detection. Learn how intelligence-driven analytics enhance cybersecurity in critical infrastructure.
Four Types of Threat Detection in Industrial Security
Explore four threat detection types for industrial security, their derivation, and applications. Learn to identify optimal methods for your organization's ICS and IIoT environments.
Dragos ICS Threat Detection and Response Platform Demo
Comprehensive demo of Dragos platform for industrial cybersecurity, showcasing passive monitoring, threat detection, alerts, case management, and guided response with integrated intelligence and expertise.
Detection and Responding to ICS Threats with the Dragos Platform
Explore intelligence-driven ICS threat detection and response using the Dragos platform, integrating OT/IT needs for comprehensive industrial cybersecurity beyond anomaly detection.
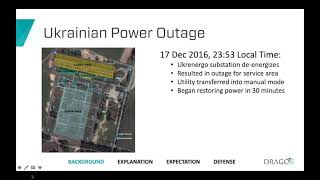
Analyzing and Understanding CRASHOVERRIDE - ICS Cybersecurity Webcast
Comprehensive analysis of CRASHOVERRIDE malware framework, exploring its impact on grid operations, technical details, and mitigation strategies for ICS cybersecurity professionals.
Effectively Investing in Cybersecurity During Digital Transformation
Explore cybersecurity strategies for manufacturing, including technology options, program building, and ransomware protection. Learn to navigate digital transformation challenges and enhance security measures.