Estrategias de Detección de Cyber-Amenazas
Explora estrategias avanzadas para detectar ciberamenazas modernas, analizando objetivos, métodos y herramientas de adversarios en ataques como Loaders, Trojans, Info Stealers y Ransomware.
Decifrando Incident Response
Explore estratégias e melhores práticas para fortalecer defesas e mitigar riscos no cenário digital em evolução, abordando efetivamente desafios emergentes de cibersegurança.
Certificate Transparency: Detecting Malicious Certificates and Phishing Attacks
Explore Certificate Transparency to protect your website from impersonation attacks. Learn integration techniques for monitoring systems and detecting malicious TLS certificates.
Spotless Sandboxes: Evading Malware Analysis Systems Using Wear-and-Tear Artifacts
Explore techniques for evading malware analysis systems by exploiting wear-and-tear artifacts on real devices, with insights on detection accuracy and potential defensive strategies.
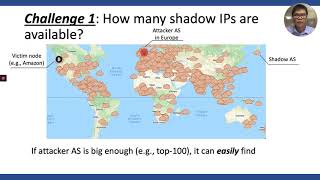
A Stealthier Partitioning Attack Against Bitcoin Peer-to-Peer Network
Explores a stealthy partitioning attack on Bitcoin's P2P network, exploiting network topology to influence node connections without routing manipulation, posing risks for cryptocurrency security.
Monitoring Endpoints, Binary Exploitation, and Continuous Recon - Security Discussion
Explore endpoint monitoring, binary exploitation, and continuous reconnaissance with insights from @Mrtuxracer. Gain valuable knowledge on advanced cybersecurity techniques and strategies.
Detecting and Controlling Rogue Third-Party Scripts in Web Applications
Explore web supply chain attacks, their impact on sensitive data, and strategies to detect and prevent rogue third-party scripts from compromising web application security.
Tangled Web: Defense in Deception - 2017
Explore defensive deception strategies for web applications, including tools and techniques to detect, confuse, and corral attackers. Learn to plan, execute, and monitor effective deception in cybersecurity.
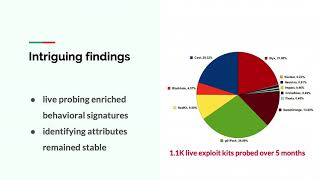
Adventures with Cybercrime Toolkits - Insights for Pragmatic Defense
Explore pragmatic defense strategies against cybercrime toolkits, combining reactive, proactive, and offensive approaches to counter threats and leverage criminals' weaknesses.
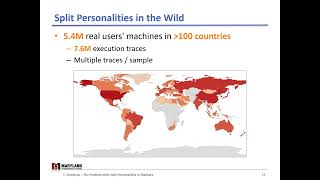
When Malware Changed Its Mind - How Split Personalities Affect Malware Analysis and Detection
Explore the impact of malware behavior variability on analysis and detection techniques, based on a large-scale study of 5.6 million hosts worldwide.
AI and Cyber Security - Mark Menzies, Check Point
Explore AI's impact on cybersecurity, including advancements in threat detection, campaign hunting, and context-aware systems. Learn how AI is revolutionizing the field and enhancing accuracy.
Using DevOps Practices to Implement a Full Route-to-Live for SIEM Platforms
Explore DevOps practices for implementing full route-to-live in SIEM platforms. Learn about threat detection, adaptive hunting, and version control for enhanced cybersecurity.
Digital Investigator: Introduction to Intrusion Detection Systems (IDS)
Learn essential IDS concepts, network security terminology, and threat detection techniques. Explore network-based IDS and simple Snort rules for effective log analysis and intrusion prevention.
Building Cyber Resilience with Microsoft Security Stack
Learn to develop a comprehensive cybersecurity strategy using Microsoft Security Stack. Gain insights on proactive measures and reactive actions to protect your organization from modern threats and enhance cyber resilience.
SIEM and XDR: Automating Threat Detection and Response
Explore Microsoft's integrated SIEM+XDR solution for advanced threat detection and automated response, designed to protect environments end-to-end and stay ahead of sophisticated adversaries.
Terminal Cornucopia: Demystifying The Mullet - Lecture 4
Explore innovative security vulnerabilities in airport terminals and learn about unconventional weapon creation using everyday items, as demonstrated by security researcher Evan Booth.
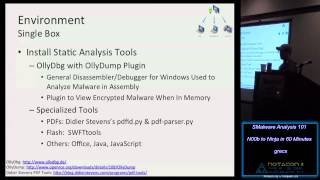
Malware Analysis 101: From Novice to Expert in 60 Minutes
Learn essential malware analysis techniques, from basic to advanced, to enhance your cybersecurity skills and protect against digital threats.
Moving the Industry Forward - The Purple Team Approach
Explore innovative strategies for advancing cybersecurity through the Purple Team approach, blending offensive and defensive tactics to enhance overall security posture.
The Great Trojan Demo - Understanding Remote Access Tools
Explore remote access tools, network security, and live Trojan demonstrations to understand potential threats and defensive strategies for protecting your digital infrastructure.
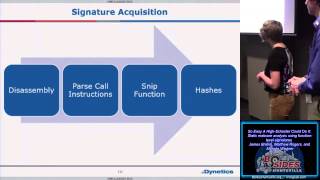
Static Malware Analysis Using Function Level Signatures
Learn static malware analysis techniques using function-level signatures, suitable for high school students and beginners in cybersecurity.
Cyber Security Incidents: Red Team vs Blue Team Tactics
Learn about Red Team/Blue Team cybersecurity exercises, incident response tactics, and best practices for defending against and simulating attacks. Gain insights from real-world scenarios and NIST framework implementation.