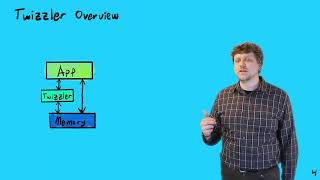
Twizzler - A Data-Centric OS for Non-Volatile Memory
Explore Twizzler, an innovative OS redesign for non-volatile memory, offering efficient data persistence, simplified programming, and improved performance over traditional systems.
The B-MAD Approach to Threat Modeling
Discover the B-MAD approach to threat modeling, exploring its pitfalls and organizational impacts. Learn effective strategies for implementing threat modeling across your organization and improving overall security.
May the Trust be with You - Empowering TrustZone-M with Multiple Trusted Environments
Explore TrustZone-M vulnerabilities and learn about innovative solutions for enhancing security through multiple trusted environments in embedded systems.
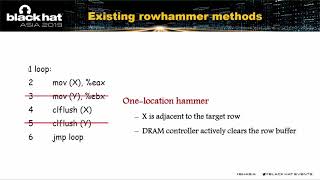
Winter is Coming Back - Defeating the Most Advanced Rowhammer Defenses to Gain Root and Kernel Privileges
A novel exploit breaking advanced rowhammer defenses, allowing unprivileged applications to gain root and kernel privileges. Stealthier and more efficient than existing exploits, this talk presents key steps and implications.
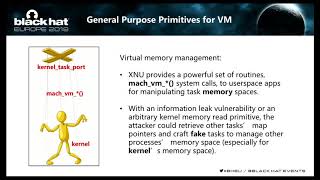
Eternal War in XNU Kernel Objects
Systematic assessment of Apple's kernel security, demonstrating bypasses through ipc_port Kernel Object-Oriented Programming and showcasing realistic attack scenarios for full XNU control.
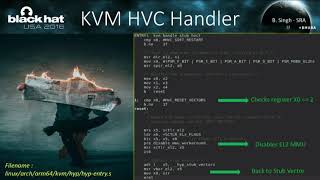
Back to the Future - A Radical Insecure Design of KVM on ARM
Explore ARM architecture vulnerabilities in KVM, focusing on privilege escalation through exception-generating instructions and hypervisor calls. Learn about potential security risks in virtualization.
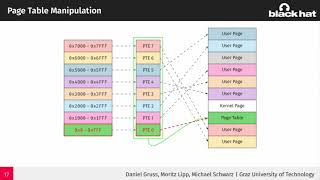
Another Flip in the Row
Explore the Rowhammer bug in DRAM modules, its security implications, exploitation techniques, and potential mitigations in this comprehensive overview of hardware vulnerabilities.
Battle of the SKM and IUM - How Windows 10 Rewrites OS Architecture
Explore Windows 10's revolutionary OS architecture, featuring Virtual Secure Machines, Secure Kernel Mode, and Isolated User Mode. Learn how these changes enhance security and impact system design.
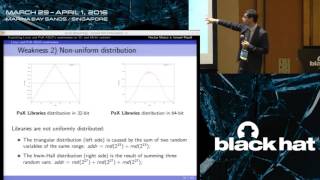
Exploiting Linux and Pax ASLR's Weaknesses on 32-Bit and 64-Bit Systems
Uncover vulnerabilities in Linux and PaX ASLR implementations, exploring low entropy, distribution issues, and object correlations. Learn to bypass Full ASLR and discover ASLR-NG, a new design addressing current weaknesses.
Exploiting Out-of-Order Execution for Covert Cross-VM Communication
Explore a novel side channel attack exploiting CPU out-of-order execution for covert cross-VM communication in cloud environments, with live demos and mitigation techniques.
Over the Edge - Silently Owning Windows 10's Secure Browser
Exploiting Windows 10's memory deduplication feature to silently compromise Microsoft Edge, bypassing security measures and gaining arbitrary memory access through JavaScript-based attacks.
Using Undocumented CPU Behavior to See Into Kernel Mode and Break KASLR in the Process
Explore undocumented CPU behavior to breach kernel security, map memory, and bypass KASLR. Learn techniques for kernel introspection and physical-to-virtual address conversion without special privileges.
Build an End-to-End IoT System Using JavaScript with GDPR Awareness
Explore building a GDPR-compliant IoT system using JavaScript, from device onboarding to remote access. Learn about JerryScript and node.js-based open gateway frameworks for secure, decentralized IoT development.
Teach Me10 Breaking in Bad - I'm the One Who Doesn't Knock
Learn physical security penetration techniques from expert Jayson E. Street. Discover real-world strategies for unauthorized access and improve your organization's defenses.
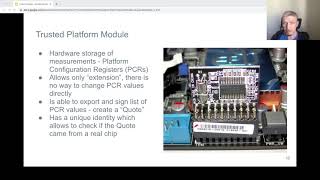
Protecting System Integrity with Trusted Platform Module
Explore system firmware vulnerabilities and learn how Trusted Platform Module (TPM) can safeguard against persistent implants, ensuring secure access to infrastructure secrets.
An SRE Guide to Linux Kernel Upgrades
Demystifying Linux kernel releases: Learn to safely and timely update your systems, balancing security patches with stability concerns for high-profile services and applications.
Cyber Insurance - Technical Challenges and a System Security Roadmap
Explore cyber insurance's growth, challenges, and future directions. Discover how data-driven methodologies and automated tools can enhance risk assessment and management in this evolving field.
Hijacking Transient Execution through Microarchitectural Load Value Injection
Explore microarchitectural vulnerabilities and load value injection techniques to understand transient execution hijacking in modern processors.
Taming Spiky Log Volumes - Maintaining Real-Time Log Accessibility with Kaldb
Explore strategies for managing high-volume log data and maintaining real-time accessibility using Kaldb. Learn techniques to handle spiky log volumes efficiently in large-scale systems.
Hand Me Your Secret, MCU - Microarchitectural Timing Attacks on Microcontrollers Are Practical
Unveiling novel microarchitectural timing side-channel attacks on microcontrollers, challenging the belief that MCUs are immune to such vulnerabilities due to their simple architecture.
Principles for Developing More Secure Systems
Comprehensive guide to system security principles, covering confidentiality, integrity, authentication, correctness, observability, overcapacity, and scalability with detailed examples for various system types.