Uncover, Understand, Own - Regaining Control Over Your AMD CPU
Explore AMD's Platform Security Processor: firmware analysis, functionality insights, and security implications. Learn to extract, replace, and observe PSP components, gaining control over your AMD CPU.
Prisoner Number Six
Explore Docker container escape techniques through live demonstrations, covering reconnaissance, exploiting vulnerabilities, and gaining system access. Learn practical cybersecurity skills for container environments.
IOMMU and DMA Attacks
Exploring IOMMU and DMA attacks, focusing on security implications, operating system integration, and techniques to bypass protections, particularly on macOS up to version 10.12.4.
Ghost DMA Attack & The SeDeFuS Conundrum
Explore Ghost DMA attacks, their mechanisms, and mitigations. Learn about the SeDeFuS conundrum and its implications for system security in this technical presentation.
Intel Management Engine Deep Dive
Explora el Intel Management Engine: arquitectura, firmware, seguridad y desarrollo de un emulador. Análisis profundo de su funcionamiento interno y posibilidades de reemplazo de código abierto.
Plundervolt - Flipping Bits from Software Without Rowhammer
Explore Plundervolt, a software-based fault attack exploiting voltage scaling interfaces in processors to compromise system security, recover cryptographic keys, and induce vulnerabilities in secure enclaves.
Kernel Tracing With EBPF
Explore Linux kernel tracing with eBPF: learn practical uses, dynamic instrumentation techniques, and insights into system workings. Gain knowledge to monitor actions and reveal process secrets efficiently.
Cryptography Pitfalls
Explore common cryptography pitfalls, modern techniques, and tools to enhance system security. Learn about random number generation, hash functions, ciphers, and authentication protocols.
What Do You Mean Threat Model Every Story
Explore integrating threat modeling into continuous development, focusing on methodology, developer education, and reflecting evolving systems in fast-paced environments.

Spectre, Meltdown, & Linux
Explore Meltdown and Spectre security issues, their impact on Linux, and learn how the kernel community addressed these vulnerabilities to ensure system protection.
Kernel Runtime Security Instrumentation
Explore extensible Linux security with eBPF programs, enabling custom security and auditing solutions without kernel modifications. Learn design, interfaces, and practical applications.

Using Seccomp to Limit the Kernel Attack Surface
Explore seccomp for system call filtering in Linux, covering BPF virtual machine basics, filter examples, and applications in sandboxing and security. Learn implementation techniques and considerations.
Open System Firmware Projects
Explore open source system firmware initiatives aimed at enhancing boot, device, and management firmware. Industry experts discuss efforts to improve openness, portability, security, and maintainability.
A Software Approach to Defeating Side Channels in Last-Level Caches
Explore techniques to mitigate side-channel attacks in last-level caches, focusing on Copy-On-Access and Cacheability Management methods for enhanced cloud security.
Securing Linux VM Boot with AMD SEV Measurement
Explore AMD SEV measurement for securing Linux VM boot, covering vulnerabilities, solutions, and future plans in confidential computing environments.
3D Red Pill - A Guest-to-Host Escape on QEMU/KVM Virtio Device
Demonstration of a guest-to-host escape exploit on QEMU/KVM virtio-gpu devices, showcasing vulnerability analysis, exploitation techniques, and potential security solutions.
Plundervolt - Flipping Bits from Software without Rowhammer
Discover Plundervolt: a software-based fault attack that threatens system security without physical access. Learn its mechanisms, potential impacts, and how it compares to Rowhammer.
Exploiting the Hyper-V IDE Emulator to Escape the Virtual Machine
Explore a critical Hyper-V vulnerability, its exploitation on Windows Server 2012R2, and learn about virtualization security, memory manipulation, and payload strategies in this technical deep dive.
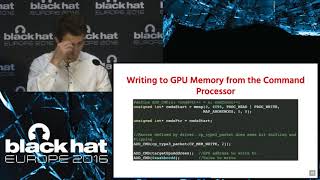
GPU Security Exposed
Explore GPU security vulnerabilities, including shared memory risks and privilege escalation issues, with insights on protecting popular devices from potential exploits.
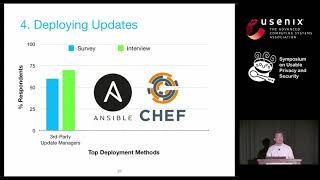
Keepers of the Machines - Examining How System Administrators Manage Software Updates
Examining system administrators' software update management practices, challenges, and potential improvements for multiple machines to enhance organizational cybersecurity.
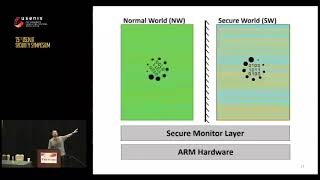
fTPM - A Software-Only Implementation of a TPM Chip
Explore software-based TPM implementation using ARM TrustZone, overcoming hardware limitations to provide robust security features for trusted computing in mobile devices.