What Have Namespaces Done for You Lately? - Writing Containers from Scratch
Explore container creation from scratch using Go, focusing on namespaces and their impact on resource access and system isolation.
A move_pages() Equivalent for Physical Memory
Proposal for a syscall to migrate physical memory contents between NUMA nodes, exploring integration with mm/migrate.c and potential applications in tiering frameworks.
Securing Containers - One Patch at a Time
Explore CVE-2016-9962: discovery, implications, and resolution. Dive into kernel boundaries, system calls, and address space randomization for enhanced container security.
The New Shiny System Call in the Block
Explore the latest system call innovation with Uber engineer Abhijit Singh, delving into its functionality, implementation, and potential impact on Linux kernel development.
Implementing BPF_PROG_LOAD_FD
Explore the implementation of BPF_PROG_LOAD_FD with Neill Kapron, gaining insights into this crucial aspect of Linux kernel programming and eBPF technology.
Mount API Extensions
Explore mount API extensions with Christian Brauner, delving into advanced Linux system concepts and their practical applications.
Fast Uprobes - Enhancing Linux Kernel Tracing
Explore fast uprobes with Jiri Olsa, learning about their implementation, performance benefits, and practical applications in Linux kernel tracing.
Tracing the Source of Errors
Discover effective techniques for identifying and tracing error sources in Linux systems, enhancing debugging skills and improving system reliability.
Hooking Libc Calls to Debug Kubernetes Apps - When They Go High, We Go Low
Explore innovative debugging techniques for Kubernetes apps using low-level Rust code to hook libc calls, enabling local testing and debugging in cloud conditions.
Debugging with Strace - A Peek Behind the Scenes of Linux Processes
Unravel the mysteries of strace, a powerful Linux debugging tool. Learn system calls, analyze output, and enhance your skills with real-life examples to become a more proficient Linux developer.
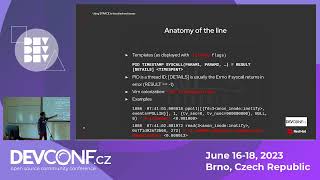
Using STRACE to Troubleshoot Userspace Issues - DevConf.CZ 2023
Explore strace basics and advanced techniques for troubleshooting userspace issues, with practical examples from Red Hat's support team.
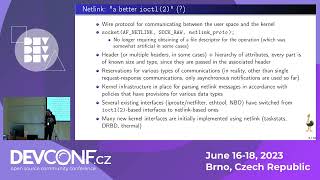
Current State of Netlink Decoding in Strace
Explore strace's netlink decoding capabilities, implementation, and challenges in protocol design and decoding for Linux system call tracing.
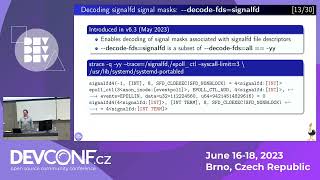
Modern strace - New Features and Problem-Solving Capabilities - DevConf.CZ 2023
Explore advanced features of strace for Linux debugging, including seccomp-assisted filtering, syscall tampering, and PID namespace translation.
Seitan: A Plant-Based Recipe Against Syscall Anxiety
Explore a unified approach to privilege separation in containers and VMs using Seitan. Learn to write JSON recipes for filtered system calls and enhance security for untrusted workloads.
Update on Landlock: IOCTL Support
Explore Landlock security module's features, recent developments, and new IOCTL restriction support for enhanced Linux process sandboxing and security policies.
Catching Linux Post-Exploitation with Auditd
Learn to detect Linux post-exploitation using Auditd. Explore system calls, audit rules, and attack scenarios for enhanced security monitoring and threat detection.
Ekoparty #UniTalks Córdoba 2021 - Analizando programas dinámicamente a través de sus syscalls
Análisis dinámico de programas mediante syscalls para detectar malware. Nueva herramienta desarrollada en proyecto de investigación de UTN, presentada por experto en seguridad informática Germán Parisi.
Anatomie eines containerfähigen Linux-Kernel-Rootkits
Einblick in die Implementierung eines containerfähigen Linux-Kernel-Rootkits. Erläutert Rootkits, Container-Technologien und zeigt detailliert die Programmierung eines solchen Rootkits mit Backdoor-Funktionen und Ausbruchsmöglichkeiten.
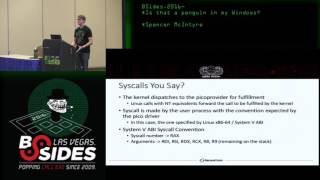
Is That a Penguin in My Windows?
Explore Windows Subsystem for Linux: architecture, processes, system calls, and security implications. Learn about cross-process access and Linux-Windows interactions.
Emulating Packed Linux Malware Using the Unicorn Emulator Framework - DefCamp - 2019
Explore Linux malware packing, unpacking techniques, and emulation using Unicorn framework. Learn practical skills for malware analysis and reverse engineering in this hands-on cybersecurity talk.
The End of Time, 19 Years to Go
Explore the 2038 time_t overflow issue in Linux, its impact on various systems, and ongoing efforts to address it. Learn about kernel updates, remaining challenges, and future steps for user space solutions.