
State of the Onion - Security Onion 2017
Comprehensive overview of Security Onion's latest developments, features, and future roadmap, presented by Doug Burks at the 2017 conference. Gain insights into this powerful network security monitoring platform.
Beyond Windows Forensics With Built-in Microsoft Tooling
Explore advanced Windows forensics techniques using native Microsoft tools for enhanced digital investigation and threat detection capabilities.
Exploiting Group Policy Objects for Persistence and Lateral Movement
Explore how Group Policy Objects can be exploited for malware distribution and network persistence. Learn about PowershellEmpire modules and countermeasures for enhanced cybersecurity in enterprise environments.
Google Workspace Forensics - Insights from Real-World Hunts and Incident Response
Insights on threat hunting and incident response in Google Workspace, focusing on data exfiltration from Google Drive. Learn forensic investigation techniques for GWS logs from real-world cases.
Hyper-scale Detection and Response - Cost-Effective SIEM Alternatives
Discover cost-effective, open-source solutions for hyper-scale threat detection, processing 45TB+ logs daily. Learn to enhance security monitoring without expensive SIEM platforms.
Mender - Current and Future Status of Open Source OTA Updates for Embedded Systems
Explore Mender's open-source project for OTA updates to embedded systems. Learn about challenges, solutions, and future developments in this informative session.
Forwarding Snort Logs to Splunk
Learn to forward Snort logs to Splunk for powerful data analysis and monitoring. Explore Splunk's web interface to search, analyze, and visualize machine-generated data, enhancing your cybersecurity capabilities.
SUDO Security Policy Bypass Vulnerability - CVE-2019-14287
Explanation and demonstration of the sudo security policy bypass vulnerability (CVE-2019-14287), including how it works and can be exploited. Includes practical examples and technical details for cybersecurity professionals.
Installing and Configuring Wazuh for SIEM - Blue Team Operations
Learn to set up Wazuh SIEM for detecting intrusions, attacks, and malicious activity. Covers installation and agent configuration on Windows and Linux for effective security data management.

CrowdStrike IT Outage Explained - Kernel Mode Driver Analysis
Detailed analysis of CrowdStrike's IT outage from a Windows developer's perspective, focusing on kernel mode drivers and system vulnerabilities.
Network File System Security - Exploiting Misconceptions and Vulnerabilities
Explore Network File System security misconceptions and exploitation techniques. Gain insights into NFS protocol vulnerabilities and learn how to address common security pitfalls in enterprise environments.
The SaaS-y Side of Incident Response - Key Log Sources for Okta, GitHub, and Salesforce
Explore key log sources for Okta, GitHub, and Salesforce in cloud-based incident response. Learn to interpret SaaS logs, avoid common pitfalls, and improve detection strategies for effective security management.
Netbird - Open Source Self-Hosted Wireguard VPN System Setup and Configuration
Learn to set up Netbird, an open-source Wireguard VPN system, with server GUI and easy client setup. Covers installation, configuration, and user management for secure, self-hosted networking.
Security Onion Essentials 2024 - Detection Engineering
Explore detection engineering in Security Onion 2.4.70, covering key techniques and best practices for enhancing network security and threat detection capabilities.
Getting to Know Spectre and Meltdown Checker
Explore the Spectre & Meltdown Checker tool, its implementation, design flows, and capabilities for assessing CPU vulnerabilities and enhancing system security.
LUNAR: A Native Table Engine for Embedded Devices
Explore LUNAR, a novel native table storage engine for embedded devices, optimizing bandwidth utilization and resource consumption while providing SQL-compatible APIs and modular architecture.
Detecting Credential Abuse - Core Concepts and Challenges
Explore detection strategies for credential abuse, including core concepts, patterns, and challenges. Learn to identify suspicious activity and protect systems from unauthorized access.
LLMs at the Core - From Attention to Action in Scaling Security Teams
Explore practical tools leveraging LLMs to scale security teams, streamline workflows, and enhance decision-making in complex environments. Gain insights on automating tasks and improving security processes.
War Stories from the SOC - Cybersecurity Incident Response Lessons
Cybersecurity expert shares real-world experiences from Security Operations Center, offering insights into threat detection, incident response, and best practices for defending against cyber attacks.
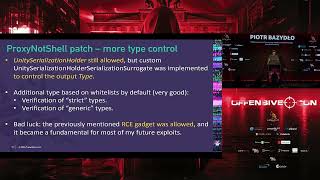
Half Measures and Full Compromise: Exploiting Microsoft Exchange PowerShell Remoting
Explore Microsoft Exchange PowerShell Remoting vulnerabilities and exploitation techniques for enhanced cybersecurity awareness and defense strategies.
Mailwizz Setup and Installation - How to Host and Install Mailwizz on Your Own Server
Comprehensive guide to hosting and installing Mailwizz PHP script on a VPS server, covering server setup, domain configuration, installation process, and essential optimizations.