Practical Approach to Automate the Discovery and Eradication of Open-Source Software Vulnerabilities
Discover and eradicate open-source vulnerabilities in web applications at scale. Learn Netflix's pragmatic approach to identifying risks, triaging vulnerabilities, and implementing effective remediation strategies.
Building Secure and Reliable Systems at Scale
Learn Google's best practices for building secure, reliable systems at scale through automated security, containment, and multi-party techniques that foster a culture of review and resilience.
I Boot when U-Boot
Explore a custom bootkit for U-Boot devices, its persistence techniques, and implications for IoT security. Learn about backdooring methods and potential countermeasures.
What Was Once Old Is New Again - Domain Squatting in 2020
Modernized domain squatting techniques for OSINT gathering and weaponized document delivery, exploring corporate relationships, supply chain mapping, and advanced spear-phishing attacks.
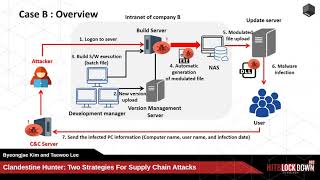
Two Strategies for Supply Chain Attacks
Explore two supply chain attack strategies by BARIUM APT group, analyzing real-world cases and their tactics. Learn defensive measures against these sophisticated cyber threats.
TOCTOU Attacks Against Secure Boot and BootGuard
Explore TOCTOU attacks on Intel's BootGuard, learn about vulnerabilities in secure boot processes, and discover open-source tools for testing system security.
The Evolving Attack Surface
Explore the expanding vulnerabilities in industrial control systems, from traditional security to blockchain, with insights on hardware attacks, supply chain risks, and network hijacking.
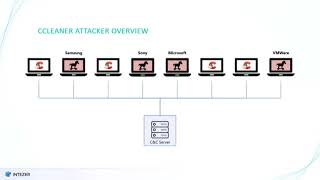
Supply Chain Attack Through CCleaner - Evidence Aurora Operation Still Active
Análisis detallado del ataque de cadena de suministro a CCleaner, explorando su sofisticación, objetivos y conexiones con el grupo APT17/Axiom, destacando la persistente amenaza de ataques estatales avanzados.
We Are About to Land - How CloudDragon Turns a Nightmare Into Reality
Explore CloudDragon's advanced cyber tactics, including supply chain and cross-platform attacks. Gain insights into APT group operations and their evolving techniques in this cybersecurity analysis.
On-Chip Randomization for Memory Protection Against Hardware Supply Chain Attacks to DRAM
Explore innovative techniques for safeguarding DRAM against hardware supply chain attacks through on-chip randomization, enhancing memory protection in modern computing systems.
Mac-ing Sense of the 3CX Supply Chain Attack - Analysis of the macOS Payloads
Detailed analysis of the 3CX supply chain attack's macOS payloads, exploring the first "chained" supply chain attack and its impact on macOS systems. Insights into advanced cybersecurity threats and defenses.
Secure Software Supply Chains for Python
Explore Python software supply chain security, including common attacks, protective measures, and tools. Learn about ecosystem improvements for enhanced security in third-party package integration.
Why You Should Care About Open Source Supply Chain Security
Explore open source supply chain security, understanding vulnerabilities, attack vectors, and protective measures. Learn to evaluate dependencies and implement safeguards against potential threats.
Project Trebuchet - How SolarWinds is Using Open Source to Secure Their Supply Chain in the Wake of the Sunburst Hack
SolarWinds' Project Trebuchet: Rebuilding secure software supply chain using CNCF and CDF projects after Sunburst hack. Insights on new build system, its necessity, and lessons learned from a major security breach.
Defending JavaScript Projects from Supply Chain Attacks - Running Code from the Internet Safely
Explore proactive defenses against JavaScript supply chain attacks, including access control and future JS features for enhanced project security.
Securing the Unseen: Defending Against Open Source Software Supply Chain Attacks
Discover practical strategies to protect applications from supply chain attacks targeting open source dependencies, with real examples and actionable defense measures.
Gem Install: What Could Go Wrong? - Risks and Prevention in Ruby Dependencies
Explore potential risks of installing gems and learn strategies to safeguard your Rails application's dependencies against attacks.
Securing Gradle Builds: Protecting Against Supply Chain Attacks
Secure Gradle builds against supply chain attacks with insights on vulnerabilities, protection strategies, and best practices for dependency and metadata verification.
Insights into New Supply Chain and Cloud-Identity Attacks
Explore new cloud threat tactics exploiting supply chain and identity vulnerabilities, with live demonstrations and defense strategies against adversaries like PANDA.
The Simple Yet Lethal Anatomy of an AI Attack
Dive into the anatomy of AI security threats through live demonstrations, exploring attack strategies from reconnaissance to LLM poisoning, and learn to defend against emerging vulnerabilities in AI systems.
The XZ Backdoor Story: How a Supply Chain Attack Nearly Compromised SSH Servers
Uncover the gripping investigation of the XZ backdoor incident, exploring the mysterious maintainer Jia Tan, technical analysis of the compromise, and crucial lessons for open-source security.