The Critical Path to Implant Backdoors and Potential Mitigation Techniques: Learnings from XZ Utils
Analyze the critical attack path of XZ Utils backdoor and explore mitigation strategies for supply-chain attacks in open-source software.
Intersection of AI and Security - Traditional Sessions
Explore AI security challenges and solutions: CISO checklist, LLM security framework, and machine learning model serialization attacks. Gain insights from experts on safeguarding AI systems.
XZ Backdoor - Navigating the Complexities of Supply Chain Attacks Detected by Accident
Explore the intricacies of supply chain attacks through the lens of the XZ Backdoor incident, uncovering detection methods and implications for cybersecurity professionals.
Detection Engineering Demystified - Building Custom Detections for GitHub Enterprise
Learn to build custom detections for GitHub Enterprise, focusing on identifying attacker behavior and protecting intellectual property through practical Detection Engineering techniques.
Securing Cloud-Native DevOps - A Zero Trust Approach
Explore Zero Trust principles for securing cloud-native DevOps environments, addressing challenges like supply chain attacks and lateral movement in microservices and serverless architectures.
Securing the Software Supply Chain: Challenges and Solutions
Learn strategies to secure the software supply chain against attacks, prioritize security measures, and protect your organization from catastrophic data breaches.
This Is How They Tell Me the World Ends - The Cyber Weapons Arms Race
Explore the global cyber arms race and its societal impact with cybersecurity expert Nicole Perlroth. Gain insights into cyber warfare, supply chain attacks, and strategies for addressing cybersecurity challenges.
Supply Chain Attacks - Focusing on NPM Vulnerabilities and Defenses
Explore NPM ecosystem vulnerabilities, learn to identify and protect against supply chain attacks, and discover strategies to fortify open-source software security.
Exploring a Risk Approach to Software Supply Chain Security
Explore software supply chain security through a risk-based approach, focusing on open source vulnerabilities and process improvements to mitigate supplier risks.
Adding Security for Reliable Continuous Delivery
Enhance security in continuous delivery: Learn containerization challenges, vulnerabilities, misconfigurations, supply chain attacks, and IAM. Explore solutions and see a practical demo.
Supply Chain Attacks: Focusing on NPM Vulnerabilities - DevSecOps 2023
Explore supply chain attacks focusing on NPM, learn defensive strategies, and discover research findings on vulnerabilities in package ecosystems. Gain insights into detection tools and solutions.
4 CI Security Best Practices to Prevent Cloud-Native Supply Chain Attacks
Explore security challenges in CI pipelines and learn best practices to prevent cloud-native supply chain attacks. Discover tips for securing GitHub Actions, GitLab Runner, and CircleCI workflows.
Exploitation Techniques and Attacks on Hosting Assets and Access for Resale
Exploration of underground markets for compromised network assets, covering exploitation techniques, lateral movement, monetization, and defender strategies for incident response and security monitoring.
Surprise Supplies
Exploring major supply chain attacks of 2017, including MeDoc and CCleaner compromises. Analyzes attacker methods, malware used, and impact on victims. Discusses the history and future of supply chain attacks.
Samsara Metamorphic Engine
Explore Samsara, a viral metamorphic engine for JVM that transforms compiled targets, complicating analysis and enabling supply chain attacks from within IDEs, with added anti-debugging features.
1-Click to Infiltrate Your Organization via Vulnerable VS Code Extensions
Explore vulnerabilities in popular VS Code extensions and their potential for supply chain attacks. Learn how attackers can compromise organizations through developers' IDEs.
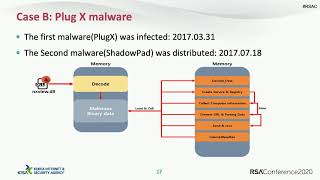
Chronicle of the Supply Chain Attack and Two Attack Strategies
Explore supply chain attack strategies, including software development environment and update server penetration, through analysis of incidents targeting Korean and global companies.
IIoT, Data Infrastructure, Smart Factory - Sarka Pekarova - Ekoparty 2021: OT - IIOT - IOT Space
Explore industrial cybersecurity challenges in IIoT and smart factories. Learn about automation pyramids, network segmentation, and threat landscapes to enhance IT-OT security in Industry 4.0 environments.

Reverse Engineering and Exploiting Builds in the Cloud
Explore security vulnerabilities in cloud-based CI/CD and container build environments. Learn about potential attack scenarios, remediation strategies, and best practices for securing the software supply chain.
Mitigating Russian State-Sponsored Cyber Threats to US Critical Infrastructure
Explore Russian state-sponsored cyber threats to US critical infrastructure, learn mitigation strategies, and understand FBI resources for enhancing cybersecurity preparedness.
The Enemy Within - Modern Supply Chain Attacks
Practical guidance on defending against and responding to supply chain attacks, covering prevention strategies, risk assessment, and best practices for both SecOps and App Development professionals.