SQLViking - Pillaging Your Data
Explore SQLViking, a tool for passive SQL query logging and active TCP injection attacks on databases. Learn about network security vulnerabilities and potential countermeasures.
Mantra OS - Penetration Testing Tools and Methodologies
Explore Mantra OS's penetration testing tools for web application security, including DDoS, SQL injection, and man-in-the-middle attacks. Learn practical methodologies and controlled environment testing techniques.
Blended Web and Database Attacks on Real-time, In-Memory Platforms
Explore blended web and database attacks on real-time, in-memory platforms, focusing on SAP HANA. Learn about novel exploit techniques, vulnerabilities, and security considerations for these high-performance systems.
Libinjection: From SQLi to XSS Detection - New Algorithm Introduction
Explore advanced techniques for detecting SQLi and XSS attacks using libinjection, a fast and accurate algorithm. Learn about its implementation, benefits, and future developments in web security.
Hacking for Developers
Learn ethical hacking techniques, tools, and methodologies to enhance your development skills and improve software security. Gain insights into vulnerability assessment and exploitation.
Injecting Brains Into Blind SQL Injection - Optimizing Data Exfiltration
Innovative approach to optimize Blind SQL Injection using Machine Learning and statistics. Introduces Hakuin, a tool that significantly improves exfiltration speed for database schemas and content compared to standard methods.

Hacking Web Applications
Comprehensive guide to web application vulnerabilities, covering OWASP Top 10, hands-on walkthroughs, and defense strategies. Learn to identify, exploit, and mitigate common security risks in web applications.
Blind SQL Injection Made Easy
Learn hands-on techniques for exploiting blind SQL injection vulnerabilities with a practical lab demonstration and expert guidance on this critical web security issue.
OWASP Juice Shop - SQL Injection
Learn to perform SQL injection on OWASP Juice Shop in this hands-on demonstration. Gain practical skills in identifying and exploiting web application vulnerabilities to enhance your cybersecurity knowledge.
Web Application Security: The Secret to Hack-Proof Apps - SQL Injection - Part 2
Discover step-by-step methods to secure web applications from SQL injection threats. Learn to identify vulnerabilities, exploit techniques, and implement effective prevention strategies for robust security.
Code Red: Navigating the Minefield of Security Programming Blunders
Explore infamous security breaches, learn from programming mishaps, and gain practical strategies to enhance cybersecurity in this dynamic session on secure coding practices.
SQL Injection 101 - Pentesting Diaries
Explore SQL injection techniques and tools in this weekly pentesting series. Learn attack methods, tool usage, and optimization for deeper understanding and improved efficiency.

SQL Injection Explained - With Free Labs
Comprehensive guide to SQL injection vulnerabilities, featuring expert insights and hands-on practice labs for enhancing web security skills and bug bounty hunting techniques.
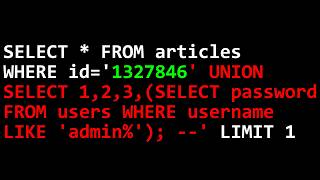
Interactive SQL Injection
Hands-on practice with SQL injection techniques in a safe environment. Learn to identify and exploit vulnerabilities, enhancing your cybersecurity skills and understanding of database security.
SQL Injection Explained - Understanding Attacks and Prevention
Comprehensive guide to SQL injection attacks: types, vulnerabilities, and prevention techniques. Learn to identify, exploit, and protect against database security threats through practical examples and best practices.
The Ultimate 2024 Cybersecurity Tutorial - From Fundamentals to Advanced Concepts
Master cybersecurity fundamentals, from threats and frameworks to tools and AI applications. Gain practical skills for data protection, forensics, and career growth in this comprehensive tutorial.
Zero Trust APIs with Python
Explore Zero Trust Security for APIs using Python. Learn to identify and address vulnerabilities, implement robust data validation, and use tools for automated security testing.
When Not to Use a Web Application Firewall and Its Alternatives - Lecture
Explore when to avoid Web Application Firewalls (WAFs) and learn their limitations. Understand WAF architecture, common web threats, and alternative security approaches for effective application protection.
Building an LLM Vulnerability Scanner to Secure AI Applications
Develop an LLM vulnerability scanner to audit and secure AI applications. Learn about LLM security risks and build a CLI tool for detecting vulnerabilities in AI systems.
The Case for Runtime Protection
Runtime protection: inoculating apps against vulnerabilities without changing code. Explores how instrumentation hardens applications, making OWASP Top Ten harder to exploit. Discusses accuracy, performance, and impact on security culture.
Advanced Android Studio Hacking - Part 2
Explore Android device hacking using Android Studio. Learn emulation, user agent tracking, reverse engineering, API tokens, decompilation, and SQL injection techniques.