AppSec Behaviors for DevOps Breed Security Culture Change
Learn effective AppSec behaviors to foster a security-conscious DevOps culture. Discover practical strategies for integrating security, conducting code reviews, and responding to vulnerabilities.
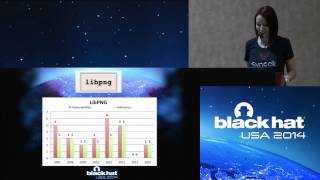
Epidemiology of Software Vulnerabilities - A Study of Attack Surface Spread
Explore the impact of third-party libraries on software vulnerabilities, analyzing their spread across products and discussing strategies to mitigate risks in application development.
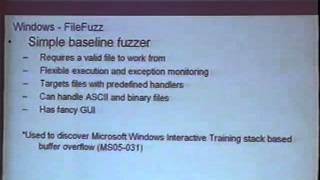
The Art of File Format Fuzzing
Explore advanced techniques for file format fuzzing, uncovering vulnerabilities in software applications through systematic input manipulation and analysis.
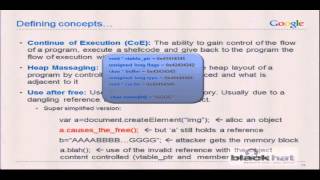
The Info Leak Era on Software Exploitation
Explore advanced techniques for exploiting software vulnerabilities through information leaks, focusing on defeating ASLR and converting various vulnerabilities into effective info leaks.
Java Every-Days - Exploiting Software Running on 3 Billion Devices
Explore Java vulnerabilities, exploitation trends, and security measures in this Black Hat talk. Gain insights into common weaknesses, attack surfaces, and Oracle's responses to protect 3 billion devices.
Windows 2003 - Java Library Hole Allowing Multiplatform Denial-Of-Service
Explore a critical Java library vulnerability enabling multiplatform denial-of-service attacks on Windows 2003 systems, presented by security expert Marc Schöenefeld.
ODDFuzz - Hunting Java Deserialization Gadget Chains via Structure-Aware Directed Greybox Fuzzing
Innovative approach to efficiently detect Java deserialization vulnerabilities using structure-aware directed greybox fuzzing, addressing challenges in existing tools and improving precision in gadget chain hunting.
Offensive Countermeasures - Still Trying to Bring Sexy Back
Explore offensive countermeasures in cybersecurity, including social engineering, password vulnerabilities, and innovative techniques to deter and confuse attackers while enhancing network defense.
Win32 Exploit Development With Mona and Metasploit
Learn advanced Win32 exploit development techniques using Mona and Metasploit, covering vulnerability exploitation, debugging plugins, and protection bypass methods.
Classic Vulnerabilities
Explore classic software vulnerabilities, their recent resurgence, and modern tools for detection and prevention. Learn from history to enhance security in today's development practices.
Improving the Security of Your Code with Free Analysis Tools
Explore free static and dynamic analysis tools to enhance code security. Learn when and how to use these tools in development to reduce vulnerabilities and produce more secure software.
Talking Business About Security
Insights on communicating security risks to executives, covering brand damage, corporate espionage, and effective presentation strategies for CISOs and security leaders.
How to Do In-App Chaos Testing
Explore in-app chaos testing techniques to uncover and address potential system failures, enhancing software resilience without modifying the codebase.
Medical Device Security and Cybersecurity Risks - Enigma 2016
Exploring cybersecurity risks in medical devices, this talk covers regulatory issues, international standards, and the balance between innovation and patient safety in software-dependent healthcare technology.
Why Even Experienced and Highly Intelligent Developers Introduce API Vulnerabilities
Explores why experienced developers introduce vulnerabilities through API misuse, examining cognitive factors and personality traits affecting code security detection abilities.
Exposing Hidden Exploitable Behaviors in Programming Languages Using Differential Fuzzing
Uncover hidden vulnerabilities in programming languages through differential fuzzing. Learn to identify undocumented functions, exposed sensitive data, unexpected code execution, and potential security risks.
Mining Software Vulnerabilities in SCCM / NIST's NVD - The Rocky Road to Data Nirvana
Explore software vulnerability mining in SCCM and NIST's NVD, uncovering challenges and insights in the journey towards comprehensive data analysis and improved cybersecurity practices.
Ensuring Cloud Resource Health: Addressing Software Vulnerabilities and Identity Risk
Learn to address software vulnerabilities and identity risks in cloud environments using Security Command Center's new capabilities for strengthening overall risk posture.
Matching CVEs and Source Code for Vulnerability Detection
Explore techniques for mapping CVEs to source code, including parsing CVE data and quantifying correspondence statistics. Learn about open-source tools and potential AI applications for vulnerability detection.
Bridging the Gap for Security Analysis in Infer
Explore advancements in Infer's static analysis for enhanced security vulnerability detection, with proposed improvements and implementation strategies for expanded property coverage.
A Glimpse Into Open Source Software Vulnerability Disclosure Practices
Explore current challenges and solutions in open-source software vulnerability disclosure, examining security advisories, bug bounty reports, and maintainer perspectives for improved OSS security practices.