The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
Unveiling the Underground World of Anti-Cheats
Explore the ongoing battle between cheat developers and anti-cheat technologies in gaming. Learn about bypassing techniques and tools for testing anti-cheat software effectiveness.
Vectorized Emulation - Putting It All Together
Explore vectorized emulation's potential in fuzzing, leveraging AVX-512 for parallel VM execution, enhanced code coverage, and hardware-accelerated taint tracking for improved vulnerability detection.
Taking the Guess Out of Glitching
Explore fault injection techniques in hardware hacking with practical tips on timing, intensity, and effectiveness. Learn innovative methods to determine optimal glitch timing for successful attacks.
Automotive Security Bugs Explained for Bug Hunters
Explore common automotive security vulnerabilities and learn bug hunting techniques for car systems, from IoT security to CAN bus hacking. Gain insights into PoCs, attacks, and bug prioritization in the automotive industry.
PwdLess - Exploitation Tales from RouterLand
Explore IoT device security through an attacker's perspective, covering fuzzing, reverse engineering, and exploit development. Learn about vulnerabilities, remote execution techniques, and challenges in IoT security.
Building Hardened IoT Implementations With LangSec
Explore Language-theoretic security for IoT, focusing on input recognition and processing separation. Learn about parser combinators, test case generation, and implementation in AMQP protocol for robust IoT systems.
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.
Automating Security Testing with Functional Testing Test Cases
Learn to automate security testing by integrating it with functional test cases, enhancing efficiency and coverage in software development processes.
Diversity in Bug Hunting
Panel discussion featuring women leaders in tech exploring strategies to increase diversity in bug hunting and cybersecurity, sharing insights and experiences from their roles at major tech companies.
Fuzzware - Automating & Scaling Fuzzing For Firmware
Automated firmware testing using Fuzzware: emulate and fuzz embedded systems without hardware. Discover vulnerabilities in network stacks and scale security analysis for diverse devices.
Nearly Generic Fuzzing of XML Based Formats
Explore advanced XML fuzzing techniques and a new tool for mutating XML documents, with insights from an experienced penetration tester on finding security vulnerabilities in various formats.
Pentesting Without Pentesters
Innovative scanning technology enables functional test cases to produce security findings, bridging the gap between development and security testing without dedicated pentesters.
Bug Hunter Adventures
Discover reconnaissance techniques and tools for finding vulnerabilities in Google's Vulnerability Reward Program. Learn from experienced bug hunters' journeys and insights into this coveted program.
Scale Hacking to Secure Your Cloud and Beyond
Learn tips and tricks for scaling bug hunting in cloud environments, enhancing your cybersecurity skills and improving your ability to find vulnerabilities efficiently.
Static Analysis-Based Recovery of Service Function Calls in UEFI Firmware
Discover a new tool for automated recovery of service calls and EFI type info in UEFI firmware, simplifying vulnerability hunting and making firmware code resemble original source.
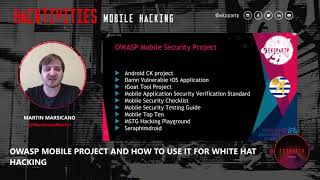
Mobile Hacking - OWASP Mobile Project and How to Use It for White Hat Hacking
Explora los proyectos OWASP para seguridad móvil: MASVS para verificación y MSTG para pruebas e ingeniería inversa. Aprende a evaluar y mejorar la seguridad de aplicaciones iOS y Android.
Don't Trust the NIC - Attacking Windows NDIS Drivers
Exploración de vulnerabilidades en controladores NDIS de Windows, demostrando ataques y problemas de seguridad en implementaciones de proveedores, incluyendo Microsoft.
Making Android's Bootable Recovery Work For You
Explore Android's bootable recovery mode to create custom tools for security testing, forensics, and device modification. Learn to build and customize recovery images for various Android devices.
Fuzzing - Finding Your Own Bugs and 0days
Aprende técnicas de fuzzing para descubrir vulnerabilidades y exploits de día cero. Incluye demostraciones prácticas de Buffer Overflow y creación de shellcode para pruebas de penetración.
Historias de vulnerabilidades de un Bug Hunter
Descubre vulnerabilidades web comunes desde la perspectiva de un experimentado bug hunter. Aprende técnicas útiles para pentesting y mejora tus habilidades en seguridad informática.