Fuzzing with AFL
Explore fuzzing with AFL, covering traditional methods, monitoring execution, and applications in Google and Windows. Learn about limitations, instrumented fuzzing, and open problems in this field.
Morning Keynote
Explore cybersecurity challenges in healthcare, including patching complexities, system dependencies, and the need for sustainable solutions in an evolving threat landscape.
Better Manual Web Application Testing Through Automation
Learn techniques to enhance manual web app testing with automation, improving efficiency and effectiveness in identifying vulnerabilities and security issues.
Kali Linux Johnny Long
Explore advanced hacking techniques and tools with renowned security expert Johnny Long, focusing on the powerful Kali Linux distribution for penetration testing and ethical hacking.
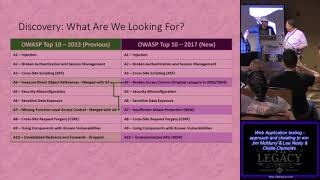
Web Application Testing Approach and Cheating to Win
Learn effective web application testing techniques and strategies to uncover vulnerabilities, including unconventional methods for successful penetration testing.
Automating Security Testing with the OWTF
Learn to automate security testing using OWTF, enhancing efficiency and effectiveness in identifying vulnerabilities and strengthening web application defenses.
How to Conduct a Product Security Test and How it Fits Into the Larger Security Strategy
Learn how to conduct thorough product security tests, from initial investigation to reporting, using various tools and techniques for static and dynamic analysis, fuzzing, and ethical hacking.
Abuse Case Testing in DevOps
Explore abuse case testing in DevOps, covering threat modeling, test development, and integration. Learn to enhance application security through continuous improvement and monitoring.
InSpec Compliance as Code
Explore InSpec for compliance-as-code, learning how to automate security and compliance testing in infrastructure and applications.
Fuzz Your Smartphone from 4G Base Station Side
Explore smartphone vulnerabilities through 4G base station fuzzing techniques, enhancing mobile security knowledge and practical skills.
Synfuzz - Building a Grammar Based Retargetable Test Generation Framework
Explore a grammar-based, retargetable test generation framework for efficient and comprehensive software testing, enhancing security and reliability.
Hacking Mobile Applications with Frida
Learn to hack mobile apps using Frida, a dynamic instrumentation toolkit. Explore techniques for analyzing and modifying app behavior in real-time on iOS and Android platforms.
Web App Testing Classroom in a Box - The Good, the Bad, and the Ugly
Explore web app testing strategies, from ideal scenarios to real-world challenges. Learn effective techniques for red and blue teams, ethical hacking, and auditing.
Its Malware Time - A Bar Crawl from Skunked Homebrew to Rotten Apples
Explore the evolution of malware through real-world examples, from initial infection to advanced techniques. Learn detection and prevention strategies for various attack vectors.
Could Static Code Analysis and Secure Coding Have Saved the Death Star
Explore how static code analysis and secure coding practices could have prevented the Death Star's destruction, using Star Wars as a fun analogy for cybersecurity principles.
Automating Windows Kernel Analysis With Symbolic Execution
Explore automated Windows kernel analysis using symbolic execution techniques for enhanced security and vulnerability detection.
Using Next Generation Fuzzing Tools - Fixing Bugs and Writing Memory Corruption Exploits
Explore next-gen fuzzing tools for bug fixing and memory corruption exploits. Learn about product security assessment, constraint solvers, and web scanning techniques.
Inter-Chip Communication - Testing End to End Security on IoT
Explore IoT security testing with a focus on inter-chip communication, using a smart lock as a case study. Learn practical techniques for analyzing and securing IoT devices.
Metasploit Town Hall - Redubbed
Explore the latest developments and community insights in Metasploit, the popular penetration testing framework, during this informative town hall session from DerbyCon 9.0.
Symbolically Executing a Fuzzy Tyrant
Explore symbolic execution and fuzzing techniques for software security analysis, focusing on practical applications and advanced methodologies.
Lessons Learned Implementing SDLC and How To Do It Better
Insights on implementing SDLC effectively, covering management buy-in, security awareness, threat modeling, code review, and testing for better software development practices.