Navigating the Quantum Readiness Journey: Open-Source Cryptography, PKI and Signing Tools
Explore quantum-resistant cryptography for IoT, containers, and software supply chains using open-source tools. Gain hands-on insights into FIPS-certified APIs, PKI software, and signing solutions for enhanced cybersecurity.

Securing Development Environments with Google Cloud
Adopt Zero Trust security for development teams using Cloud Workstations, BeyondCorp Enterprise, and Assured Open Source Software, enhancing software supply chain security without compromising productivity.
Secure Your Software Supply Chain with Go
Learn to detect and remediate vulnerabilities in Go dependencies using the new vulnerability management system, enhancing software supply chain security.
SBOM: The Inescapable Way of Tracking Dependencies
Explore SBOM's role in preventing cyber-attacks, its formats, and implementation across the software development lifecycle. Learn to generate, manage, and monitor SBOMs for enhanced security.
Protecting Kubernetes Resource Manifests in End-to-End Software Development Lifecycle
Secure Kubernetes manifests throughout the software development lifecycle. Learn about integrity protection, signing techniques, and end-to-end supply chain security.
Better Build Pipelines with OpenSSF Projects - Enhancing Trust and Security
Enhance build pipeline security using OpenSSF projects: cosign, SBOMs, and SLSA. Demonstrate kpack for container image building on Kubernetes, integrating signed images and SBOM generation.
Securing Open Source Supply Chains: Challenges and Solutions
Explore the importance of securing open source supply chains through automation, best practices, education, and collaboration in data centers and consumer applications.
Securing Your .NET Application Software Supply-Chain
Hands-on guide to securing .NET application supply chains, covering source code access, third-party libraries, build servers, and implementing SLSA guidance and SBOM concepts to mitigate security risks.
Abusing GitHub for Fun and Profit - Actions and Codespaces Security
Explore security vulnerabilities in GitHub Actions and Codespaces, including real-world exploitation scenarios and practical tips for protecting your software supply chain and development pipelines.
An Acronym-Free Introduction to Software Supply Chain Security
Explore principles and practices for securing software supply chains without jargon. Learn about open-source projects, standards, and common terms to enhance your understanding of this rapidly evolving field.
Protecting the World's Greatest Open Source Ecosystem with Sigstore
Explore Sigstore, an OpenSSF project enhancing software supply chain security. Learn to sign and verify Maven Central artifacts, protecting against malicious attacks and ensuring dependency trust.
The Risks of Blind Trust in Code from Strangers
Explore the hidden dangers of open-source software and learn effective strategies to detect and prevent supply chain attacks in your daily coding routine.
Attacking Through the Software Supply Chain
Comprehensive exploration of software supply chain attacks, featuring real-world examples and practical solutions to minimize vulnerabilities and protect against emerging threats.
Securing Your .NET Application Software Supply-Chain
Hands-on guide to securing .NET application supply chains, covering source code access, third-party libraries, build servers, and implementing SLSA guidance and SBOM concepts.
What Is Going On In Your Source Code? Understanding Software Component Analysis in Plain Language
Gain insights into software supply chain security concepts like SBOM, VEX, and SLSA, understanding their importance in protecting organizations from emerging security threats.
PEP 740 and PyPI - Bootstrapping Provenance for the Python Ecosystem
Explore how PEP 740 enhances PyPI's security through digital attestations, integrating with Sigstore and SLSA to provide robust package provenance without complex key management.
Helping the PyTorch Community Improve the Security Posture of this Popular AI Framework
Discover how to enhance PyTorch's security through OpenSSF Best Practices, dependency management, and proactive measures for safer AI framework implementation and neural network development.
Open Source Software Supply Chain Security - Understanding Threats and Best Practices
Explore critical threats to open source software supply chains, industry best practices for security, and practical strategies for protecting against vulnerabilities and cyberattacks.

Protecting Software Supply Chains with Hyperledger Fabric
Explore Corsha's Zero Trust solution using Hyperledger Fabric to secure software supply chains. Learn about preventing attacks and protecting critical components through live demonstrations and expert insights.
Security Threat Model Analysis and Protection Practice in Edge Computing
Análisis de modelos de amenazas y prácticas de protección en computación de borde, incluyendo auditoría de seguridad de KubeEdge, iniciativas de mejora y cumplimiento SLSA L3 para fortalecer la seguridad en escenarios de edge computing.
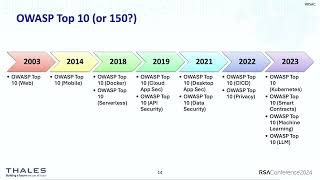
Securing Software Supply Chain - Problems, Solutions, and AI/ML Challenges
Explore software supply chain security, recent attacks, frameworks, and SBOM. Learn risk mitigation strategies and tackle AI/ML supply chain challenges in this comprehensive overview.