In-Toto: Attestations and Software Supply Chain Security
Explore in-toto framework's advancements in software supply chain security, including attestation verification, type mapping, and integrations with CNCF projects and industry tools.
Updates from The Update Framework
Explore The Update Framework's role in secure content delivery, its protection against supply chain attacks, and its evolving ecosystem with insights from TUF maintainers.
The Update Framework (TUF) Maintainer Panel: Integrations, Enhancements, and Supply Chain Security
Panel discussion on The Update Framework: insights on integrations, supply chain security, and open-source project maintenance from TUF maintainers across various implementations and organizations.
Putting the Supply Chain Pieces Together: A Deep Dive into the Secure Software Factory
Explore a deep dive into supply chain security, focusing on implementing CNCF's Secure Software Factory architecture using cloud-native tools to enhance software provenance and artifact trustworthiness.
Securing Your Container Native Supply Chain with SLSA, GitHub and Tekton
Practical guide to securing container native supply chains using SLSA principles, in-toto attestations, and step-by-step demos for achieving SLSA Level 2 in Tekton and Github Actions.
Towards Effective and Scalable Vulnerability Management
Explore challenges and solutions in modern vulnerability management, focusing on automation, exploitability-based prioritization, and frameworks like CSAF and VEX to improve organizational security posture.
Three Things That Each Developer Should Know to Help Secure Code Base
Discover key strategies to enhance code security: SBOM for transparency, Reproducible Builds for verification, and SigStore for signing. Learn practical tools and real-world examples to protect against cybercrime.
Hiding in Plain Sight - The Untold Story of Hidden Vulnerabilities
Uncover limitations of vulnerability scanners and SCA tools through groundbreaking research. Learn about hidden vulnerabilities, scanner blindspots, and the need for holistic software security approaches.
Enforcing Supply Chain Security and Simplifying Compliance Audit for ArgoCD Deployments
Explore techniques for securing supply chains and simplifying compliance audits in ArgoCD deployments using open-source tools like Guac, Sigstore, and in-toto.
SBOMs - Are They a Threat or a Menace?
Explore the implications of Software Bill of Materials (SBOMs) in cybersecurity, examining their potential benefits and challenges for software supply chain management.
Identity-based Source Integrity with Gitsign
Explore Gitsign, a Sigstore project for keyless, identity-based Git commit signing. Learn its benefits over traditional methods and how it enhances security in CI/CD and GitOps workflows.
Security Patch Identification on Open-Source Software
Explore techniques for identifying security patches in open-source software with Dr. Kun Sun, enhancing your ability to assess and mitigate vulnerabilities effectively.
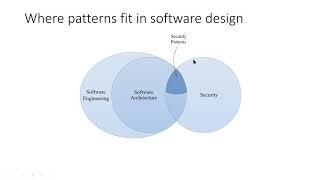
Building Secure Software Systems Using Security Patterns
Learn to create secure software systems using proven security patterns, enhancing your ability to design robust and protected applications in today's cybersecurity landscape.
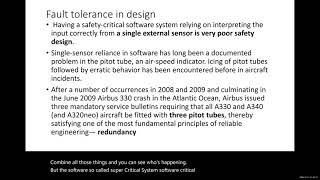
Insecure, Unsafe, and Lying Software
Explore the critical issues of insecure, unsafe, and deceptive software with insights from Eduardo Fernandez of Florida Atlantic University, addressing key cybersecurity challenges.
Growing the Chain: Trusting Build Provenance from Userspace
Explore techniques for establishing trust in CI/CD workflows, focusing on artifact signing, provenance generation, and building a chain of trust using open-source technologies like Sigstore and OIDC.
Implementing OpenSSF Best Practices Badges and Scorecards for Project Security
Learn to enhance open-source project security using OpenSSF Best Practices Badges and Scorecards. Gain practical tips for implementation and addressing common issues to improve your project's security posture.
Smarter Than Your Average SBOM - Understanding the SBOM Lifecycle
Explore the SBOM lifecycle, including creation, storage, distribution, trust verification, and enrichment. Learn about emerging practices and companion formats in software security.
Opening the JAR: The Hitchhiker's Guide to JAR File Dependencies
Explore JAR file dependencies, their complex structures, and various inclusion methods. Learn about edge cases, oddities, and potential vulnerabilities in Java program dependencies.
Automating Architectural Risk Analysis with Open Threat Model Format
Explore automating architectural risk analysis using Open Threat Model format. Learn to create OTM files, integrate threat modeling into DevSecOps, and address challenges in software development security.
OWASP Open Application Security Curriculum
Comprehensive overview of OWASP's initiative to develop an open, standardized application security curriculum for undergraduate and postgraduate education, addressing the skills gap in the security sector.
How to Use Your Vulnerabilities to Train Developers on Security
Learn to leverage your vulnerabilities for targeted developer security training. Discover common coding mistakes, effective fix strategies, and how to create adaptive training plans using real-world examples.