The Cavalry Is Us - Cybersecurity Activism in the Internet of Things Era
Exploring cybersecurity challenges in IoT and the need for collective action. Calls for researchers and professionals to shape the future of digital security and address emerging threats.
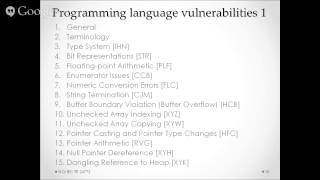
Guidance on Avoiding Programming Language Vulnerabilities - TR24772 Explanation
Overview of ISO/IEC TR 24772:2010, guiding programmers on avoiding vulnerabilities through language selection and use. Insights from a contributor on enhancing software security.
Can AppSec Training Really Make a Smarter Developer?
Explores the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and its impact on application security strategies.
Why Won't Developers Always Write Secure Open Source Software?
Explore challenges and solutions for enhancing open source software security, addressing developer motivations and industry-wide strategies for safer code practices.
Threat Modeling - Key Methodologies and Applications from OSS CIP Perspective
Explore key threat modeling methodologies and their applications in open source civil infrastructure platforms, enhancing security practices for critical systems.
Software Supply Chain Integrity with Sigstore
Learn about Sigstore, a tool for securing software supply chains, with demos on Cosign for signing and verifying artifacts, and insights on its practical applications.
Generating a SPDX SBOM for Your Code in CI Using ORT
Learn to generate SPDX Software Bill of Materials (SBOM) for your code in continuous integration using the OSS Review Toolkit (ORT), enhancing software transparency and security.
Developing Secure Open Source Software - Mentorship Session
Explore best practices for developing secure open source software with expert guidance on risk mitigation, vulnerability management, and collaborative security measures.
The Cedar Language and Policy-Based Authorization - Episode 1
Explore policy-based authorization with AWS scientist Emina Torlak, discussing Cedar language, access control, and separating authorization logic from application code for improved security and management.
Privacy-preserving Approaches to Transparency Logs
Explore append-only transparency logs, their applications in infrastructure, and privacy-preserving techniques to balance immutability with user rights and data protection.
Gitsign - Keyless Git Commit Signing
Explore Gitsign, a Sigstore project enabling keyless Git commit signing. Learn its functionality, integration with Sigstore, and application in development, CI/CD, and GitOps workflows.
Composing the Ultimate SBOM - Creating Accurate and Modular Software Bill of Materials
Explore a modular approach to creating accurate Software Bills of Materials (SBOMs) using Micro-SBOMs, enhancing software security and compliance tracking beyond traditional post-build methods.
Improving Package Repository Security - From White Papers to Practice
Explore package repository security challenges, modern practices, and collaborative solutions for improving community repositories like PyPI and NPM.
Trusted-SBOM - Verifying Software Bill of Materials for Security and Integrity
Explore the importance of verifying Software Bill of Materials (SBOMs) for software integrity. Learn about tools and best practices to ensure SBOM accuracy, comprehensiveness, and trustworthiness.
Making Fuzzing Part of Your Software Development Lifecycle
Learn to integrate fuzzing into software development, exploring tools like libFuzzer, ClusterFuzz, and OSS-Fuzz to enhance security and catch bugs early in open-source and proprietary projects.
Zero-Configuration Runtime Software Component Detection
Discover how to detect vulnerable software components in running systems using eBPF, focusing on Java applications and container images without initial configuration.
From a Security Expert's Diary: DOs and DON'Ts When Choosing Software for Embedded Products
Practical advice on selecting software for embedded products, covering distribution choices, module selection, support assessment, update systems, and security considerations.
5G - Prioritizing Security Now
Explore 5G security strategies, standards, and challenges in virtualized and cloud environments, with insights on cybersecurity and container protection.
Zero-Trust Supply Chain Security with Sigstore, TektonCD and SPIFFE
Explore cutting-edge tools for enhancing software supply chain security, focusing on Sigstore, TektonCD, and SPIFFE implementations in zero-trust environments.
Dependencies: Do's and Don'ts - Managing Application Dependencies Securely
Learn best practices for managing dependencies in software development, balancing security risks with benefits to team velocity and business value. Discover preventive measures to minimize vulnerabilities.
Securing Open Source Software - End-to-End, at Massive Scale, Together
Explore strategies for securing open source software at scale, focusing on collaborative approaches and end-to-end solutions for robust protection in the digital ecosystem.