WingFuzz: Implementing Continuous Fuzzing for Database Management Systems
Continuous fuzzing technique for enterprise-level DBMSs, addressing challenges in SQL grammar, codebase evolution, and anomaly analysis. Discovered 236 bugs across 12 major DBMSs.
LLVM Improvements for Better Verification
Explore LLVM enhancements that facilitate improved code verification, focusing on techniques and strategies for more robust software development.
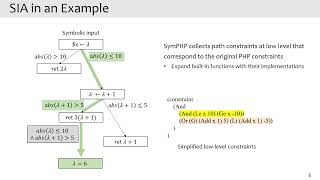
Holistic Concolic Execution for Dynamic Web Applications via Symbolic Interpreter Analysis - 2024
Explore advanced techniques for analyzing dynamic web applications using holistic concolic execution and symbolic interpreter analysis.
Defensive Coding Bootcamp - NDC Melbourne
Learn essential security practices to build robust, hack-resistant software. Explore vulnerabilities, evasive coding techniques, and fundamental principles applicable across programming languages for developers of all levels.
Fueling Open Source Adoption with DevSecOps
Learn strategies for integrating open source securely using DevSecOps principles, addressing concerns, and leveraging tools to maximize benefits while minimizing risks in software development.
Demystifying Open Source Crash Reporter - An In-depth Security Analysis
Explore crash reporting systems, focusing on Ubuntu's Error Tracker. Learn key functions, security implications, and techniques for crash analysis and triage in open-source software.
Matching CVEs and Source Code for Vulnerability Detection
Explore techniques for mapping CVEs to source code, including parsing CVE data and quantifying correspondence statistics. Learn about open-source tools and potential AI applications for vulnerability detection.
Unwinding the Stack for Fun and Profit
Explore stack-based buffer overflow exploitation techniques, bypassing modern mitigations by leveraging exception handling mechanisms to resurrect old exploits and achieve successful attacks.
Orange is the New Purple - How and Why to Integrate Development Teams with Red - Blue Teams to Build More Secure Software
Explore a new paradigm for integrating development teams with offensive and defensive teams to enhance software security throughout the development lifecycle, fostering knowledge sharing and strengthening defenses.
SKF Keeper Project - There Is No Right or Wrong, Only Fun and Boring
Explore secure software development with SKF Keeper, an open-source platform offering defensive coding, offensive testing, and infra security tracks. Learn to prevent vulnerabilities and elevate AppSec maturity.
Protecting the World's Greatest Open Source Ecosystem with Sigstore
Explore Sigstore, an OpenSSF project enhancing software supply chain security. Learn to sign and verify Maven Central artifacts, protecting against malicious attacks and ensuring dependency trust.
PGP vs Sigstore - The Match at Maven Central
Exploring sigstore as an alternative to PGP for signing and verifying Maven Central artifacts, promising easier key management and improved software supply chain security.
Protecting Your Organisation Against Attacks via the Build System
Explore build system security risks and mitigation strategies, including dependency verification, checksums, vulnerability detection, and build reproducibility. Learn to safeguard your development process.
How to Gain Value from SAST Tools in SDLC - Most Common Findings and Mitigations
Explore SAST tools for secure software development, covering common findings and mitigations. Learn to integrate security checks early in the SDLC and prioritize critical issues for improved code security.
The Goodness is Baked In - Baking Assurance into Software
Learn techniques to integrate security assurance into software development, covering key legislation, essential components, and practical implementation strategies for robust cybersecurity.
Defensive Coding Bootcamp
Learn essential security practices and defensive coding techniques to build more secure software across all programming languages.
Defensive Coding Bootcamp
Learn essential security practices to build robust, hack-resistant software. Explore vulnerabilities, evasive coding techniques, and fundamental principles applicable across programming languages.
How Hacking Works
Explore software exploitation, hacking techniques, and tools in this talk. Learn to secure systems through gamified environments and build skills for safer software development.
What Is a Software Security Initiative and Do I Need One
Explore building blocks for successful software security initiatives, balancing finding, fixing, and preventing issues. Learn strategies to enhance your AppSec program and avoid common pitfalls.
Explosive Overflow: Lessons in Software Design from Rocket Science
Explore software design lessons from the Ariane 5 rocket failure, examining testing, validation, and security principles to prevent catastrophic system failures in critical applications.
What Is Going On In Your Source Code? Understanding Software Component Analysis in Plain Language
Gain insights into software supply chain security concepts like SBOM, VEX, and SLSA, understanding their importance in protecting organizations from emerging security threats.