Mind the Bridge - A New Attack Model for Hybrid Mobile Applications
Unveils a novel attack model for hybrid mobile apps, exploiting JavaScript bridges. Presents vulnerability models, explores embedded browser architecture, and proposes mitigation strategies for enhanced security.
Software Security Era - Past, Present, and Future
Explore the evolution of memory corruption exploitation, from early techniques to modern mitigations. Includes live demos of vulnerabilities and discusses the ongoing challenges in software security.
Pwning ARM Debug Components
Exploring ARM debug components for security primitives and information flow tracking. Demonstrates a portable approach to enhance runtime security monitoring in ARM-based systems.
Exploiting GLIBC - Hacking Everything
Exploración detallada de la vulnerabilidad CVE-2015-7547 en glibc, demostrando técnicas de explotación remota y su impacto en diversos productos de software compilados con versiones antiguas.
Don't Feed The Hippos
Exploring common failures in security communication with developers, this talk offers insights on avoiding 'insecure hippos' and provides best practices for effective collaboration in software security.
Hack In The Studio - Fireside Chat
Fireside chat with security experts Cristofaro Mune and Adam Laurie, discussing their extensive experience in hardware hacking, embedded systems security, and reverse engineering techniques.
TaintART - A Practical Multi-level Information-Flow Tracking System for Android RunTime
Explore a practical multi-level information-flow tracking system for Android RunTime, enhancing mobile security through advanced taint analysis techniques.
Real-World Post-Quantum Cryptography - Introducing the OpenQuantumSafe Software Project
Explore OpenQuantumSafe, an open-source library for quantum-safe cryptography, including implementations, benchmarks, integration challenges, and future developments.
About Directed Fuzzing and Use-After-Free - How to Find Complex & Silent Bugs
Explore directed fuzzing techniques for targeted vulnerability detection, focusing on bug reproduction and patch-oriented testing to uncover complex and silent software flaws.
Weak Analogies Make Poor Realities
Exploring the shift from viewing cybersecurity as risk to security debt, challenging traditional paradigms and proposing a new approach to articulate and measure software security benefits.
Software Security Austerity - Software Security Debt in Modern Software Development
Explore software security debt in modern development, its sources, management strategies, and consequences with expert insights on risk assessment and mitigation techniques.
Practical AppSec - Quick Wins for More Secure Software
Practical steps to enhance application security with minimal effort, including quick wins, finding attack surfaces, and engaging developers. Introduces a software security maturity model for measuring progress.
Problems You'll Face When Building a Software Security Program
Learn strategies to overcome common challenges in implementing software security programs, including dev process integration, team engagement, and vulnerability management.
Rugged Software Engineering
Practical strategies for rapid and secure software development, addressing challenges in modern engineering organizations and emphasizing continuous deployment, vendor alerts, and language safety.
How to Influence a Developer to Write Secure Code in 10 Minutes
Discover effective strategies to quickly motivate developers to prioritize secure coding practices, enhancing overall software security in just 10 minutes.
Software Security - Is OK Good Enough
Explore software security challenges and determine if "OK" is sufficient in today's threat landscape. Gain insights on balancing security with practicality.
Why Do Developers Make Dangerous Software Errors
Explore why developers create risky software, the importance of secure coding practices, and strategies for implementing effective software assurance in modern technology development.
Compiler-assisted Code Randomization
Explore compiler-assisted code randomization as a defense against return-oriented programming exploits, balancing security with software distribution norms and maintaining compatibility.
The Correctness-Security Gap in Compiler Optimization
Explores how compiler optimizations can preserve functionality but violate security guarantees, proposing research to identify and mitigate security errors introduced during optimization.
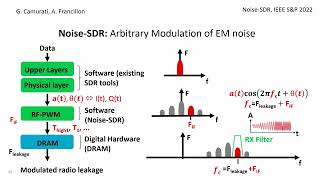
Noise-SDR - Arbitrary Modulation of Electromagnetic Noise from Unprivileged Software and Its Impact on Emission Security
Explore how unprivileged software can modulate electromagnetic noise, affecting emission security. Discover potential implications for data protection and system vulnerabilities.
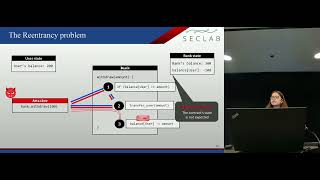
SAILFISH - Vetting Smart Contract State-Inconsistency Bugs in Seconds
Discover a groundbreaking technique for rapidly identifying state-inconsistency vulnerabilities in smart contracts, enhancing blockchain security and reliability.