Exploring a Risk Approach to Software Supply Chain Security
Explore software supply chain security through a risk-based approach, focusing on open source vulnerabilities and process improvements to mitigate supplier risks.
SBOMs: Zero to Hero - A Comprehensive Guide
Discover SBOMs: definition, importance, contents, creation methods, and open-source tools. Explore integration challenges and solutions in build processes.
How Your Brain Processes Code - A Cognitive Perspective on Programming
Explore cognitive aspects of programming, understanding how the brain interprets code to enhance reading and learning new languages. Gain insights for improved code interaction.
SLSA - A Supply Chain Security Framework
Explore SLSA framework for securing software supply chains, mitigating vulnerabilities, and ensuring code integrity from development to deployment.
Reviewing NuGet Packages Security Using OpenSSF Scorecard
Explore OpenSSF Scorecard for assessing NuGet package security. Learn to evaluate maintenance, workflows, and security tools to improve application safety and make informed decisions.
Counting Down for CRA - Updates and Expectations
Explore the EU's Cyber Resilience Act: timeline, critical discussions, and new responsibilities for software developers. Learn about PSF's preparations and how to ready your Python projects for increased security liability.
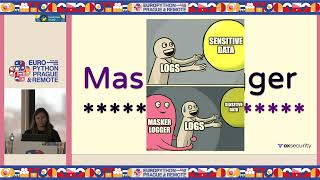
Secure Logging Practices: Protecting Sensitive Information in Python Applications
Explore secure logging practices to protect sensitive data in Python applications. Learn to identify, redact, and safeguard confidential information from accidental disclosure in log files.
Intellectual Property Law 101 for Developers
Demystify essential legal concepts for developers: trademarks, copyrights, and patents. Learn to secure your code and understand the consequences of your actions through real-life examples.
Mastering Data Fabrication: Enhance Testing and Protect User Privacy with Python
Generate realistic, fictitious data for enhanced application testing while adhering to privacy standards. Master tools like Faker to create diverse data types and ensure compliance.
ID, EGO and Super EGO of Your Entity - Performance and Identity Management
Explore entity identifier management in business applications, examining performance impacts and innovative solutions for efficient code development and maintenance.
CCLAS and Fusion Integration - Combining LIMS and GDMS
Explore CCLAS and Fusion integration for seamless data transfer between LIMS and GDMS. Enhance efficiency, accuracy, and collaboration in mining operations through real-time synchronization.
The Joy and Excitement of Forbidden Computing - Closing Keynote
Explore hardware hacking and low-level engineering with Kate Temkin. Discover empowering educational technology and insights into USB development, reverse engineering, and hardware hacking.
Gravitino: A Multi-Regional, Geo-Distributed Meta Datalake
Discover Gravitino, a unified solution for multi-regional metadata management. Simplify data access, enhance security, and streamline processes with this geo-distributed meta datalake.
Mentorship Programs: Growing New Team and Community Leaders
Explore strategies for effective mentorship programs to cultivate community leaders, foster contributor growth, and enhance team bonding in open-source projects.
Impact Framework: Open-Source Tool for Quantifying Environmental Impact of Software
Quantify software's environmental impact using Impact Framework, an open-source tool. Learn its history, core concepts, and practical application through a live demonstration.
Allyship - Powering Up Diversity in Open Source
Aprenda a ser um aliado eficaz para impulsionar a diversidade e inclusão em projetos de código aberto, promovendo mudanças positivas e um ambiente mais equitativo.
Testing Your Yocto Project - From Ptest and Testimage to LAVA
Explore Yocto Project testing options, from simple setups using testimage and ptest to complex frameworks like LAVA. Learn integration techniques and alternatives for various project scales.
The Current Situation of SBOM in Japan
Explore Japan's SBOM adoption progress, including METI guidelines, implementation challenges, and the evolving landscape of software supply chain security in Japanese companies.
Bridging the Dev-Sec Divide: Three Tips for Agile Developers
Discover proven steps to build and grow a DevSec culture in your tech organization, bridging the gap between development and security teams.
Codifying Privacy: How to Follow Through On Your Privacy Promises
Learn practical approaches to implement privacy promises in software development, focusing on embedding privacy in CI/CD pipelines and overcoming common hurdles to ensure data handling aligns with user-facing policies.
Security Posture Assessment and Improvements for Open Source Projects
Explore essential security practices for open source projects, including fuzzing, SBOM, and SSDLC. Learn to assess vulnerabilities and maintain robust security postures through real-world examples.