Introducing OpenChain Japan Community's SBOM Initiatives
Explore Japan's SBOM initiatives, SPDX 3.0 contributions, and future outlook. Gain insights on software supply chain security, practical SBOM adoption, and global implications for stakeholders.
Open Source Projects in Safety Critical Applications
Explore open source projects in safety-critical applications with industry experts, discussing challenges, best practices, and future trends in this critical domain.
An Open-Source Implementation for Linked-Data-Based Verifiable Credentials with Selective Disclosure and Zero-Knowledge Proofs
Explore an open-source implementation of Linked-Data-based verifiable credentials, enabling secure digital identity management with selective disclosure and zero-knowledge proofs.
Eliminating the Unknowns: Using GUAC to Better Understand Your Software Supply Chain
Learn how GUAC, an open-source knowledge graph, aggregates software supply chain metadata to enhance security, inform decision-making, and enable policy-driven admission control in your development lifecycle.
The Evolution of SBOMs in AlmaLinux
Explore AlmaLinux's SBOM generation process, its evolution to meet NTIA requirements, and the implications for RPM-based Linux distributions. Learn about challenges and solutions in software supply chain security.
Beyond Guidelines - Designing and Implementing Robust Build Pipelines
Learn to design and implement secure build pipelines beyond standard guidelines. Explore practical tools and methods to enhance supply chain security and protect against rising attacks.
Fully Automated Power Measurement Solution with IC Temperature Control
Explore automated power measurement and temperature control for embedded Linux platforms, featuring innovative solutions for characterization and Operating Performance Points optimization.
PipeWire - The New Multimedia Service Ready for Automotive
Explore PipeWire's evolution into a robust multimedia service for automotive applications, featuring enhanced audio-video capabilities and industry-ready performance.
Telcos Move From Blackboxes to Open Source - Linux Foundation Networking
Explore how Linux Foundation Networking is driving open source adoption in the telco industry, transforming traditional closed systems into innovative, transparent solutions.
Finding Vulnerabilities in Your Codebase Using Open Source Tools
Explore open-source tools for identifying vulnerabilities in your codebase. Learn effective techniques to enhance software security and protect against potential threats.
No Code Malware - Windows 11 at Your Service
Explore Windows 11 vulnerabilities and no-code malware techniques in this DefCamp 2023 presentation by Inbar Raz, VP of Research at Zenity. Learn about emerging cybersecurity threats and defense strategies.
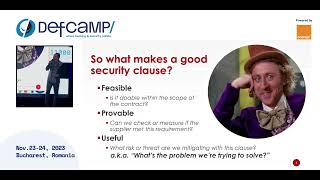
AppSec Contractual Sins - Identifying and Addressing Security Issues in Contracts
Explore common AppSec contractual pitfalls and best practices for securing software development agreements in this DefCamp 2023 presentation by Canon's EMEA Information Security Manager.
Navigating the Software Supply Chain Defense Landscape
Explore software supply chain security tools and frameworks, their integration, and how to select the right combination for comprehensive protection against rising cyber threats.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security strategies for new technologies, emphasizing the importance of product security in today's cyber landscape and the need for innovative, affordable approaches.
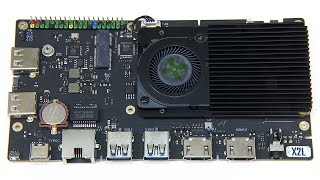
Radxa X2L - Low-Cost x86 SBC with RP2040 Review and Demo
Comprehensive review of Radxa X2L, an x86 single board computer with RP2040 microcontroller. Covers unboxing, specs, performance tests, and unique features like onboard Raspberry Pi Pico functionality.
Structured Scorecard Results: Tailor Your Own Supply-Chain Security Policies
Learn to customize OpenSSF Scorecard for tailored supply-chain security assessments using Structured Results feature. Explore practical examples and use cases for automated policy-driven analysis.
Practical SBOM Management with Zephyr and SPDX
Learn to identify, assess, and manage software components in Zephyr applications using SBOM standards and tools. Enhance security practices and respond effectively to vulnerabilities in embedded systems.
The 5 Ws and H of Open Source Community - Panel Discussion
Experts discuss the 5 Ws and H of open source communities, exploring key aspects, real-world examples, and how to get involved in this dynamic ecosystem.
The Past, Present, and Future of Cross-Site and Cross-Origin Request Forgery
Explore the evolution of Cross-Site Request Forgery attacks, their impact on applications, and effective defense strategies. Learn about vulnerabilities in API-based systems and best practices to prevent CSRF.

OWASP Juice Shop - An Open Source Software and Security Fairytale
Explore the evolution of OWASP Juice Shop, a pioneering hacking training platform, from its inception as a pet project to becoming an OWASP Flagship project, with insights into its future developments.
The End of DevSecOps? - Leveraging New Tools and AI in Engineering-First Security
Explore how Generative AI and new tools can simplify communication, reduce toil, and integrate security seamlessly into engineering processes, moving beyond traditional DevSecOps.