Demystifying SBOMs: Strengthening Cybersecurity Defenses
Explore Software Bill of Materials (SBOMs) as a crucial tool for enhancing cybersecurity, identifying vulnerabilities, and managing software supply chain risks in organizations.
OWASP IoT Security Testing Guide (ISTG)
Comprehensive guide for IoT security testing, covering methodologies and best practices to identify vulnerabilities and enhance device protection in the interconnected world.

CrowdStrike IT Outage Explained - Kernel Mode Driver Analysis
Detailed analysis of CrowdStrike's IT outage from a Windows developer's perspective, focusing on kernel mode drivers and system vulnerabilities.
Creating Better Computer Systems by Focusing on Sustainability
Explore practices to increase sustainability in software development, focusing on simple changes to create better, more environmentally-friendly products while improving system performance.
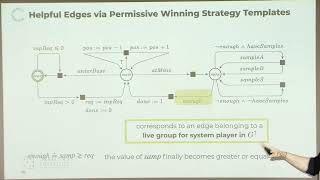
Localized Attractor Computations for Infinite-State Games
Explore symbolic methods for solving infinite-state games, focusing on localized attractor computations in sub-games to enhance efficiency and tackle complex problem instances.
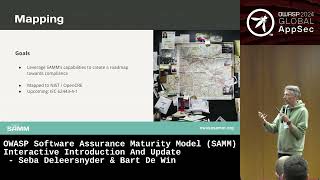
OWASP SAMM - Interactive Introduction and Update
Explore OWASP SAMM, a framework for software assurance maturity modeling, with interactive insights and updates from industry experts.
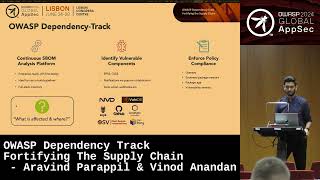
OWASP Dependency Track - Fortifying the Software Supply Chain
Explore strategies to secure software supply chains using OWASP Dependency Track, a powerful tool for identifying and mitigating vulnerabilities in third-party components.

Gaining Initial Access by Exploiting Leaked Credentials
Explore how attackers exploit leaked credentials to breach organizations and learn effective prevention strategies for safeguarding sensitive information.
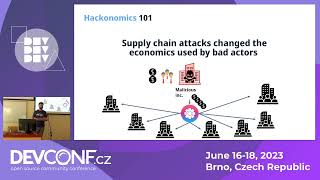
The Internet is Broken: Breaking Down the Software Supply Chain
Explore modern software vulnerabilities, recent supply chain attacks, and actionable steps to build secure applications in an insecure internet environment.
Jumpstarter: Enabling Open Hardware-in-the-Loop Testing
Automate embedded software testing with Jumpstarter, integrating hardware-in-the-loop into CI/CD pipelines for faster, more consistent results. Explore the dutlink-board and its expandable functionality.
Walking the PEB, Enhancing IDA's Output with Structures, and Unlocking Runtime-Linking - Lecture 4
Explore PEB usage in malware, learn runtime DLL location techniques, and enhance IDA analysis with custom structures for improved reverse engineering.
Hardware Security I - CHES 2024
Explore hardware security topics presented at CHES 2024, chaired by Jan Richter-Brockmann. Gain insights into cutting-edge research and developments in the field of cryptographic hardware and embedded systems.
Securing the Software Supply Chain - SBOMs and Their Impact
Explore software supply chain security, SBOMs, and their impact on open source. Learn about transparency challenges and the potential effects of the Cyber Resilience Act.
Open Source Robotics with Python - Learn Robotics with No Robot Required
Explore robotics simulation using Python, ROS 2, and Gazebo. Learn to develop robot code without hardware, leveraging open-source tools used by professionals in the field.
Unpacking Open Source Security in Public Repositories
Explore open source security challenges in public repositories and learn strategies to mitigate risks in cloud-native environments.
Hunting Fileless Malware with Treesitter
Explore advanced techniques for detecting obfuscated, fileless malware using Treesitter parser generator library. Learn to create scalable and accurate detections for malicious PowerShell and Bash payloads.
Leveling Up Ghidra - Learn Ghidra Plugins with Game Boy Game Reverse Engineering
Explore Ghidra plugin development for efficient reverse engineering, using Game Boy games as an engaging example to showcase automation possibilities and enhance RE skills.
The SaaS-y Side of Incident Response - Key Log Sources for Okta, GitHub, and Salesforce
Explore key log sources for Okta, GitHub, and Salesforce in cloud-based incident response. Learn to interpret SaaS logs, avoid common pitfalls, and improve detection strategies for effective security management.
DevSecOps: Connecting Developers, Security, and Operations
Explore DevSecOps methodology, connecting developers, security, and operations. Learn about tooling, cloud security automation, and the importance of continuous learning in fostering a collaborative DevSecOps culture.
Secrets Scanning Techniques and Tools
Explore secret scanning techniques using GitLeaks, truffleHog, and orchestration with AWS Lambda, AWS Code Build, or Secure Codebox. Learn through fun comic-style explanations.
Reproducible Builds with BuildKit for Software Supply Chain Security
Learn how BuildKit enables reproducible builds to enhance software supply chain security, ensuring verifiable and trustworthy Docker images through bit-for-bit identical reproduction from source code.