The Road Towards 365 Bugs in Microsoft Office 365
Discover vulnerabilities in Microsoft 365 applications, including cross-tenant privacy leaks, SQLi, CSRF, SSRF, and XSS. Learn bug hunting techniques and tips for testing new Office 365 features.
A Review of Modern Code Deobfuscation Techniques
Explore modern code deobfuscation techniques, from basic analysis to advanced semantic-based methods. Learn limitations of syntactic approaches and discover state-of-the-art program synthesis techniques.
Fuzzing Javascript Engines for Fun and Pwnage
Discover methods for finding vulnerabilities in Javascript Engines through fuzzing techniques, including crash classification, parallel fuzzing, and custom pattern generation for enhanced web browser security.
Fuzzing the Windows Kernel
Explore Windows kernel fuzzing architecture, from test-case generation to crash collection. Learn about distributed fuzzing design for effective scaling in this insightful presentation on kernel security.
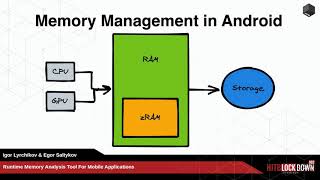
Runtime Memory Analysis Tool for Mobile Apps
Runtime memory analysis tool for mobile apps, automating common checks during penetration testing. Simplifies reverse engineering of obfuscated code for iOS and Android, tracking app behavior changes in real-time.
Introducing ARM-X - The ARM IoT Firmware Emulation Framework
Explore ARM-X, an IoT firmware emulation framework for testing and vulnerability discovery. Learn its evolution, use cases, and future directions in IoT security research and development.
Compiler Bugs and Bug Compilers
Explore compiler vulnerabilities and malicious modifications in GCC, from accidental bugs to intentional exploits. Learn about compiler stages, potential attack vectors, and strategies for detecting malicious alterations.
HDMI - Pwning HDMI For Fun And Profit
Explore HDMI vulnerabilities through protocol analysis, fuzzing techniques, and real-world exploitation, showcasing potential security risks in AV devices and demonstrating practical attack vectors.
Spanish Fly - Infecting Files On-The-Fly
Explore advanced file infection techniques and on-the-fly malware insertion methods with cybersecurity expert Leonardo Nve in this in-depth technical presentation.
Rooting Routers Using Symbolic Execution
Explore advanced techniques for exploiting router vulnerabilities using symbolic execution, uncovering potential security flaws in network devices.
Creating Browser Extensions to Hunt for Low-Hanging Fruit
Learn to create browser extensions for identifying security vulnerabilities, focusing on low-hanging fruit and efficient hunting techniques.
Attacking Software Tokens
Exploring vulnerabilities in software OTP tokens, demonstrating reverse engineering techniques and exploits for major vendors' tokens, and assessing obfuscation effectiveness.
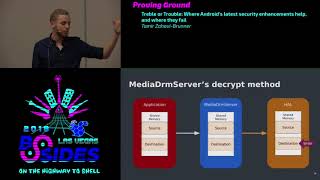
Treble or Trouble - Where Android's Latest Security Enhancements Help And Where They Fail
Explore Android's security enhancements, focusing on Project Treble's impact. Analyze SELinux, Stagefright, and MediaDrmServer vulnerabilities to understand where improvements succeed or fall short.
Don't Ship a Product, Ship Value - Start Your Minimum Viable Product With a Solution
Learn strategies to create a successful minimum viable product by focusing on delivering value and solutions in game or software development.
Time Travel Debugging JavaScript Applications
Explore time travel debugging for JavaScript applications, learning to pause, rewind, and fast-forward execution to efficiently investigate and resolve common bugs using Replay.io.
Automated Testing of Gameplay Features in 'Sea of Thieves'
Discover how automated testing improved 'Sea of Thieves' development and learn its potential benefits for other game studios and developers.
Assassin's Creed Origins - Monitoring and Validation of World Design Data
Explore Ubisoft's innovative approach to world design data management in Assassin's Creed: Origins, featuring automated tests and visual reports for efficient team communication and quality assurance.
Hack In The Studio - Fireside Chat
Fireside chat with security experts Cristofaro Mune and Adam Laurie, discussing their extensive experience in hardware hacking, embedded systems security, and reverse engineering techniques.
When Fuzzing Meets SAP Network Services
Exploring fuzzing techniques for SAP network services, overcoming challenges in performance, protocol complexity, and crash reproduction to discover critical vulnerabilities in custom network protocols.
Summer of Fuzz - MacOS
Explore overlooked attack surfaces on macOS through fuzzing techniques. Learn to bypass security protections, debug effectively, and use new tools for crash triage in Apple core apps and services.
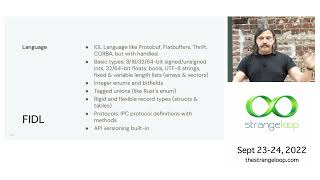
An IPC Language for the Whole Operating System
Explore Fuchsia's innovative FIDL system for unified API and ABI boundaries across the entire OS stack, from kernel to GUI apps, discussing its benefits and challenges.