Bugrank - A Community Bug Bounty Platform
Introducing Bugrank: an open-source community bug bounty platform. Explore its design, architecture, and functions. Learn how to set up your own bug reporting system for enhanced cybersecurity.
Fuzzing File System Implementations to Uncover Security Bugs
Explore file system vulnerability research through fuzzing techniques on BSD systems. Learn to identify attack surfaces, automate testing, and uncover security bugs in kernel implementations.
Open Source Security – Vulnerabilities Never Come Alone
Explore open source security challenges, variant analysis techniques, and real-world case studies. Learn about vulnerabilities in popular software and gain insights from industry expert Fermin J. Serna.
LoRaWAN Auditing
Comprehensive guide to LoRaWAN security auditing, covering vulnerabilities, testing methods, and new tools. Provides practical insights for securing IoT deployments in smart cities and industries.
Reimplementing Local RPC in .Net
Reimplementing Windows RPC in .NET for privilege escalation, covering ALPC implementation, NDR parsing, and PowerShell integration. Includes bug discovery and tooling demonstration.
Over the Edge - Pwning the Windows Kernel
Exploración detallada del subsistema gráfico de Windows, vulnerabilidades del kernel y técnicas de escape del sandbox de Edge, con demostraciones de exploits para elevar privilegios desde el proceso de contenido de Edge a SYSTEM.
ProdSec - A Technical Approach
Explore product security strategies, including risk management, automation, and attack surface reduction. Learn how to integrate security into development processes and foster a security-conscious culture within organizations.
Go Speed Tracer - Guided Fuzzing
Explore advanced guided fuzzing techniques for vulnerability discovery, including code coverage analysis, constraint solving, and feedback mechanisms. Learn about novel tools and approaches in dynamic analysis.
Kernel Exploit Hunting and Mitigation
Explore kernel exploit hunting and mitigation techniques, focusing on identifying and analyzing malware that leverages Windows kernel vulnerabilities for system compromise and evasion of security measures.
Pentesting ChatOps
Explore ChatOps for penetration testing: streamline workflows, automate tasks, and enhance team collaboration using chatbots and custom scripts in a distributed environment.
Security Design and High Risk Users
Security design for high-risk users: understanding human outcomes, adversary capabilities, and synthesizing solutions. Explores challenges and practical processes for improving security beyond code and systems.
DCART - Decoupled Components for Automated Ransomware Testing
Explore a framework for controlled ransomware testing, focusing on decoupled components for detonation and detection. Learn about design, development, and automated testing methodologies for behavioral ransomware analysis.
Hourglass Fuzz - A Quick Bug Hunting Method
Introducción a Hourglass Fuzz, un método rápido de búsqueda de errores para Android que supera las limitaciones de los sistemas de fuzzing típicos, con ejemplos de vulnerabilidades descubiertas en controladores gráficos y Bluetooth.
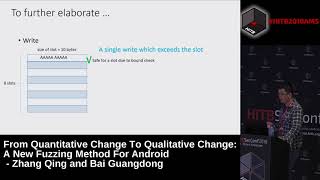
A New Fuzzing Method for Android
Innovative Android fuzzing method combining function points to find vulnerabilities. Proven effective with 50+ bugs discovered on major OEM devices, inspiring new approaches in mobile security research.
Static Binary Analysis - The Essentials
Dive into reverse engineering and static malware analysis essentials with Igor Kuznetsov. Learn visual inspection, disassembly techniques, and structure analysis using IDA Pro and Ghidra.
Web Applications Bug Hunting - Fundamentals
Explore web application security fundamentals, attack vectors, and tools for bug hunting. Learn key concepts to kickstart your career in application security.
Zebrocy’s Multi-Language Malware Salad
Explore Zebrocy's unique APT tactics, multi-language malware, and evolving techniques in this cybersecurity analysis by Kaspersky's Kurt Baumgartner.
Evading Anti-APT Technologies
Learn advanced techniques to bypass anti-APT technologies, including sandbox weaknesses, timing attacks, and dynamic analysis. Gain insights into evading endpoint security and improving your cybersecurity skills.
Mistakes Made Integrating Security Scanning into CI/CD
Explore common pitfalls and solutions for integrating security scanning into CI/CD pipelines, learning from real-world experiences and best practices.
Introduction to Windows Kernel Mode Debugging
Explore Windows kernel debugging essentials, including symbol servers, BSOD analysis, and live debugging. Learn practical approaches to diagnose CPU issues, deadlocks, and blue screens for improved software security.
Crimeware Chaos - Empirical Analysis of HTTP-Based Botnet C&C Panels
Empirical analysis of HTTP-based botnet C&C panels, exploring design, technologies, and characteristics of crimeware control systems used by cybercriminals for managing botnets and other malicious operations.