Cheaper by the Dozen - Application Security on a Limited Budget
Discover cost-effective application security strategies using open-source tools. Learn to implement OWASP projects, assess risks, and create a robust security program tailored to your organization's needs and budget constraints.
Secure Software Development Framework - An Industry and Public Sector Approach
Explore industry-led framework for secure software development, addressing regulatory challenges, open source, metrics, and emerging technologies like AI in cybersecurity.
Open Source in Security-Critical Environments
Explore best practices for using open-source code securely in critical environments, focusing on DevOps and management strategies for edge, network, and cloud applications.
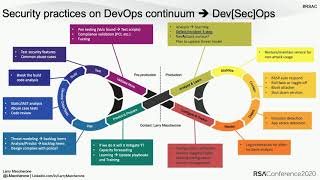
The Impact of Software Security Practice Adoption Quantified
Quantitative analysis of software security practices' impact on risk outcomes, based on data from 200 Comcast teams. Insights on effective strategies for enhancing cybersecurity in diverse tech environments.
When Application Security - The Wrong Way - Is the Right Thing for Your Organization
Discover innovative approaches to application security, including a "credit score" system, an exclusive security champions program, and improved scanning techniques for large-scale IT environments.
Moving 17 Years of Old Legacy Code and Sites into the Cloud
Explore the challenges and solutions of migrating legacy systems to the cloud, covering requirements analysis, decision-making, and sustainable future planning for complex technical environments.
How to Use GitHub Actions with Security in Mind
Comprehensive guide to enhancing GitHub Actions security, covering access control, secrets management, containerization, and best practices for protecting CI/CD pipelines and workflows.
Protect Yourself Against Supply Chain Attacks
Explore supply chain attack vectors, from CI/CD pipeline vulnerabilities to package squatting, and learn protective measures for securing your development environment.
Rethinking Reactive Architectures
Explore reactive architectures: concepts, patterns, and real-world applications. Learn when to leverage this paradigm for building responsive, resilient cloud-native systems.
Best Practices Unit Testing Blazor Components with bUnit
Explore best practices for unit testing Blazor components using bUnit, focusing on creating stable, maintainable tests that improve component quality and development efficiency.
Eventuous Event Sourcing with .NET - NDC Oslo 2021
Explore Event Sourcing in .NET with Eventuous framework through live coding. Learn core concepts, building blocks, and practical implementation for developing event-sourced applications.
Inside a Static Analyser - Type System
Explore C++ static analysis, focusing on type system representation in PVS-Studio. Learn about current implementation, challenges, and upcoming improvements in encoding and handling complex types.
Secure Coding in C and C++ - Volatility Ahead
Explores volatile keyword in C/C++, its uses, semantics, and potential standard revisions. Covers historic context, qualifications, data races, and implementation-defined behavior.
Drone Penetration Testing and Vulnerability Analysis Framework
Explore an open-source framework for drone security testing, covering attack types and vulnerability analysis. Learn to assess and enhance drone safety in various applications.
Access Control Design Best Practices
Learn best practices for designing robust access control systems in web applications, covering anti-patterns, principles, and practical examples for secure implementation.

Coordinated Vulnerability Disclosure - You’ve Come a Long Way, Baby
Explore new research on coordinated vulnerability disclosure, examining perspectives of researchers and organizations to understand behaviors, preferences, and practices in software flaw reporting.
SecDevOps - A Security Pro's Guide to Development Tools
Guía para profesionales de seguridad sobre herramientas de desarrollo, enfocada en empatía, integración de seguridad y métricas para mejorar la colaboración entre equipos de seguridad y desarrollo.
High Performance Fuzzing
Explore advanced fuzzing techniques for enhanced software security, covering target selection, input generation, execution monitoring, and failure detection.
Checklist Pentesting - Not Checklist Hacking
Learn to create a comprehensive pentesting framework for efficient and thorough security assessments, focusing on methodology rather than specific hacking techniques.
Rawr - Rapid Assessment of Web Resources
Explore rapid web resource assessment techniques, including crawling, scanning, and fuzzing, to enhance cybersecurity and identify potential vulnerabilities in web applications.
Planning and Executing a Red Team Engagement
Planning and executing a red team engagement: strategies, tools, and techniques for simulating real-world cyber attacks to assess and improve an organization's security posture and incident response capabilities.